Bengaluru continues to maintain its reputation as a hub of tech and innovation. In fact, Karnataka hosts 18,000 startups and 550 Global Capability Centres (GCCs), based on figures provided by the Karnataka government. Also worth noting is that Karnataka represents 43% of India’s total IT exports. All this is evidence that significant amounts of business conducted out of Karnataka involve technology. In turn, protecting customer and business data is increasingly becoming critical for enterprise assurance as SaaS firms, fintech, IT services firms, cloud computing businesses, and digital platforms expand domestically and overseas.
Organizations located in Whitefield, Electronic City, Koramangala, HSR Layout, Bellandur, Marathahalli, Outer Ring Road, Manyata Tech Park, Indiranagar, JP Nagar, or Jayanagar seeking to establish or confirm operational controls can leverage SOC 2 to assess and document design or operating effectiveness relative to Trust Services Criteria.
Global Quality Services offers Bengaluru-based firms planning SOC 2 Type I or Type II audits comprehensive support, including gap assessment, control documentation, evidence gathering, and readiness review.
What Does SOC 2 Mean for a Bengaluru-Based Business
The SOC 2 audit framework relies heavily on AICPA’s Trust Services Criteria. Unlike a typical security audit, which only checks for a security policy, a SOC 2 audit examines the specific controls a service organization uses to secure its data and operations. Depending on the intended scope of the project, the assessment may address any number of the criteria below:
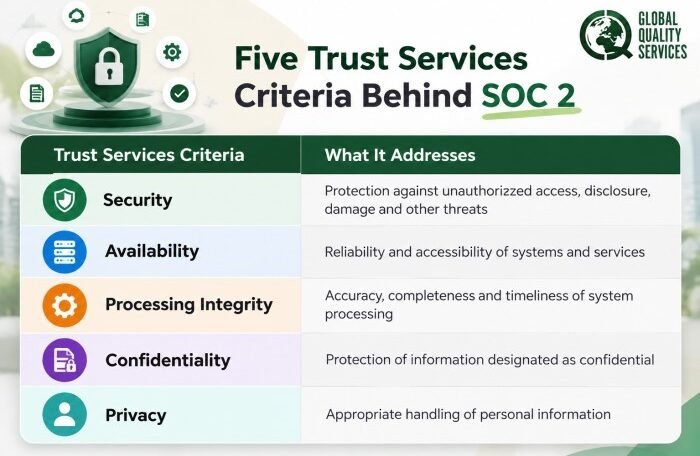
- Security: Safeguards employed against unauthorized access and threats to information and systems.
- Availability: The ability of users to access systems and services consistently.
- Processing Integrity: Processes implemented to ensure information is processed properly and is complete.
- Confidentiality: Controls protecting data classified as confidential.
- Privacy: Data privacy controls covering personal data collection, use, storage, disclosure, and disposal processes.
SOC 2 Type I or Type II? Understand the Difference Before You Start
Determining which type of SOC 2 to pursue should be considered during your SOC 2 engagement planning process. This decision matters.
A SOC 2 Type I report assesses whether the necessary controls are adequately designed and operating as of a specific point in time.
On the other hand, a SOC 2 Type II looks at whether those controls were operating effectively throughout a certain period. Evidence proving effective control operation will need to be provided.
For any Bangalore-based SaaS vendor looking to sign its first enterprise deal, a startup establishing itself globally, or a tech company dealing with stringent information security questionnaires, knowing this upfront will save you headaches down the line.
Why SOC 2 Is Becoming Important for Bengaluru’s Technology Businesses
A company may have strong technical security but still struggle to demonstrate those practices to a prospective enterprise customer. This is where SOC 2 can make a practical difference. A well-prepared SOC 2 engagement can help your organization:
- Demonstrate a structured approach to information security
- Give customers greater visibility into relevant security controls
- Respond more effectively to vendor security assessments
- Support enterprise and international business opportunities
- Establish clearer access management procedures
- Strengthen incident response and monitoring practices
- Improve documentation and accountability
- Identify control gaps before an independent examination
- Establish repeatable processes as the company grows
- Provide documented evidence of control operation
Five Trust Services Criteria Behind SOC 2
A SOC 2 audit uses the Trust Services Criteria framework. However, your organization doesn’t need to comply with every single one of them. Which criteria will apply to your business? That’s determined by your offering, customer demands, and audit goals.
How SOC 2 Preparation Works in Bengaluru
Preparing for a SOC 2 examination gets much simpler once you establish an actionable methodology for your organization. GQS streamlines the process of preparing Bangalore-based businesses from defining scope to being audit-ready.
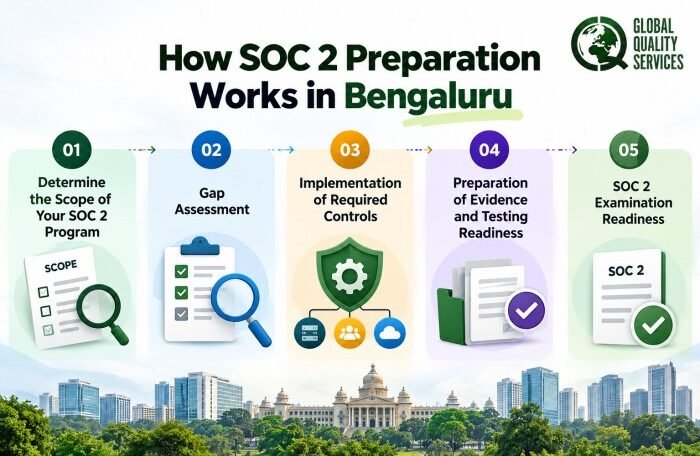
Step 1: Determine the Scope of Your SOC 2 Program
First, we determine which systems, services, teams, and Trust Services Criteria are applicable to your business. That way, your SOC 2 program can prioritize aspects of security that matter most to your clients and operational processes.
Step 2: Gap Assessment
Our team performs an assessment of your existing controls to pinpoint any weaknesses in areas like access control, risk management, incident management, vendor management, and data management.
Step 3: Implementation of Required Controls
Given our assessment results, we assist in implementing stronger controls, policies, processes, and accountabilities to ensure compliance with SOC 2 standards and your operations.
Step 4: Preparation of Evidence and Testing Readiness
Evidence gathering is essential to prove control effectiveness. Our services include helping set up evidence-gathering practices and testing readiness to detect potential problems prior to the audit.
Step 5: SOC 2 Examination Readiness
After implementing required controls and preparing evidence, we guide your team in getting ready for the SOC 2 examination. This includes coordinating requirements and closing gaps.
Business Benefits of SOC 2 Compliance for Bengaluru Businesses
Getting SOC 2-compliant doesn’t just mean updating your security policies. The framework will help you manage customer data and operational processes better.
Gain Trust With Enterprise Clients
Enterprise clients usually require assurances around your security posture before signing up for any services. A SOC 2 certification gives both your sales and compliance teams something to point to.
Enhance Your Vendor Management Program
If your business leverages cloud computing providers, software vendors, infrastructure partners, or other third-party solutions, SOC 2 preparation helps you develop vendor management programs.
SOC 2 Access Management Tips
SOC 2 compliance prompts companies to develop processes to clearly outline access requests, approval decisions, privilege assessments, and termination policies. Improving access management ensures better control over your infrastructure and sensitive data.
SOC 2 Readiness Program Benefits
A readiness assessment allows you to discover vulnerabilities ahead of time, eliminating unexpected surprises during the independent examination process. This will ensure that you avoid costly compliance delays.
SOC 2 Security Assurance for Enterprise Procurement
Indian businesses based in Bengaluru offering SaaS applications, technology services, cloud computing, or professional services abroad should consider security assurance as a vital component of global business expansion strategies.
Internal Accountability Becomes Easier
SOC 2 clarifies who’s responsible for implementing, documenting, testing, monitoring, and responding to incidents related to security controls.
Bengaluru Areas We Serve for SOC 2 Support
Global Quality Services provides SOC 2 consultancy support for organizations across Bengaluru, including businesses operating in:
- Whitefield
- Electronic City
- Koramangala
- HSR Layout
- Bellandur
- Marathahalli
- Outer Ring Road
- Manyata Tech Park
- Indiranagar
- JP Nagar
- Jayanagar
- Banashankari
- Rajajinagar
- Hebbal
- Yelahanka
Which Bengaluru Businesses Can Benefit From SOC 2
SOC 2 is particularly relevant to organizations that provide technology-enabled services or handle customer information on behalf of other businesses. Here is the list of businesses that can take advantage of SOC 2 certification:
- SaaS and Software Companies
- IT and ITES Companies
- Fintech and Financial Technology
- HealthTech and Healthcare Technology
- Cloud and Data Service Providers
- BPO and Outsourcing Companies
- E-commerce and Digital Platforms
- AI and Data Companies
- Global Capability Centres
What Can Make SOC 2 Preparation Difficult
Many organizations do not struggle because they lack security tools. The difficulty often comes from inconsistent processes and incomplete evidence. Common challenges include:
- Scattered documentation: Policies may exist across different teams without a central structure.
- Unclear ownership: Employees may not know who is responsible for individual controls.
- Access management gaps: User privileges may not be reviewed regularly.
- Weak evidence collection: Teams perform activities but fail to retain sufficient records.
- Vendor oversight issues: Third-party security assessments may not follow a defined process.
- Change management gaps: System changes may not be consistently documented and approved.
- Incident response weaknesses: Organizations may have an incident response policy but limited evidence of testing.
- Late preparation: Starting the process too close to the examination can put unnecessary pressure on internal teams.
How Much Does SOC 2 Cost in Bengaluru
No fixed SOC 2 cost applies to every Bengaluru business. The overall investment depends on factors such as:
- Organization size
- Number of employees
- Audit scope
- Number of applications and systems
- Cloud infrastructure
- Selected Trust Services Criteria
- Existing security controls
- Documentation maturity
- Type I or Type II engagement
- Length of the Type II review period
- Level of support required
How Long Does SOC 2 Certification Take
The timeline depends on your existing control environment and the scope of the engagement. Type I and Type II also follow different approaches because Type II requires evidence that controls operated effectively over a defined period. Factors that can affect the timeline include:
- Existing policies and procedures
- Control maturity
- Number of systems in scope
- Number of locations and teams involved
- Evidence availability
- Remediation requirements
- Selected Trust Services Criteria
- Type of SOC 2 report
- Examination schedule
SOC 2 and ISO 27001: Are They the Same
No. Both SOC 2 and ISO 27001 are well-known information security frameworks, but they’re not the same thing.
ISO 27001 is an internationally recognized framework for the development, implementation, maintenance, and continual improvement of an Information Security Management System.
On the other hand, SOC 2 is an assurance framework that assesses control activities according to relevant Trust Services Criteria, culminating in the creation of a report upon completion of the evaluation process conducted by an independent CPA organization.
The choice between using either or both will vary based on business needs, market conditions, contract terms, and overall information security goals.
Why Bengaluru Businesses Work With Global Quality Services for SOC 2 Preparation
Global Quality Services has 26 years of experience in consulting services related to management systems and compliance. Having offices in Bengaluru allows clients to access a local representative when seeking consultancy services. According to published sources, the Bengaluru branch of GQS is located in Banashankari III Stage.
- Bengaluru-based support for businesses across major technology and commercial hubs.
- Experienced consultants with knowledge of SOC 2 requirements and audit expectations.
- Practical recommendations tailored to your business, systems, and customer requirements.
- Support for both SOC 2 Type I and Type II engagements.
- Focus on building effective controls without unnecessary compliance work.
- Clear, responsive guidance throughout your SOC 2 preparation journey.
- Consultancy support designed around enterprise customer and business requirements
Prepare for SOC 2 with Professionals Consultant
Enterprise buyers need proof that your company’s controls live up to its security promises. At GQS, we help Bangalore-based businesses improve their SOC 2 preparedness, identify any control weaknesses, and collect documentation and proof required for an independent Type I or Type II examination. Give your customers peace of mind and enable business growth with our practical SOC 2 solutions. Talk to Global Quality Services now about your SOC 2 needs.
Frequently Asked Questions
1. What firms issue SOC 2 reports in Bangalore?
A SOC 2 report is generated after conducting an examination carried out by an independent licensed CPA firm. GQS can assist companies in becoming SOC 2-ready through assessments and implementation of controls, documentation, and evidence collection. But it doesn’t generate an independent SOC 2 report for its clients.
2. Is SOC 2 required for IT companies in Bangalore?
SOC 2 isn’t a mandated requirement for all IT or SaaS firms. It is optional and dependent on client needs or customer contract requirements.
3. Is SOC 2 preparation possible for startups in Bangalore?
Yes. Startups will need to scope their project appropriately, determine which Trust Services Criteria apply, evaluate their current controls, and develop any required process documentation to enable the examination.
4. Who conducts the SOC 2 audit for Global Quality Services clients?
No. While Global Quality Services can assist your Bangalore-based organization with consultation services related to SOC 2 compliance, the actual SOC 2 examination must always be done independently by a certified CPA firm.
5. Is SOC 2 Type I or Type II preferable for a company in Bangalore?
Neither report format works universally. A Type I examination examines the design and implementation of controls at a single point in time, whereas a Type II examination measures the operational effectiveness of specific controls during a designated timeframe. It depends entirely on the situation and your organizational needs.