As cloud adoption accelerates across Mumbai’s financial and tech hubs, protecting personally identifiable information (PII) in cloud environments has become critical. ISO 27018 Certification establishes robust, international privacy controls for cloud service providers to safeguard sensitive customer data.
With the average cost of a data breach in India reaching an all-time high of ₹25.5 crore, robust cloud data protection is non-negotiable (Economic Times). Hiring an experienced ISO 27018 consultant streamlines your compliance roadmap, bridges technical security gaps, and secures seamless certification without disrupting daily operations.
What is ISO 27018 Certification
ISO 27018 is an extension of the broader ISO/IEC 27001 Information Security Management System (ISMS) standard. While ISO 27001 provides an overall blueprint for information security, ISO 27018 certification focuses specifically on protecting Personally Identifiable Information (PII) in Public Clouds.
It acts as a code of practice for cloud service providers (both PII processors and PII controllers) to ensure they handle customer data lawfully, transparently, and with strict access controls. When you achieve ISO 27018 certification, you demonstrate that your cloud architecture complies with globally recognized privacy principles.
Why is ISO 27018 Important for Businesses in Mumbai
Mumbai is India’s financial and enterprise engine, hosting thousands of technology firms, cloud operators, data centers, and fintech innovators. As cloud adoption surges, so do concerns around data privacy, regulatory compliance, and cross-border data protection.
Here is why ISO 27018 matters for your Mumbai operations:
- Navigating India’s DPDP Act: With India’s Digital Personal Data Protection (DPDP) Act in force, organizations face severe penalties for failing to safeguard personal data. ISO 27018 provides a practical, structured framework to meet these strict statutory duties.
- Global Enterprise Appeal: International enterprise clients require vendor risk assessments before sending data to cloud service providers in India. Having ISO 27018 eliminates friction during vendor onboarding.
- Building Customer Trust: Demonstrating that customer data stored in the cloud won’t be used for unauthorized purposes like advertising or profiling without consent creates a strong competitive advantage.
Step-by-Step Process to Get ISO 27018 Certified
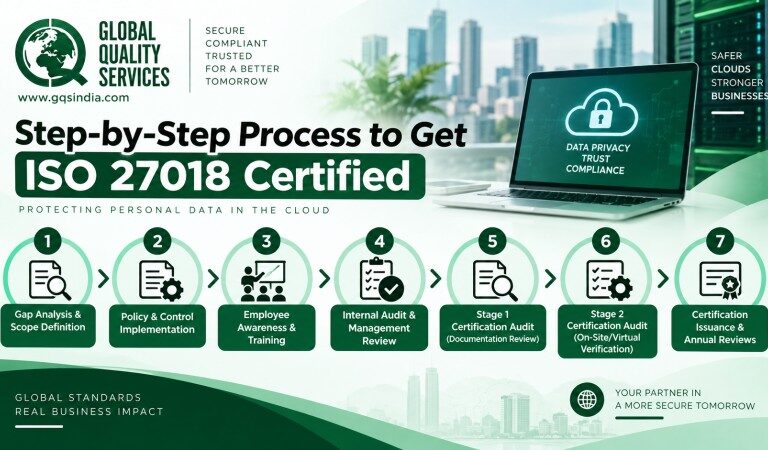
Getting certified doesn’t have to be overwhelming. Following a clear, systematic roadmap ensures a smooth implementation journey:
- Gap Analysis & Scope Definition: Map out your cloud environment, assets, and data flows. Compare your current cloud privacy controls against ISO 27018 requirements to identify missing safeguards.
- Policy & Control Implementation: Develop and update cloud-specific PII policies. Implement technical measures such as robust encryption (at rest and in transit), access restrictions, and automated data destruction protocols.
- Employee Awareness & Training: Train your DevOps, IT operations, and data governance teams on cloud privacy rules, data subject rights, and incident escalation paths.
- Internal Audit & Management Review: Conduct a thorough internal assessment to verify that controls operate effectively in practice. Present the results to leadership to approve any required adjustments.
- Stage 1 Certification Audit (Documentation Review): An accredited third-party certification body reviews your ISMS documentation, PII inventory, and cloud security policies to ensure compliance.
- Stage 2 Certification Audit (On-Site/Virtual Verification): Auditors verify the active implementation of your controls, testing technical systems and interviewing key team members.
- Certification Issuance & Annual Reviews: Upon successful audit completion, you receive your ISO 27018 certification (valid for 3 years, with annual surveillance audits to ensure ongoing compliance).
Benefits of ISO 27018 Certification
Investing in ISO 27018 brings concrete operational and business advantages:
- Enhanced Data Privacy Safeguards: Prevents unauthorized PII disclosure, data leaks, and malicious cloud breaches.
- Streamlined Enterprise Sales: Speeds up Security & Privacy questionnaires during RFP processes for global and local clients.
- Clear Operational Transparency: Ensures your customers know exactly where their data resides, how it’s processed, and how it is protected.
- Reduced Regulatory Liability: Demonstrates due diligence in data protection, lowering risk profile and legal liabilities.
- Stronger Cloud Architecture: Promotes clean data retention, disposal, and backup practices across all cloud hosting models (IaaS, PaaS, SaaS).
Key Requirements of ISO 27018
ISO 27018 builds on ISO 27001 by introducing targeted guidelines for cloud PII processors:
- Customer Consent & Data Limits: PII must never be used for direct marketing or advertising unless explicit instructions and consent are given.
- Data Transparency: Cloud service providers must disclose the geographical locations where PII is stored and processed, as well as any sub-processors involved.
- Strong Encryption Practices: PII transmitted over public networks or stored in cloud databases must be encrypted using strong cryptographic protocols.
- Notification of Data Breaches: Clear procedures must be established to notify affected enterprise clients promptly in the event of a security breach involving PII.
- Data Subject Rights Support: Cloud platforms must provide built-in capabilities allowing clients to fulfill requests like data access, correction, export, or deletion.
Why Choose Global Quality Services for ISO 27018 Certification in Mumbai
Ready to make cloud privacy your competitive edge? Protecting customer data shouldn’t mean drowning in complex compliance paperwork.
At Global Quality Services, our seasoned Mumbai experts turn ISO 27018 certification into a fast, hassle-free process tailored to your cloud setup. We bridge security gaps and build robust privacy controls that win enterprise trust. Secure your cloud and close deals faster. Contact Global Quality Services today for a free expert consultation!
Frequently Asked Questions
1. Is ISO 27001 mandatory before applying for ISO 27018 certification?
Yes. ISO 27018 is an add-on standard extending ISO 27001. Your organization must either hold an active ISO 27001 certification or implement both standards simultaneously in an integrated audit.
2. How long does it take to get ISO 27018 certified in Mumbai?
The timeline typically ranges between 6 to 12 weeks, depending on the size of your organization, the complexity of your cloud infrastructure, and your existing security maturity.
3. Does ISO 27018 apply to private cloud setups?
ISO 27018 specifically focuses on public cloud service providers acting as PII processors. However, organizations operating hybrid or private clouds that host multi-tenant customer environments can also implement these best practices to ensure privacy compliance.
4. What is the difference between ISO 27018 and ISO 27701?
While both standards focus on privacy, ISO 27018 specifically targets cloud-hosted PII and cloud service provider controls. ISO 27701 is a broader Privacy Information Management System (PIMS) standard covering all data processing activities, both online and offline.
5. How much does ISO 27018 certification cost in Mumbai?
Costs vary based on team size, scope of cloud services, and choice of accredited certification body. Contact our team to receive a tailored, transparent cost breakdown for your organization.