The global rollout data from the ISO Survey reveals the continuing growth in the implementation of IT service management standards, with more than 27,000 ISO 20000 certifications currently in operation. Indian IT companies and technology-enabled service firms are under increasing pressure to prove their capability for resiliency and high-level service delivery.
Getting an ISO 20000 certification offers Indian companies a distinct competitive advantage. It enables firms to win important enterprise-level deals and distinguish themselves in international markets. Implementing an officially recognized Service Management System optimizes day-to-day operations in an IT environment. It ensures the absence of service interruption and a commitment to the ongoing process of quality improvement.
What is ISO 20000 Certification
ISO 20000 Certification is a global standard that demonstrates your organization delivers reliable, well-managed IT services. It focuses on building an effective IT Service Management System (ITSMS) that aligns your technology, processes, and teams with business goals. This certification helps you streamline operations, reduce service issues, and maintain consistent service quality for customers.
Why ISO 20000 Matters for Indian Businesses
ISO 20000 matters for Indian businesses because it boosts service reliability, builds global trust, and strengthens competitiveness in the rapidly growing IT marketplace.
- Credibility & Trust: ISO 20000 certification signals to clients, partners, and regulators that your IT services meet rigorous global standards.
- Operational Efficiency: By standardizing processes, you reduce waste and improve reliability.
- Customer Satisfaction: Structured service management helps you consistently meet SLAs, improving satisfaction.
- Competitive Differentiation: In many Indian and global contracts, ISO credentials are increasingly required.
- Risk Management: A formal Service Management System (SMS) helps proactively manage incidents, changes, and service disruptions while supporting compliance with regulations such as India’s Digital Personal Data Protection (DPDP) Act, 2023.
- Integration with Other Standards: ISO 20000 can be integrated with ISO 27001 (information security), ISO 9001 (quality), etc.
Key Benefits of ISO 20000 Certification
ISO 20000 certification delivers stronger service quality, higher efficiency, and better customer satisfaction, helping businesses operate smoothly and stand out in competitive markets:
- Reliable Service Delivery: Build a clear framework that cuts down on unexpected IT issues, clarifies team responsibilities, and keeps communication smooth.
- Better Cost Efficiency: Standardized processes reduce wasted effort and resources, helping your team run operations without unnecessary expenses.
- Stronger Governance: Regular internal checks and management reviews keep your services sharp and focused on continuous improvement.
- Closer IT and Business Alignment: Ensure your technology strategies directly support broader company goals rather than operating in a separate silo.
- Enhanced Market Credibility: Prove your operational maturity to clients and partners, making it easier to win trust and secure global business opportunities.
ISO 20000 Certification Requirements in India
Meeting ISO 20000 requirements in India comes down to establishing practical IT controls that prove your service delivery is reliable and structured. Organizations must fulfill these core conditions before earning the certification:
- Documented Service Management System: Build and maintain a formal framework that clearly outlines every core IT process, policy, and service objective across the organization.
- Defined Service Policies: Establish clear service quality guidelines from leadership that align daily IT operations with broader business goals and customer expectations.
- Standardized IT Processes: Put consistent, repeatable procedures in place for handling incidents, service requests, and system changes with clear accountability for every role.
- Regular Internal Audits: Conduct routine internal evaluations to check how well your team follows the documented procedures and to fix any gaps ahead of the external audit.
- Management Reviews: Hold scheduled leadership meetings to analyze performance metrics, service feedback, and audit results to ensure the management system stays effective.
ISO 20000 Certification Process in India
For organizations in India looking to scale and win enterprise clients, following a clear roadmap makes the entire transition smooth and manageable. Here is what the process looks like:
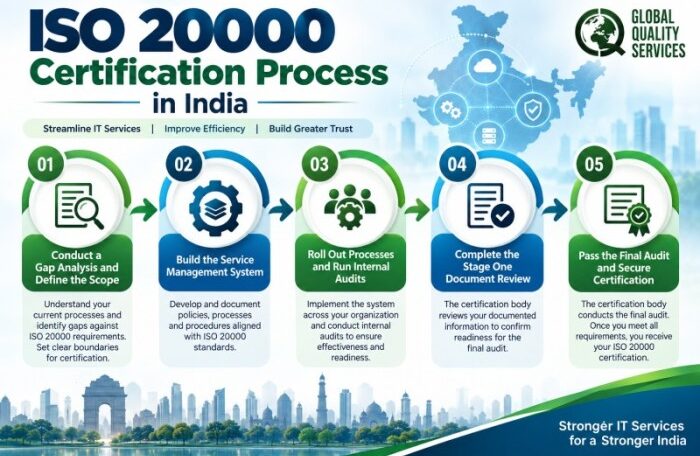
Step 1: Conduct a Gap Analysis and Define the Scope
Start by looking closely at how your team currently delivers IT services and compare those habits against ISO 20000 benchmarks. Map out exactly which departments, locations, and services will fall under the certification so the project stays focused and realistic.
Step 2: Build the Service Management System
Design a practical Service Management System that documents your core workflows, policies, and service level agreements. This phase is about capturing how your team handles incidents, manages changes, and resolves problems every day without adding unnecessary red tape.
Step 3: Roll Out Processes and Run Internal Audits
Introduce the new framework to your team through clear training sessions and put the updated procedures into daily practice. Run a thorough internal audit afterward to catch any operational hiccups and fix them before an external auditor ever steps through the door.
Step 4: Complete the Stage One Document Review
Bring in an accredited certification body to review your policies, documentation, and structural readiness. The auditor checks your paperwork to ensure everything aligns with the standard and points out any policy gaps that need attention before the main evaluation.
Step 5: Pass the Final Audit and Secure Certification
The certification body visits your facility to verify that your documented processes actually match your daily operations. Once you clear any final observations, you receive your official ISO 20000 certificate, backed by straightforward annual checkups to keep the system sharp.
Who Should Consider ISO 20000 Certification in India?
ISO 20000 certification suits IT providers, startups, enterprises, and government teams aiming to improve service quality and strengthen trust in India’s growing tech ecosystem.
- IT Service Providers: Whether you’re a managed service provider (MSP), cloud vendor, or internal IT team.
- Tech Startups & SMEs: Want to scale with credibility and structured service processes.
- Enterprises with Large IT Operations: Looking to reduce incidents, align IT to business goals, or improve governance.
- Government Bodies: As compliance and public trust become more critical, ISO 20000 adds value.
- Companies Bidding for Contracts: Many RFPs now expect ITSM certification as a quality benchmark.
Essential Documents Required for ISO 20000 Certification
Preparing for the ISO 20000 audit requires a few core records to prove your Service Management System works smoothly:
- SMS Scope and Policy
- Service Catalogue and SLAs
- Process Procedures
- Risk Assessments
- Audit and Review Records
Summary Points
- ISO 20000 shows that you manage IT services with a clear, structured, and customer-focused approach.
- It helps you deliver consistent, reliable IT services aligned with business goals.
- The standard improves service planning, monitoring, and continual improvement.
- It reduces service disruptions, incidents, and operational inefficiencies.
- Certification builds client confidence by proving your IT services meet global best practices.
Why Choose Global Quality Services for ISO 20000 Consulting?
Choose Global Quality Services because we simplify your ISO 20000 journey with expert guidance, tailored solutions, and end-to-end support that ensures smooth, successful certification.
- Expert Guidance: Our consultants have deep experience in ITSM and ISO standards.
- Tailored Solutions: We don’t believe in one-size-fits-all we design SMS for your business size, maturity, and goals.
- End-to-End Support: From gap analysis to certification audit readiness, we’re there every step.
- Sustainable Practices: We help you build a system that’s not just certifiable, but genuinely improves your operations long-term.
- ROI-Focused: Our goal is not just to help you certify, but to translate it into better service, lower risk, and business growth.
Accelerate Your IT Service Excellence with Global Quality Services
Ready to streamline your IT workflows and secure high-value enterprise contracts? Partner with Global Quality Services to fast-track your ISO 20000 certification with expert guidance from initial gap analysis to final audit success. Contact our team today to strengthen your operational resilience and build lasting market trust.
Frequently Asked Questions
1. Is ISO 20000 only for IT companies?
No. Although designed for IT service management, ISO 20000 benefits any organisation offering internal or external IT services, helping them streamline operations, improve reliability, and enhance customer satisfaction.
2. How long does ISO 20000 certification remain valid?
ISO 20000 certification is valid for three years, but organisations must undergo annual surveillance audits to maintain compliance, ensure continual improvement, and keep their service management system performing effectively.
3. Does ISO 20000 require companies to follow ITIL?
No, ISO 20000 doesn’t require ITIL, but both align closely. ITIL provides best-practice guidance, while ISO 20000 formally certifies your service management processes, strengthening structure and operational consistency.
4. Can small businesses benefit from ISO 20000 certification?
Yes, small businesses benefit through improved service efficiency, reduced incidents, stronger client trust, and better operational control, especially when competing for contracts that demand globally recognised IT service standards.
5. What documents are needed for ISO 20000 certification?
You need policies, procedures, service management plans, incident logs, change records, audit reports, and performance metrics that demonstrate your IT service processes follow ISO 20000’s required standards.