India’s logistics costs were estimated at 7.97% of GDP for 2023–24, with total logistics costs reaching approximately ₹24.01 lakh crore, according to the latest assessment by DPIIT and NCAER. This highlights the scale and importance of India’s logistics ecosystem and the need for organizations to strengthen security, resilience, and risk management across their operations.
ISO 28000:2022 Certification in India helps organizations establish a structured security management system to identify, manage, and control security risks that can affect their operations, assets, people, and supply-chain activities.
The standard provides a framework that organizations of different sizes and sectors can apply, including logistics, transportation, manufacturing, warehousing, distribution, and international trade.
What Is ISO 28000:2022 Certification?
ISO 28000:2022 is an international standard titled Security and resilience – Security management systems – Requirements.
It specifies requirements for establishing, implementing, maintaining, and continually improving a security management system, including security aspects associated with supply-chain activities.
The standard is not restricted to one particular industry. Commercial organizations, government agencies, non-profit organizations, and other entities can apply it when they need a structured approach to managing security risks.
Why Is ISO 28000:2022 Certification Important in India?
Indian businesses often operate through complex networks involving suppliers, manufacturers, warehouses, transporters, ports, distributors, and customers.
A security incident at any point in this network can affect deliveries, assets, personnel, information, business continuity, and customer commitments.
ISO 28000:2022 provides a systematic framework for identifying these risks and establishing appropriate security controls.
Better Supply Chain Security
Organizations can identify security risks across relevant supply-chain activities and establish controls to address them.
Improved Risk Management
A structured security management system helps organizations evaluate potential threats and choose suitable measures to reduce security-related risks.
Greater Operational Resilience
Organizations can strengthen their ability to prepare for and respond to security-related disruptions affecting business operations.
Improved Customer Confidence
A recognized security management framework can demonstrate that an organization takes operational and supply-chain security seriously.
ISO 28000:2022 Certification Process in India
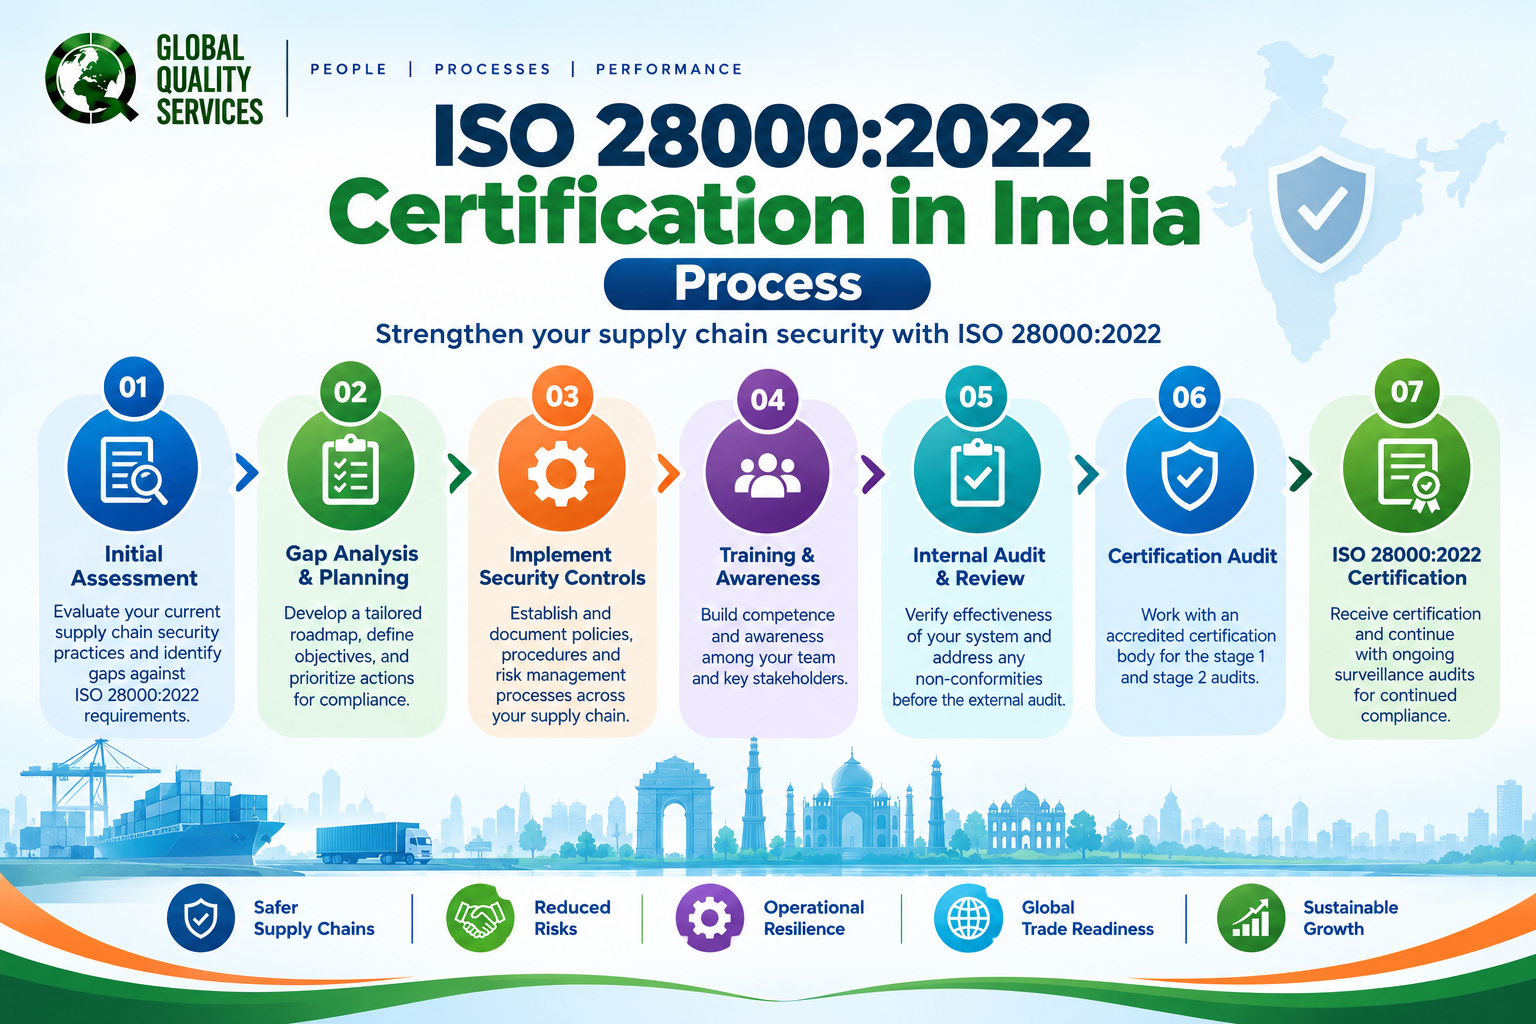
Step 1: Understand ISO 28000:2022 Requirements
The organization first understands the requirements of ISO 28000:2022 and determines how they apply to its operations.
Step 2: Conduct a Gap Assessment
The organization reviews existing security practices, processes, documentation, and controls against the standard’s requirements.
Step 3: Identify Security Risks
Identify and evaluate relevant security risks across operations and supply-chain activities.
Step 4: Develop the Security Management System
The organization establishes required processes, controls, responsibilities, documentation, and monitoring mechanisms.
Step 5: Implement the System
The organization implements the defined security processes across applicable functions and locations.
Step 6: Conduct an Internal Audit
The organization conducts an internal audit to determine whether the system is properly implemented and to identify areas requiring corrective action.
Step 7: Conduct Management Review
Management reviews the security management system’s performance and effectiveness and determines improvement requirements.
Step 8: Complete the Certification Assessment
The organization undergoes the certification assessment conducted by the applicable certification body.
Which Organizations Should Consider ISO 28000:2022 Certification in India?
ISO 28000:2022 is not limited to logistics companies. Organizations across sectors can consider the standard when security risks affect their operations or supply-chain activities.
Logistics and Supply Chain Companies
Logistics providers manage the movement, storage, handling, and distribution of goods across multiple locations. ISO 28000:2022 can help establish a structured approach to managing security risks throughout these activities.
Warehousing and Distribution Companies
Warehouses and distribution centers handle valuable goods and materials that may be exposed to theft, unauthorized access, damage, or other security risks.
Transportation Companies
Road, rail, air, and multimodal transportation providers can use a security management system to address risks associated with moving goods and related operations.
Ports and Maritime Organizations
Ports and maritime logistics organizations operate within complex environments involving cargo, vessels, personnel, transportation networks, and multiple stakeholders.
Manufacturing Companies
Manufacturers depend on reliable suppliers, transportation networks, warehouses, and distribution channels. ISO 28000:2022 can help address security risks that could disrupt these interconnected activities.
Import and Export Companies
Organizations involved in international trade may have supply chains extending across multiple countries, suppliers, logistics providers, warehouses, and customers.
E-Commerce and Fulfillment Companies
E-commerce businesses depend on secure inventory management, warehousing, order fulfillment, transportation, and delivery networks.
Retail and Distribution Organizations
Large retailers and distributors can establish consistent security practices across relevant facilities and supply-chain operations.
Pharmaceutical and Healthcare Supply Chains
Pharmaceutical products, medical equipment, and healthcare supplies often require reliable and controlled supply chains. A security management system can help protect products and related logistics activities.
High-Value Goods and Specialized Logistics
Organizations handling electronics, machinery, sensitive equipment, or other high-value products may benefit from a structured approach to security risk management.
What Does ISO 28000:2022 Cover?
ISO 28000:2022 focuses on establishing a security management system that is appropriate to an organization’s activities and security risks.
Security Risk Identification
Organizations need to understand relevant security risks associated with their operations and supply-chain activities.
Security Objectives and Controls
The organization establishes appropriate security objectives and measures based on identified risks and operational requirements.
Operational Security
Organizations can incorporate security considerations into relevant operational processes and activities.
Monitoring and Evaluation
Organizations need processes to monitor the effectiveness of their security management system and evaluate its performance.
Corrective Action
When security-related nonconformities or system weaknesses are identified, organizations can establish and follow up on appropriate corrective action.
Continual Improvement
The security management system should be maintained and improved as organizational activities, risks, and operating conditions change.
Benefits of ISO 28000:2022 Certification in India
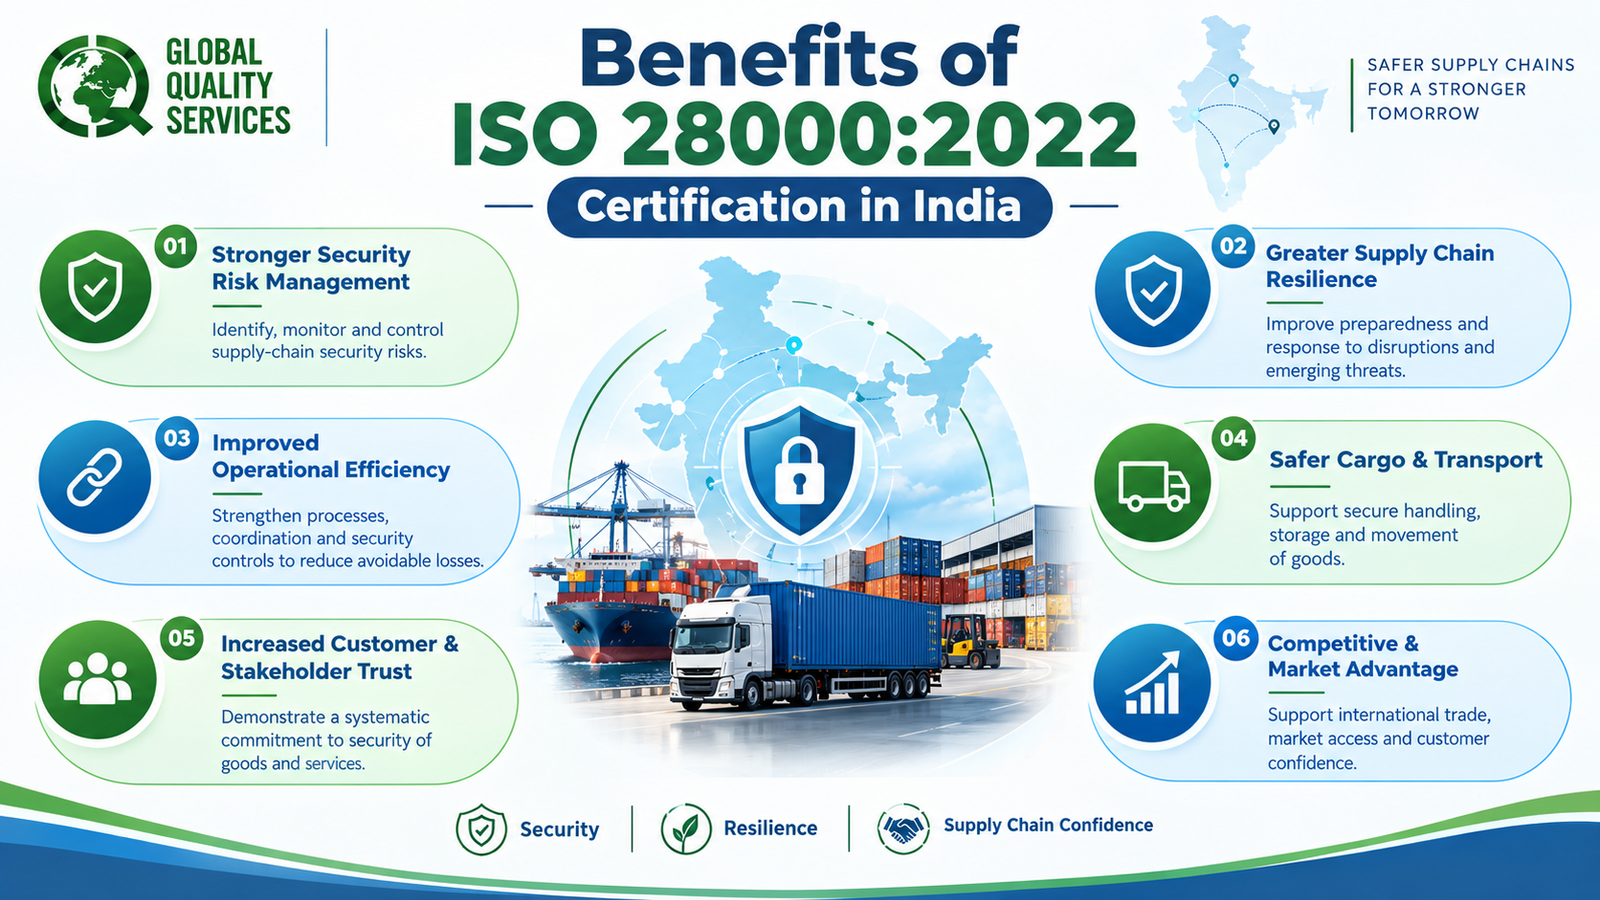
Stronger Supply Chain Security
ISO 28000:2022 provides a structured framework for addressing security risks that may affect supply-chain operations.
Better Security Risk Identification
Organizations can systematically identify security threats and evaluate their potential impact on business activities.
Improved Operational Control
Clearly defined processes and responsibilities can improve consistency in managing security-related activities.
Protection of Assets and Resources
A structured security management system can better protect physical assets, goods, facilities, people, and other resources.
Reduced Supply Chain Disruptions
Identifying security risks in advance can help organizations establish measures to reduce the likelihood and impact of disruptions.
Improved Stakeholder Confidence
Customers, suppliers, business partners, and other stakeholders can gain greater confidence in an organization’s approach to security management.
Support for International Business
Organizations working with international customers and supply-chain partners can demonstrate their commitment to an internationally recognized security management framework.
Continual Improvement
Regular monitoring, auditing, review, and corrective action help organizations continually improve their security management practices.
How Can Global Quality Services Help with ISO 28000:2022 Certification in India?
Global Quality Services can help organizations prepare for ISO 28000:2022 certification by reviewing existing security and supply-chain processes, conducting gap assessments, identifying areas requiring improvement, supporting the development of relevant documentation, and preparing the organization for the certification assessment.
GQS can also help organizations understand how to incorporate ISO 28000:2022 requirements into their existing management systems and operational processes.
Global Quality Services provides certification consultancy and management-system support for organizations seeking to strengthen their processes and prepare for third-party certification.
With experience across different industries, GQS can help organizations take a practical approach to ISO 28000:2022 requirements based on their operational activities and security risks. The focus is on developing a management system relevant to the organization, rather than creating unnecessary documentation or controls.
Frequently Asked Questions
What Is ISO 28000:2022 Certification?
ISO 28000:2022 certification demonstrates that an organization’s security management system has been assessed against the requirements of ISO 28000:2022.
Is ISO 28000:2022 Only for Logistics Companies?
No. ISO 28000:2022 is not industry-specific and applies to different types and sizes of organizations, including manufacturers, logistics providers, transportation companies, government organizations, and other businesses.
Is ISO 28000:2022 the Same as Supply Chain Management Certification?
No. ISO 28000:2022 focuses specifically on a security management system. Its scope includes security aspects relevant to supply-chain activities, but it is not a general supply-chain management standard.
Can ISO 28000:2022 Be Integrated with ISO 9001?
Yes. Organizations may integrate relevant management-system processes where practical. However, ISO 28000:2022 has its own specific requirements related to security management.
What Is the Current Version of ISO 28000?
The current published standard is ISO 28000:2022. ISO also published Amendment 1:2024, which introduces climate-action changes.