Noida has developed into a major technology and business hub, with IT companies, SaaS providers, fintech firms, manufacturers, and global service businesses handling sensitive information every day. The Times of India reported that a semiconductor project worth Rs 3,250 crore has been allotted land in Noida’s Electronics Manufacturing Cluster, highlighting the city’s growing technology and industrial activity. As customer expectations around cybersecurity continue to rise, businesses need more than written security policies. They need evidence that their controls actually work.
A CyberVadis cybersecurity assessment gives businesses a structured way to evaluate their cybersecurity maturity across Identify, Protect, Detect, and React. For companies in Noida, it can support customer evaluations, supplier reviews, and business relationships that require clear cybersecurity evidence. Hiring an experienced CyberVadis consultant can simplify assessment preparation, identify documentation gaps, organise evidence, and help your team present its cybersecurity practices accurately.
What is a CyberVadis Cybersecurity Assessment?
A CyberVadis assessment evaluates how systematically an organisation manages cybersecurity. It looks beyond policies and checks whether security controls are implemented and monitored in practice.
The assessment covers four important functions:
1. Identify
This area looks at asset management, risk assessment, data classification, and cybersecurity governance. It helps determine whether your business understands what it needs to protect.
2. Protect
This function reviews controls such as access management, encryption, network security, endpoint protection, and security awareness.
3. Detect
This area examines monitoring, logging, anomaly detection, and vulnerability management. It focuses on how effectively your organisation can identify potential security incidents.
4. React
This function reviews incident response, business continuity, recovery, and communication procedures.
CyberVadis also considers three evidence layers: definition, implementation, and monitoring. This means having a policy alone may not be enough. You need evidence showing that your team follows and reviews those controls.
Why Do Businesses in Noida Need CyberVadis Assessment?
Businesses in Noida often work with enterprise customers, international clients, technology partners, and large supply chains. These relationships can bring cybersecurity questionnaires and third-party security reviews into the procurement process.
Instead of repeatedly answering different security questionnaires, businesses can use a structured assessment to demonstrate their cybersecurity maturity more clearly.
A CyberVadis assessment can help Noida businesses:
- Understand their current cybersecurity maturity
- Identify weaknesses in existing security controls
- Organise cybersecurity documentation and evidence
- Respond more confidently to customer security requirements
- Support vendor and supplier evaluations
- Improve internal cybersecurity practices
- Create a practical improvement roadmap
CyberVadis provides a scorecard that shows cybersecurity performance by function and topic. It also provides an improvement plan with prioritised actions for strengthening security practices.
What Does CyberVadis Assess?
CyberVadis customises its questionnaire according to factors such as your organisation’s sector, size, IT practices, and qualification responses. This means businesses do not simply receive the same checklist regardless of their operations.
Key areas can include:
- Security Governance: The assessment reviews security policies, responsibilities, procedures, and governance practices that guide your organisation.
- Risk Management: It examines how your organisation identifies, evaluates, treats, and monitors cybersecurity risks.
- Asset Management: The assessment looks at how effectively you maintain visibility over important systems, devices, applications, and information assets.
- Access Control: It reviews user permissions, authentication, privileged access, and access management practices.
- Vulnerability Management: The assessment examines how your team identifies, prioritises, tracks, and resolves security vulnerabilities.
- Security Monitoring: It looks at logging, monitoring, alerting, and other practices used to detect suspicious activity.
- Incident Response: The assessment reviews how your organisation prepares for, manages, documents, and communicates cybersecurity incidents.
- Business Continuity: It considers how effectively your organisation prepares for disruptions and maintains important business operations.
How Does the CyberVadis Assessment Process Work?
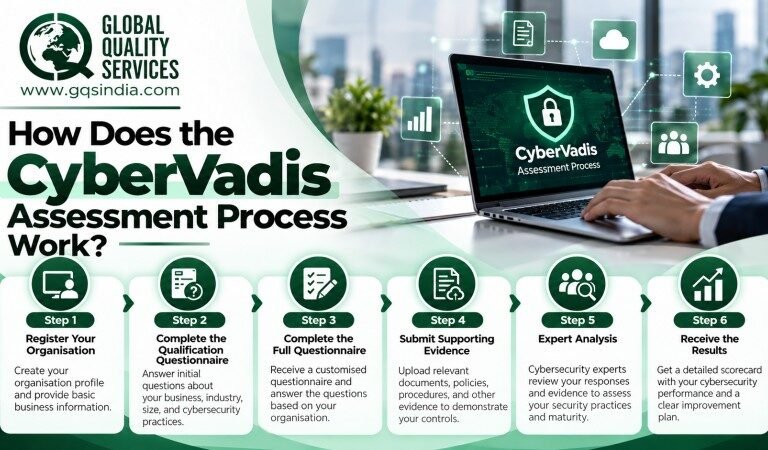
The CyberVadis assessment follows a structured process that takes businesses from registration through questionnaires, evidence review, expert analysis, and final results.
Step 1: Register Your Organisation
The process begins with registration. You create your company profile and submit basic business information and contact details. CyberVadis states that registration takes around five minutes.
Step 2: Complete the Qualification Questionnaire
You answer an initial set of questions about your organisation and its cybersecurity practices. These responses help CyberVadis customise the full questionnaire according to your business context.
Step 3: Complete the Full Questionnaire
You then complete the customised cybersecurity questionnaire and select the controls that apply to your organisation. CyberVadis also asks you to upload relevant supporting evidence.
Step 4: Submit Supporting Evidence
Evidence can include policies, procedures, screenshots, risk assessments, training records, audit reports, and other documents that support your answers. CyberVadis states that evidence is important because analysts need proof that declared controls exist.
Step 5: Expert Analysis
Cybersecurity analysts review your questionnaire responses and supporting evidence. They assess the credibility of your controls and assign scores across Identify, Protect, Detect, and React.
Step 6: Receive the Results
After the review, you receive a scorecard showing your cybersecurity performance, strengths, and risk areas. You also receive an improvement plan with actions that can help strengthen your security posture.
What Evidence Should Noida Businesses Prepare?
Good preparation can make the CyberVadis assessment much easier. Before starting the questionnaire, businesses should collect documents that demonstrate how their cybersecurity controls operate.
Common evidence may include:
- Information security policies
- Risk assessment reports
- Access control procedures
- Incident response plans
- Employee security training records
- Vulnerability assessment reports
- Business continuity plans
- Disaster recovery documents
- Audit reports
- Compliance certificates
- Security monitoring records
- Asset management documents
The important point is consistency. Your evidence should support the answers you submit and reflect how your organisation actually operates.
CyberVadis recommends gathering supporting evidence before beginning the assessment and involving the appropriate IT, information security, data protection, legal, and compliance teams.
How is Cybersecurity Maturity Evaluated?
CyberVadis focuses on how systematically and consistently a business manages cybersecurity.
The assessment considers three layers:
- Definition: Does the organisation have an appropriate policy or procedure?
- Implementation: Does the organisation actually follow the documented security practice?
- Monitoring: Does the organisation regularly review and maintain the control?
This approach gives businesses a more practical view of cybersecurity maturity. A policy sitting in a folder does not automatically demonstrate that employees follow it in everyday operations.
What are the Benefits of CyberVadis Assessment in Noida?
A CyberVadis assessment can support both cybersecurity improvement and business development.
- Better Visibility Into Cybersecurity: The assessment helps management understand where the organisation performs well and where security practices need attention.
- Identify Security Gaps: Evidence-based review can reveal weaknesses in documentation, implementation, monitoring, and security processes.
- Stronger Customer Confidence: A CyberVadis scorecard gives businesses a structured way to demonstrate cybersecurity practices to customers and partners.
- Better Security Documentation: Assessment preparation encourages teams to organise policies, procedures, reports, and other cybersecurity records.
- Easier Customer Assessments: Businesses that regularly receive cybersecurity questionnaires can use a standardised assessment to communicate their security posture more efficiently.
- Clear Improvement Priorities: The CyberVadis improvement plan gives businesses practical actions they can use to strengthen their cybersecurity maturity.
Who Can Benefit From CyberVadis Assessment in Noida?
CyberVadis can be useful for organisations that handle sensitive information or work with customers who expect evidence of cybersecurity controls.
- IT and Software Companies: Software companies can use the assessment to demonstrate their cybersecurity practices during customer onboarding and vendor evaluations.
- SaaS Companies: SaaS providers can use evidence-based assessment results when enterprise customers request information about security controls.
- Fintech Businesses: Fintech companies manage sensitive financial information and often need to demonstrate strong security practices to customers and business partners.
- Manufacturing Companies: Manufacturers increasingly depend on connected systems, digital applications, and technology suppliers. A cybersecurity assessment can help them understand and communicate their security maturity.
- Healthcare Technology Companies: Healthcare technology businesses handle sensitive information and can use structured assessments to identify weaknesses in their security practices.
- Global Capability Centres: GCCs and organisations supporting international operations may need to demonstrate their cybersecurity controls to global stakeholders.
- Technology Service Providers: IT service providers that manage customer systems or sensitive business information can use CyberVadis to present their security posture more clearly.
How Can Noida Businesses Prepare for CyberVadis?
Start preparing before you open the full questionnaire. Good preparation can save time and reduce confusion during the assessment.
Begin by identifying the people responsible for IT, information security, data protection, legal, and compliance activities. Then review your existing documentation and compare it with your actual practices.
You should also:
- Collect relevant security policies
- Review your risk assessment records
- Organise access control evidence
- Check vulnerability management records
- Prepare incident response documentation
- Collect employee security training records
- Review business continuity and recovery plans
- Map evidence to relevant controls
- Check whether your documents are current
- Identify missing evidence before submission
- Avoid submitting documents that do not support the answers provided
CyberVadis also allows organisations to involve colleagues in completing the questionnaire, which can help distribute responsibility across the relevant teams.
Why Choose Global Quality Services for CyberVadis Assessment Support in Noida?
Global Quality Services helps Noida businesses prepare for CyberVadis assessment with practical and structured support.
Our team can review your existing cybersecurity practices, identify documentation gaps, organise supporting evidence, and help your internal teams understand assessment requirements.
We support businesses across Noida and nearby business locations, including Sector 62, Sector 63, Sector 125, Sector 132, Noida-Greater Noida Expressway, and other technology and commercial areas.
The goal is simple: help your team present its cybersecurity practices accurately while identifying areas that need improvement.
Frequently Asked Questions
- What is a CyberVadis cybersecurity assessment in Noida?
A CyberVadis assessment evaluates an organisation’s cybersecurity maturity across Identify, Protect, Detect, and React using questionnaires, supporting evidence, expert analysis, and detailed scorecards.
- Which Noida businesses can benefit from CyberVadis?
IT companies, SaaS providers, fintech businesses, manufacturers, healthcare technology firms, GCCs, and service providers can use CyberVadis to demonstrate cybersecurity maturity.
- What evidence is required for CyberVadis assessment?
Businesses may submit security policies, risk assessments, access procedures, incident plans, training records, vulnerability reports, audit documents, compliance certificates, and monitoring evidence.
- How long does the CyberVadis assessment take?
Registration takes around five minutes, while the full questionnaire typically requires two to three days when documentation is ready. Expert analysis generally takes four to six weeks.
- Can a consultant help with CyberVadis assessment preparation?
Yes. A consultant can review cybersecurity practices, identify evidence gaps, organise documentation, guide internal teams, and help prepare accurate responses before assessment submission.