As digital economies expand, firms in India are managing large amounts of personal data on customer portals, apps, cloud systems, HR systems, financial services, and transaction processing. By March 2026, India had 1,092.79 million internet subscribers, of which 1,065.88 million were broadband internet users, reported the Telecom Regulatory Authority of India (TRAI).
Privacy management becomes increasingly critical when organizations collect, process, store, or control Personally Identifiable Information (PII). ISO/IEC 27701:2025 sets requirements and guidelines for developing, implementing, operating, monitoring, evaluating, maintaining, and continuously improving privacy management. The 2025 version is a standalone management system standard applicable to both controllers and processors of PII.
ISO/IEC 27701:2025 can provide useful guidance to Indian companies seeking structure around privacy management responsibilities, documentation of data processing activities, management of privacy-related risks, and overall accountability to stakeholders. In addition, ISO/IEC 27701:2025 may assist in meeting relevant obligations within the scope of the Digital Personal Data Protection Act and Rules. However, certification does not automatically guarantee compliance with all relevant privacy regulations.
What is ISO/IEC 27701:2025 Certification
ISO/IEC 27701:2025 is an international standard for developing and implementing a Privacy Information Management System (PIMS). A PIMS provides organizations with an organizational framework for managing personal data throughout its lifecycle.
It allows organizations to define their privacy obligations, assess risks, implement controls, document their processes, and evaluate their effectiveness in meeting those privacy objectives. This standard applies to organizations performing one of two functions related to the handling of personal information:
- PII controllers determine how and why personal data will be processed.
- PII processors process personal data on behalf of another organization.
What Changed in ISO/IEC 27701:2025
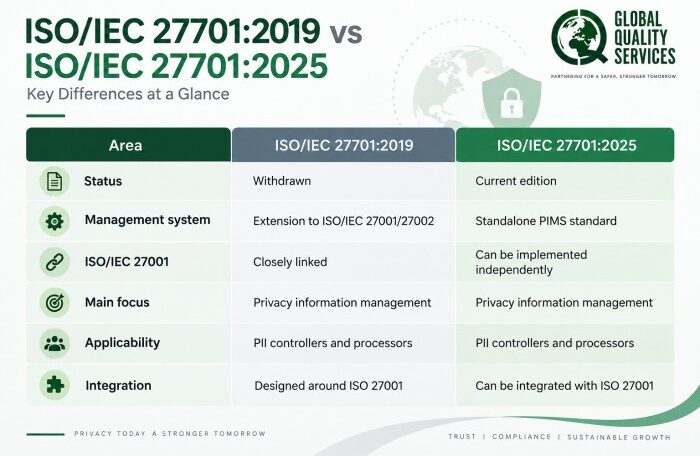
The 2025 version is the second revision of ISO/IEC 27701, succeeding ISO/IEC 27701:2019, which was withdrawn. The key difference with this update is that the 2025 version can stand alone as its own management system standard rather than merely being an add-on to ISO/IEC 27001 and 27002.
ISO/IEC 27701:2019 vs ISO/IEC 27701:2025:
Why is ISO/IEC 27701:2025 Important for Indian Businesses
Personal data is integral to modern business processes. Your client lists, personnel files, CRMs, SaaS applications, web properties, financial systems, and outsourcing providers may each deal with personal data. ISO/IEC 27701:2025 provides organizations with a structured approach to managing their obligations in this area. Here is how it could benefit your business:
- Establish formal privacy governance
- Identify and manage privacy risks
- Define responsibilities for PII processing
- Maintain documented privacy processes
- Demonstrate accountability to customers and business partners
- Strengthen privacy due diligence for international clients
- Integrate privacy management with existing security processes
Businesses seeking ISO/IEC 27701:2025 certification in Bengaluru may need to consider privacy processes across IT services, SaaS operations, BPOs and global delivery centres.
ISO/IEC 27701:2025 and India’s DPDP Framework
India has established its regulatory regime on digital personal data protection through its Digital Personal Data Protection Act, 2023, and the Digital Personal Data Protection Rules, 2025. On November 14, 2025, the Government of India promulgated the DPDP Rules, declaring that the DPDP Rules would operationalize the provisions of the DPDP Act.
The ISO/IEC 27701:2025 standard and the DPDP framework address different needs. The DPDP Act and rules set out requirements under law, whereas the ISO/IEC 27701:2025 standard offers a management system approach for organizing and documenting privacy management. A PIMS can help an organization structure areas such as:
- Personal data processing governance
- Privacy responsibilities
- Data handling procedures
- Risk assessment
- Privacy-related documentation
- Incident management
- Monitoring and continual improvement
The ISO/IEC 27701:2025 certification process doesn’t imply automatic compliance with the DPDP Act and Rules. Organizations will need to evaluate themselves against applicable laws based on the nature of their data processing activities.
ISO/IEC 27701:2025 and GDPR
When an organization processes personal data relating to individuals within the EU, they may have GDPR compliance considerations as well. ISO/IEC 27701:2025 establishes a framework for managing privacy, which can help organizations in several ways related to privacy accountability and governance, such as:
- Managing PII processing activities
- Defining privacy responsibilities
- Managing privacy risks
- Handling applicable data subject requirements
- Managing third-party privacy responsibilities
- Maintaining evidence of privacy processes
- Reviewing and improving privacy controls
Companies pursuing ISO/IEC 27701:2025 certification in Hyderabad can use the framework to structure privacy processes across technology, outsourcing, and service delivery operations.
Who Needs ISO/IEC 27701:2025 Certification in India
ISO/IEC 27701:2025 could be useful for any company dealing with personal data processing. It directly addresses companies that work as PII controllers and processors. These are the sectors requiring ISO/IEC 27001:2025 certification:
- IT, SaaS and Cloud Companies
- Banks, NBFCs and FinTech Companies
- BPOs and KPOs
- Healthcare and Health-Tech Companies
- E-commerce and Retail
- Insurance and InsurTech
- HR and Recruitment Companies
- Government and Public Sector Organizations
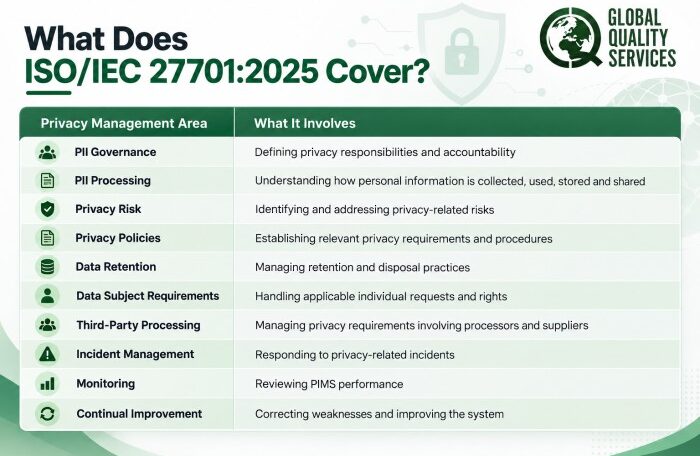
What Does ISO/IEC 27701:2025 Cover
A Privacy Impact Management System should take care of privacy management based on organizational function, processes performed, risk assessments, and scope definition. This is how it does so:
Key Benefits of ISO/IEC 27701:2025 Certification
Here are the key benefits of getting ISO/IEC 27701:2025 certification in India:
- Improved Privacy Governance: The PIMS clearly outlines roles, procedures, and controls for handling personal information.
- Increased Accountability: Companies can keep records demonstrating the delegation and management of privacy obligations.
- Compliance Assistance: This model can guide organizations in creating procedures related to privacy regulations.
- Greater Consumer Assurance: Certification serves as proof to consumers and partners alike of proper governance around privacy management.
- Supporting Global Operations: Privacy standards are helpful when completing customer surveys, supplier evaluations, and international due diligence processes around privacy matters.
- Better External Relationships Management: Organizations will have defined privacy guidelines for external third parties who handle PII on their behalf.
- Integration with Information Security: Firms that have ISO/IEC 27001 can combine their efforts regarding privacy management into their current information security management system framework.
Organizations working out of financial centers and technology hubs may leverage this standard to improve their privacy governance practices. This makes ISO/IEC 27701:2025 certification in Mumbai relevant for businesses handling customer, employee, financial, and technology-related personal information.
ISO/IEC 27701:2025 Certification Requirements
Before certification, an organization needs to establish and operate a PIMS within its defined scope. Key activities include:
- Define the PIMS scope based on how your business operates and processes personal information
- Determine who will hold the necessary privacy roles and responsibilities throughout the relevant organizational units
- Document what personal information is processed and the relevant privacy requirements involved
- Identify any privacy risks associated with those activities
- Create appropriate privacy policies and procedures related to the defined PIMS scope
- Apply the proper controls and processes within that scope
- Continuously monitor the performance of the PIMS and document everything accordingly
- Perform an internal audit before having your organization’s PIMS audited for certification
- Perform the required management review of your PIMS
- Have the certification body perform the certification audit
Firms working throughout the NCR area should also look at ISO/IEC 27701:2025 certification in Delhi, which applies to privacy management systems for IT, finance, health care, professional services, and other industries reliant on data.
ISO/IEC 27701:2025 Certification Process in India
Here is a clear process for achieving ISO/IEC 27701:2025 certification:
Step 1: Determine the PIMS Scope and Gap Assessment
Determine which organizational activities, sites, IT systems, and personal information processing will be covered within your PIMS scope. Perform a gap assessment between current practice and ISO/IEC 27701:2025 standards.
Step 2: Privacy Risk Assessment and PIMS Development
Document the flow of personal information processing, assess associated privacy risks, and create privacy policies, procedures, roles, and controls according to scope. There’s some overlap here between step 1 and step 2, since risk identification requires documentation.
Step 3: PIMS Implementation and Training
Implement the actual privacy controls you defined and train staff members about their privacy responsibilities. Document how the system is performing as intended.
Step 4: Internal Audit and Management Review
Carry out an internal audit to detect nonconformities and potential improvements. Management reviews the results of PIMS performance, internal audits, risk management, and corrective action prior to the external certification audit.
Step 5: Certification Audit Completion
The certification audit takes place independently of the organization, including the mandatory assessment of the PIMS. Any nonconformities detected throughout the audit process must be corrected prior to certification.
For companies pursuing ISO/IEC 27701:2025 certification in Chennai, this framework will assist them in preparing their privacy management system for external assessment.
Documents Required for ISO/IEC 27701:2025 Certification
The type of documentation required will depend on the certification scope of the organization and its processes. Some examples are:
- PIMS scope
- Privacy policies
- PII processing information
- Privacy risk assessment records
- Privacy objectives
- Roles and responsibilities
- Data retention procedures
- Data handling procedures
- Data subject request procedures
- Third-party and processor requirements
- Privacy incident procedures
- Training and awareness records
- Internal audit records
- Management review records
- Corrective action records
- Applicable legal and regulatory requirements
How Long Does ISO/IEC 27701:2025 Certification Take
There isn’t one fixed timeline that will apply to all companies. It varies based on different variables, including:
- Organization size
- Certification scope
- Number of locations
- PII processing activities
- Existing privacy controls
- Existing ISO management systems
- Implementation readiness
How Much Does ISO/IEC 27701:2025 Certification Cost in India
There is no fixed ISO/IEC 27701:2025 certification price for every organization. The cost may depend on various factors such as:
- Number of employees
- Number of locations
- Certification scope
- Volume and complexity of PII processing
- Number of business processes covered
- Existing ISO/IEC 27001 framework
- Existing privacy documentation
- Certification body audit fees
- Consulting and implementation requirements
How Global Quality Services Helps With ISO/IEC 27701:2025 Certification
Global Quality Services provides consulting and implementation support for organizations preparing for ISO/IEC 27701:2025 certification. We have years of experience working with various industries across India:
- 26+ Years of Experience: Extensive experience in ISO certification and compliance consulting across industries.
- Qualified Experts: A team of experienced consultants, lead auditors, and compliance professionals.
- Industry Experience: Proven exposure across IT, BFSI, healthcare, manufacturing, BPO, and other sectors.
- Practical Approach: Business-focused guidance tailored to your actual operations, not generic templates.
- Pan-India Presence: Supporting organizations across major business locations, including Mumbai, Pune, Delhi, Bengaluru, Chennai, and Hyderabad.
Get ISO/IEC 27701:2025 Certification From a Reputed Consultant
With 26 years of experience, Global Quality Services provides practical consulting support for organizations preparing for ISO/IEC 27701:2025 certification. As a reputed consultant, we assist with gap assessment, privacy risk assessment, PIMS documentation, implementation, training, internal audit preparation, and certification audit readiness. Get structured support based on your organization’s actual privacy processes, business scope, and PII processing activities.
Frequently Asked Questions
1. Certifying To ISO/IEC 27701:2025 Required In India?
Not at all. The certification scheme is voluntary. Organizations can get certified voluntarily, either to prove a systematic privacy management practice or to fulfill client or contractual obligations.
2. Who Certifies ISO/IEC 27701:2025 Certification?
An external certifying body audits the organization’s Privacy Information Management System (PIMS) and issues a certificate. Organizations need to evaluate the certification body’s qualifications and accreditation status before engaging them.
3. How Frequently Should An Organization Undergo Audits for ISO/IEC 27701:2025 Certification?
Organizations certified under the standard undergo surveillance audits throughout their certification period before undergoing recertification based on their certification criteria.
4. Is Employee Information Included Under ISO/IEC 27701:2025?
Yes, employee data may qualify as part of an organization’s processing of PII. It depends on the scope of their PIMS as well.
5. Is There An Option To Gain ISO/IEC 27701:2025 Certification As A Startup?
Certainly. This standard applies to organizations irrespective of their size and industry. Their PIMS must align with their business operations and processing scope.