Every business in Mumbai today collects and stores a wide range of personal information, from customer data to employee records and online transactions. According to IBM’s 2025 report, the average cost of a data breach in India has reached ₹22 crore (a 13% year-on-year increase).
ISO/IEC 27701:2025 Certification helps organizations build a strong privacy management system and comply with international data protection laws. Working with trusted consultants like Global Quality Services makes this process smooth, structured, and effective for lasting data security.
What is ISO/IEC 27701:2025 Certification
The ISO/IEC 27701:2025 certification in Mumbai ensures that your organization has a formal Privacy Information Management System (PIMS) to manage personally identifiable information (PII). The framework outlines mandatory requirements for any entity collecting, processing, storing, or controlling personal information.
It addresses how organizations assess privacy threats, manage personal information, allocate privacy obligations, and constantly enhance their privacy approach. The latest 2025 release is the current iteration and is applicable to organizations of different sizes and industries such as IT firms, banks, hospitals, call centers, e-commerce websites, and others.
Who Needs ISO/IEC 27701:2025 Certification
Any organization that handles personal or sensitive information can benefit from this certification. It’s especially valuable for:
- IT and software companies
- BPOs and call centers
- Banks and financial institutions
- Hospitals and healthcare organizations
- E-commerce and digital service providers
Why is ISO/IEC 27701:2025 Important for Organizations
Mumbai is India’s business and tech powerhouse, with companies processing vast amounts of digital data every single day. Data privacy breaches can not only lead to heavy financial losses but also damage credibility. Here is how this certification helps:
- Keeps your business compliant with both Indian and international privacy laws
- Builds customer confidence through strong data protection practices
- Reduces the risk of data theft and misuse
- Enhances global business opportunities
- Encourages transparency and accountability across departments
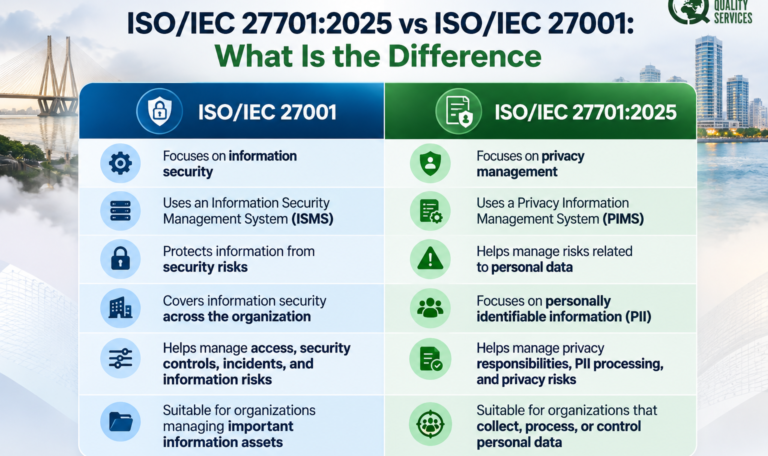
ISO/IEC 27701:2025 vs ISO/IEC 27001: What Is the Difference
These two standards enable firms to mitigate risk in relation to information, but their scopes differ. While ISO/IEC 27001 addresses information security specifically, ISO/IEC 27701:2025 addresses privacy and personal information management. For a clearer comparison between them, check out the chart below:
Step-by-Step Process to Get ISO/IEC 27701:2025 Certification in Mumbai
Here is the step-by-step process to get ISO/IEC 27701:2025 certification. All are in active voice, professional, and easy to read. Pick the one that fits your tone best.
Step 1: Gap Analysis
Consultants conduct a detailed review of your current data privacy framework to identify gaps in alignment with ISO/IEC 27701:2025 standards. This step provides a clear understanding of where improvements are needed and forms the base for a strategic compliance roadmap.
Step 2: Documentation Development
Privacy-related documents such as policies, procedures, consent forms, and records are created or refined to meet certification requirements. Proper documentation ensures consistency, defines accountability, and demonstrates your organization’s commitment to managing personal data responsibly and transparently.
Step 3: Implementation
Your teams are trained to integrate Privacy Information Management System (PIMS) controls into day-to-day operations. This stage ensures that data protection practices are effectively implemented, monitored, and maintained across all departments for long-term compliance and organizational integrity.
Step 4: Internal Audit
A comprehensive internal audit evaluates the performance of implemented privacy controls. Auditors identify non-conformities, recommend improvements, and verify whether corrective actions have been taken, ensuring your organization is fully prepared for the external certification audit process.
Step 5: Certification Audit
An accredited certification body performs an independent audit to verify compliance with ISO/IEC 27701:2025 requirements. After a successful evaluation, your organization is awarded certification, demonstrating its robust privacy management system and commitment to global data protection standards.
Key Benefits of ISO/IEC 27701:2025 Certification
Achieving ISO/IEC 27701:2025 offers long-term advantages that go beyond compliance:
- Strengthens data privacy and security
- Boosts trust among customers and partners
- Reduces risks of breaches and penalties
- Ensures alignment with global data protection laws
- Improves transparency and accountability
- Opens doors to global markets and collaborations
- Builds a culture of privacy awareness and improvement
How Much Does ISO/IEC 27701:2025 Certification Cost
The cost varies depending on company size and system complexity. Generally, the cost starts at USD 4,000 for small firms and can increase to USD 60,000 for large enterprises.
Pricing depends on factors like employee count, process maturity, and consultancy involvement. While it’s an investment, the certification adds lasting value by boosting trust and strengthening your privacy infrastructure.
Mumbai Areas We Cover for ISO/IEC 27701:2025 Certification
Global Quality Services supports businesses across major commercial and IT hubs in Mumbai, including:
- Andheri
- Bandra
- BKC
- Powai
- Lower Parel
- Goregaon
- Malad
- Vikhroli
- Thane
- Navi Mumbai
Documents Required for ISO/IEC 27701:2025 Certification
The exact documentation depends on your business and PII processing activities. Key documents generally include:
- PIMS Scope
- Privacy Policy
- PII Inventory
- Privacy Risk Assessment
- Data Protection Procedures
- Internal Audit Records
- Management Review Records
How Global Quality Services Supports ISO/IEC 27701:2025 Certification
Achieving ISO/IEC 27701:2025 Certification becomes simpler with expert guidance. Let’s see how Global Quality Services ensures a seamless and successful implementation process:
- Privacy Consultants with ISO Experience: Gain advice from reputed consultants who know everything there is to know about privacy management systems and certification standards.
- Gap Assessment: Our experts determine where the weaknesses lie within your current privacy practices and assist you in addressing them.
- Documentation Assistance: You get support in creating the necessary documentation needed for compliance with ISO/IEC 27701:2025, including policies, procedures, records, and more.
- Implementation Assistance: We provide assistance through every phase of implementing PIMS, conducting internal audits, and holding management reviews.
- Audit Readiness Assistance: Prepare for your audit by understanding audit requirements, compiling necessary evidence, and closing any gaps before the actual audit occurs.
- Certification Support: Your consultants remain engaged throughout the entire certification process to ensure success along the way.
At 26 years strong, Global Quality Services goes above and beyond as a consultant. Get a dependable partner to guide your company toward better data privacy policies and compliance with the new ISO/IEC 27701:2025 standard.
Partner with Global Quality Services – Your ISO Compliance Experts in Mumbai
ISO/IEC 27701:2025 certification is not just about meeting regulations; it’s about protecting your brand, building trust, and preparing your business for the future. With Global Quality Services, Mumbai organizations can achieve certification efficiently with expert guidance and hands-on support. Contact our consultants today and start your certification journey with confidence.
Frequently Asked Question
1. How does ISO/IEC 27701:2025 help my business in Mumbai?
It enhances your data privacy framework, ensures compliance with global regulations, prevents data breaches, and fosters customer trust.
2. Do I need ISO 27001 before applying for ISO/IEC 27701 Certification?
Yes. ISO/IEC 27701 is an extension of ISO 27001; therefore, you must first implement or be certified under ISO 27001.
3. How long does the certification process take?
Usually between three and six months, depending on your organization’s size, current privacy maturity, and implementation pace.
4. What challenges do companies face during implementation?
Most organizations struggle with documentation and awareness. Hiring experienced consultants helps simplify and accelerate the process.
5. Why choose Global Quality Services for ISO/IEC 27701 Certification in Mumbai?
Global Quality Services provides expert guidance, customized solutions, and full support from planning to certification, ensuring you achieve compliance efficiently while strengthening data protection practices.