Bangalore’s growing technology ecosystem has made data security a key priority for SaaS companies, fintech firms, IT providers, and startups. According to The Times of India, Bengaluru-based tech startups raised $4.4 billion during the first nine months of 2026, highlighting the city’s strong technology presence.
As businesses handle sensitive customer and business data, clients increasingly expect clear proof of effective security controls. SOC 2 attestation helps demonstrate this commitment. However, preparing for the assessment can be complex, making an experienced SOC 2 consultant valuable for identifying gaps, improving controls, and preparing your business for the audit.
What is SOC 2 Attestation
SOC 2 attestation is an independent examination of an organisation’s controls against the AICPA Trust Services Criteria. A qualified CPA firm evaluates whether the company’s controls are properly designed and, depending on the engagement, operating effectively over a defined period.
SOC 2 commonly covers five Trust Services Criteria:
- Security: Protects systems and information against unauthorised access.
- Availability: Keeps systems available according to agreed business requirements.
- Processing Integrity: Helps ensure systems process information accurately and completely.
- Confidentiality: Protects information classified as confidential.
- Privacy: Addresses how organisations collect, use, retain, and dispose of personal information.
A company does not necessarily need to cover all five criteria. The scope depends on its services, customer expectations, risks, and contractual requirements.
Why Do Bangalore Businesses Need SOC 2 Attestation
Bangalore’s technology ecosystem serves customers across India and international markets. Many enterprise customers now evaluate a vendor’s security controls before signing contracts or sharing sensitive data.
For a growing SaaS or technology company, this can create a practical challenge. Your sales team may have a strong product, but prospects can still ask:
“How do you protect our data?”
SOC 2 gives your business a structured way to answer that question with independent evidence.
It can help Bangalore organisations:
- Build trust with enterprise customers
- Respond to security questionnaires more confidently
- Support vendor and third-party risk assessments
- Strengthen internal security controls
- Improve customer confidence during procurement
- Support expansion into international markets
- Identify control gaps before they become larger problems
SOC 2 Type 1 vs SOC 2 Type 2
Choosing the right SOC 2 engagement matters because Type 1 and Type 2 serve different purposes.
SOC 2 Type 1 Attestation
A Type 1 report evaluates whether your controls are suitably designed and implemented at a specific point in time.
It can work well for organisations building their compliance programme and needing an initial independent assessment.
SOC 2 Type 2 Attestation
A Type 2 report goes further. It evaluates both the design of controls and their operating effectiveness over a specified period.
Customers often prefer Type 2 because it demonstrates that controls did not simply exist on paper. The organisation operated those controls consistently during the examination period.
For Bangalore SaaS and technology companies targeting larger enterprise contracts, SOC 2 Type 2 is often the more commercially valuable option.
SOC 2 Attestation Process in Bangalore
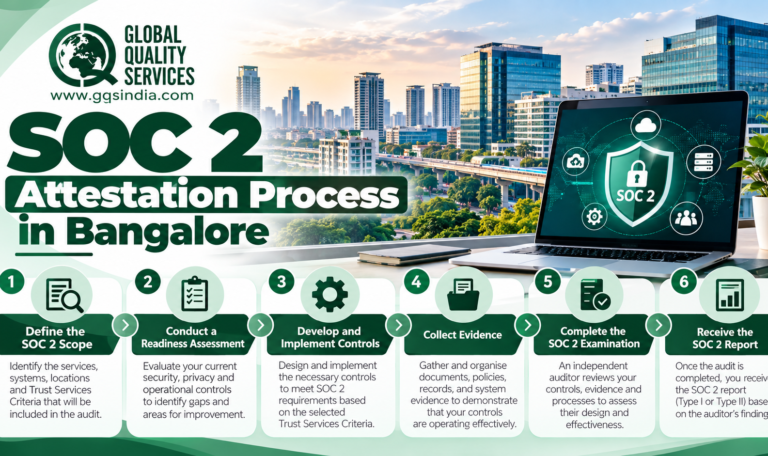
The process does not need to become complicated if you approach it systematically. A typical engagement involves the following stages.
1. Define the SOC 2 Scope
Begin by identifying the services, systems, applications, locations, processes, and teams included in your SOC 2 examination. A clear scope keeps the assessment focused, practical, and manageable.
2. Conduct a Readiness Assessment
Review existing security and operational controls against the selected Trust Services Criteria. This assessment helps identify weaknesses, missing controls, and improvements needed before the formal examination begins successfully.
3. Develop and Implement Controls
Address identified gaps by strengthening policies, access controls, risk management, incident response, change management, monitoring, vendor management, and other processes relevant to your selected SOC 2 criteria and business operations.
4. Collect Evidence
Gather reliable evidence showing employees consistently follow established controls. Records may include access reviews, security logs, training records, incident reports, approvals, monitoring reports, and supporting documentation for examination purposes.
5. Complete the SOC 2 Examination
An independent CPA firm performs the formal SOC 2 examination by reviewing your controls, processes, and supporting evidence against the agreed scope and selected Trust Services Criteria thoroughly.
6. Receive the SOC 2 Report
After completing the examination, your organisation receives its SOC 2 report. You can share the appropriate report with customers and prospects under suitable confidentiality arrangements when required.
How Long Does SOC 2 Attestation Take in Bangalore?
The timeline depends on your existing controls, organisation size, scope, and whether you pursue Type 1 or Type 2.
A readiness assessment and remediation phase may take several weeks or months. Type 1 generally has a shorter examination window because it assesses controls at a specific point in time.
Type 2 requires an observation period, so organisations need more preparation and planning.
Companies should therefore start early, particularly when a major customer has already included SOC 2 in its procurement requirements.
Which Bangalore Industries Should Consider SOC 2?
SOC 2 can benefit any organisation that stores, processes, or manages customer information through technology systems. It becomes particularly relevant for businesses selling technology-enabled services to other businesses.
SaaS Companies
SaaS providers frequently process customer data through cloud-based applications. SOC 2 can help demonstrate that the company has appropriate controls around security and access.
Fintech Companies
Fintech businesses handle sensitive financial information and often face detailed security reviews from customers, partners, and financial institutions.
IT and Software Companies
IT service providers, software development companies, and technology vendors can use SOC 2 to strengthen trust during enterprise procurement.
Healthcare Technology
Healthcare technology providers often handle sensitive information. A well-defined SOC 2 programme can demonstrate disciplined controls around security, confidentiality, and privacy.
Cloud Service Providers
Cloud-based businesses need strong controls around infrastructure, access, monitoring, availability, and incident management. SOC 2 can help demonstrate these controls to customers.
BPO and Business Process Companies
BPO companies frequently access or process customer information on behalf of clients. SOC 2 can support their security commitments during vendor evaluations.
AI and Data Companies
AI platforms and data-driven businesses increasingly face questions about how they protect customer information, control access, and manage data throughout its lifecycle.
SOC 2 Attestation in Bangalore for Growing Businesses
You do not need to wait until an enterprise customer demands SOC 2. If your business plans to move into larger B2B contracts, international markets, or regulated industries, starting early can save considerable time later.
A strong SOC 2 programme also brings value beyond the final report. It encourages teams to document responsibilities, review access regularly, monitor systems, manage vendors properly, and respond to security incidents consistently.
For Bangalore businesses competing in a crowded technology market, that operational discipline can become a genuine business advantage.
Why Choose Global Quality Services for SOC 2 Attestation in Bangalore
Preparing for SOC 2 becomes easier when you know exactly where your organisation stands and what needs improvement. A qualified consultant can review your current controls, identify gaps, guide remediation, and help your team prepare the necessary evidence before the independent examination.
If your Bangalore-based SaaS, IT, fintech, healthcare, or technology company is preparing for enterprise contracts, SOC 2 attestation can strengthen customer confidence while improving your internal security practices. Contact Global Quality Services to build your SOC 2 programme around your actual business operations rather than creating unnecessary controls.
FAQ’s
1. What is SOC 2 attestation in Bangalore?
SOC 2 attestation is an independent examination of an organisation’s controls for security, availability, confidentiality, processing integrity, or privacy. Bangalore businesses use it to demonstrate reliable data protection practices.
2. How long does SOC 2 attestation take in Bangalore?
The timeline depends on your scope, existing controls, and selected report type. Type 1 usually takes less time, while Type 2 requires an observation period to assess ongoing control effectiveness.
3. Which Bangalore businesses need SOC 2 attestation?
SaaS companies, IT service providers, fintech firms, cloud providers, BPOs, healthcare technology companies, and data-driven businesses can benefit from SOC 2 when customers require stronger security assurance.
4. What is the difference between SOC 2 Type 1 and Type 2?
SOC 2 Type 1 assesses whether controls are suitably designed at a specific point. Type 2 also evaluates whether those controls operated effectively throughout a defined examination period.
5. Can a SOC 2 consultant help with the attestation process?
Yes. A consultant can conduct readiness assessments, identify control gaps, support implementation, prepare evidence, and coordinate audit activities. An independent CPA firm performs the actual SOC 2 examination.