Delhi hosts many enterprises such as IT organizations, SaaS companies, fintech startups, BPO services, cloud service providers, and businesses dealing with confidential customer data. Given that these businesses operate within large enterprises based both domestically and internationally, demonstrating that their customers’ information systems remain adequately protected will directly impact business growth.
In its annual statistics on cybersecurity incidents, CERT-In noted 29,44,248 cases in 2025 compared to 20,41,360 in 2024. Additionally, CERT-In observed that the maximum number of cyber attacks occurred in the National Capital Territory of Delhi among various industries.
SOC 2 allows service organizations to evaluate their control processes and, in the case of a Type 2 assessment, evaluate whether the controls operate effectively concerning the respective criteria. Despite the frequent use of SOC 2 certification by businesses seeking this assessment process, the actual output comes in the form of an official attestation report provided through a separate CPA firm. At Global Quality Services, we offer consultancy for your SOC 2 examination and ensure proper preparation through practical advice and expertise. Keep reading to learn more about SOC 2 and our services.
What is SOC 2 Certification
SOC 2 (System and Organization Controls 2) is a framework by the American Institute of Certified Public Accountants (AICPA) that helps to assess how organizations safeguard their customer data.
SOC 2 looks at controls using the five criteria of Trust Services: Security, Availability, Processing Integrity, Confidentiality, and Privacy. SOC 2 is utilized by SaaS companies, IT service companies, cloud companies, fintech companies, and other firms dealing with sensitive customer data.
There are two types of SOC 2. The Type 1 assessment tests if the controls are appropriately designed at a certain time. The Type 2 also examines if controls are working effectively during a period. It should be noted that SOC 2 certification is usually not used; the correct term is SOC 2 attestation.
Why Delhi Businesses Are Looking for SOC 2 Certification
Organizations in the Delhi tech and services space manage customer data, internal information systems, cloud operations, and outsourced processes on a regular basis. Security isn’t just an issue that’s relevant for their own internal IT teams; enterprise clients might ask them to prove that their processes are managed correctly.
SOC 2 could potentially meet that need by auditing against the appropriate AICPA Trust Services Criteria. Here are some situations where SOC 2 may be especially useful for organizations operating in Delhi NCR:
- US and international SaaS customers
- Enterprise technology buyers
- Financial and fintech clients
- Healthcare and HealthTech organizations
- Cloud and managed service customers
- BPO and KPO clients
- Businesses processing customer or confidential information
- Companies responding to detailed vendor security questionnaires
Who Needs SOC 2 Certification in Delhi
SOC 2 is especially pertinent for companies using technology to handle customer information storage, processing, or protection. In Delhi, some industries that can benefit from SOC 2 preparation include the following:
- SaaS and Software Companies
- IT and ITES Companies
- FinTech and Financial Technology Businesses
- BPO and KPO Companies
- Cloud and Managed Service Providers
- HealthTech and Data-Driven Businesses
The Five Trust Services Criteria
Your report will focus on one or more of the five Trust Services Criteria. Security is mandatory for every report, while the remaining four are included based on your specific business operations.
- Security: Protects system resources against unauthorized access and software vulnerabilities. Controls include firewalls and multi-factor authentication.
- Availability: Ensures your systems remain operational as agreed in customer service level agreements. Controls cover network monitoring and disaster recovery testing.
- Processing Integrity: Verifies that system processing is complete, valid, accurate, and authorized. This is essential for financial platforms and automated data processing engines.
- Confidentiality: Guarantees that information designated as confidential is protected from disclosure. Controls include data encryption and strict access role policies.
- Privacy: Addresses how personal information is collected and disposed of in alignment with your privacy notice and global regulations.
Our 5 Step SOC 2 Advisory Process
Global Quality Services follows a proven 5-step preparation framework to get your business fully audit-ready. As dedicated consultants, we handle the heavy lifting so you pass your final audit with confidence.
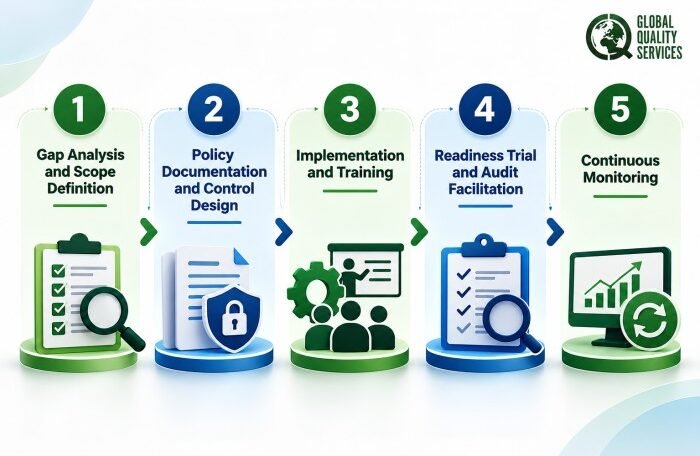
- Step 1: Gap Analysis and Scope Definition: We evaluate your current systems against SOC 2 criteria to identify vulnerabilities and define your exact audit scope.
- Step 2: Policy Documentation and Control Design: Our team drafts custom security policies and designs practical internal controls tailored to your daily operations.
- Step 3: Implementation and Training: We work alongside your team to execute new security protocols and train your staff on compliance best practices.
- Step 4: Readiness Trial and Audit Facilitation: We run a simulated audit to fix any remaining gaps, connect you with a licensed CPA firm, and manage the entire external audit process.
- Step 5: Continuous Monitoring: We provide ongoing support to keep your controls effective for future SOC 2 Type 2 evaluation periods and renewals.
Key Benefits of SOC 2 Certification in Delhi
SOC 2 Compliance in Delhi is not just an act of being compliant but a step to enhance your reputation, processes, and long-term success. Here are some advantages your business can reap:
- Builds High-Level Client Trust: Today’s clients expect their service providers to manage their information in the most secure way possible. Having SOC 2 Certification, you will prove that you use the highest data protection standards and build strong relations with clients, which is particularly important for IT, BPO, and SaaS companies in Delhi.
- Enhances Information Security Infrastructure: With SOC 2 Compliance in Delhi, you will implement top-level security standards. You will make sure that all of your systems, network, and processes meet global requirements of confidentiality, integrity, and availability.
- Satisfies Global Business Needs: Many international businesses ask their vendors for SOC 2 Certification. Thus, with this certification, organizations from Delhi can easily go international and satisfy global business needs.
- Limits Risks and Data Breaches: SOC 2 emphasizes recognizing weaknesses and increasing the effectiveness of internal controls. This way, the risk of data breaches, hacking, or any other negative occurrence is minimized to protect the reputation of your organization.
- Increases Operational Efficiency: Preparing for SOC 2 Certification involves streamlining processes and documenting procedures that make the workflow smoother, more transparent, and efficient.
- Creates Competitive Advantage: When competing for clients in the growing Delhi tech market, SOC 2 Certification will give your company an undeniable competitive advantage in terms of its reliability and professionalism.
- Complies With Other Standards: SOC 2 controls are aligned well with the majority of other data protection frameworks, including ISO 27001, GDPR, and others. Thus, certification allows you to work toward compliance with several standards at once.
- Facilitates Business Growth: Business sustainability in today’s world depends largely on trust and compliance. By staying SOC 2 Certified in Delhi, you make a clear statement that you believe in data ethics and best practices, thus fostering better relations with your partners and investors.
Common SOC 2 Challenges Faced by Businesses in Delhi
SOC 2 preparation can become difficult when organizations try to handle it without a clear understanding of the requirements. Common challenges include:
- Not knowing which systems and services should be included in scope
- Choosing the appropriate Trust Services Criteria
- Creating policies that do not match actual business practices
- Maintaining consistent evidence
- Managing employee access and offboarding
- Tracking vendor and third-party risks
- Preparing for Type 2’s observation period
- Coordinating multiple internal teams
- Understanding what customers actually expect from the SOC 2 report
- Preparing for auditor requests without disrupting daily operations
SOC 2 Consulting Support Across Delhi NCR
Global Quality Services provides SOC 2 consulting support for organizations operating across Delhi and the wider NCR business region. Our consulting support can be relevant to businesses located in:
- New Delhi
- Central Delhi
- South Delhi
- East Delhi
- West Delhi
- Gurugram
- Noida
- Greater Noida
- Ghaziabad
- Faridabad
How Compliance Experts Help You Achieve SOC 2 Certification
Global Quality Services brings more than 26 years of consulting experience across certification and compliance requirements and supports organizations across major business locations in India. For Delhi businesses, our focus is on making SOC 2 requirements practical, understandable, and relevant to the way your organization actually operates:
Experience Spanning Technology and Compliance Standards
We operate in the domain that includes SOC 2, ISO 27001, ISO 27017, ISO 27018, ISO/IEC 27701, PCI DSS, HITRUST, and various other frameworks related to cybersecurity. Such knowledge allows companies to think not only about one single audit but to create a more connected compliance landscape.
Practical Advice Instead of Cookie-Cutter Templates
Each business has its unique technology stack, people, applications, vendor relationships, and client needs. Our approach emphasizes understanding the current situation in the business and then recommends the appropriate documentation and control measures.
Growing and Mature Businesses Services
Be it a startup in Delhi that is getting ready for its first SOC 2 engagement or a mature IT business that needs help building its compliance program, the consulting methodology can be tailor-made to fit the requirements of the business.
Consulting Expertise across India
Global Quality Services provides consulting services to businesses located in important cities of India such as Delhi NCR, Bangalore, Mumbai, Hyderabad, Chennai, Pune, and Ahmedabad. Thus, we can provide the required consulting expertise to businesses based in Delhi.
Get Your SOC 2 Certification Preparation Started in Delhi
If your customer is asking for a SOC 2 report, now is the time to understand your scope, identify gaps, and prepare your controls properly. Global Quality Services brings 26+ years of consulting experience to help Delhi businesses build practical compliance systems and prepare confidently for their independent SOC 2 examination.
Speak with our SOC 2 consultant today to discuss your business scope, Type 1 or Type 2 requirements, expected timeline, and certification support. Call +91 9845313910 or +91 9845078743 to schedule your consultation.
Frequently Asked Questions
1. Is SOC 2 mandatory for firms in Delhi?
No. It is not mandatory for most firms by law. However, business clients, particularly foreign clients, might ask for a SOC 2 report prior to making a deal.
2. Which SOC 2 type does my business need?
It is up to you based on client needs and the level of maturity of your business. SOC 2 Type 1 measures controls as at a particular date, while SOC 2 Type 2 proves that controls worked throughout a certain period.
3. Can startups in Delhi get SOC 2?
Yes, they can. Startups can be ready for SOC 2 if they have clear systems, procedures, controls, and enough evidence for testing.
4. How long does a SOC 2 Type 2 audit take?
This is contingent upon the scope, preparedness, and period of observation of the organization. Type 2 audits usually take more time compared to Type 1 since they look at controls over a specified period of time and not just once.
5. What documentation do you need for SOC 2?
Documentation required by organizations includes security policies, procedures, risk assessment, access logs, system data, vendor data, training documentation, among others.