The technology industry in Chennai continues to expand rapidly. The data protection requirements increase along with the size of this market. In the financial year 2022-23, Tamil Nadu has achieved its highest software export figures yet, registering ₹2 lakh crore at a 16.4% CAGR. That’s according to Tamil Nadu Information Technology Department figures. Data security is an increasingly crucial component of attracting and keeping clients among SaaS vendors, IT services firms, fintech organizations, and global delivery centers based throughout OMR, Sholinganallur, Taramani, Perungudi, Guindy, and Siruseri.
Here is where SOC 2 comes into play. SOC 2 provides an objective framework for validating a company’s controls regarding security, availability, processing integrity, confidentiality, and privacy. Controls are assessed for design and operational effectiveness. Additionally, for Chennai organizations serving foreign clients, enterprises, or dealing with sensitive data, SOC 2 reporting could be a great resource to address security queries during initial discussions before signing off on a project. What is SOC 2? Who requires it? How should a business in Chennai approach getting their SOC 2 audit done? Let’s dive in.
What is SOC 2 Certification
SOC 2 certification refers to a set of controls designed by the American Institute of Certified Public Accountants (AICPA). It evaluates the controls of service providers concerning security, availability, processing integrity, confidentiality, and privacy.
It is crucial for any organization handling customer data, whether stored, processed, or managed. Some examples include a SaaS business based in Chennai with its cloud computing services. Another one could be a BPO processing customer data for foreign firms. Fintech companies that work with sensitive financial details and healthtech solutions managing private health information are further examples.
Why SOC 2 Certification Matters for Chennai Businesses
Given the number of IT parks, cloud services, and BPOs located in Chennai, data protection has ceased to be something you can do without if you want to compete successfully. SOC 2 Certification guarantees security, reliability, and client confidentiality in your process infrastructure, which makes it vital. The following are reasons why this certification will be crucial for your organization going forward:
- Your clients need assurance of compliance before delegating any sensitive processes to you.
- Partnerships across the globe necessitate showing strong capability for handling data.
- Data leaks can cost your organization in financial terms, as well as damaging its reputation.
- SOC 2 Certification will provide your business with an undeniable competitive advantage.
By pursuing SOC 2 Certification in Chennai, you are not only ensuring adherence to standards; you are demonstrating integrity to potential partners and clients.
Understanding SOC 2 Type I and Type II Certification
Both Type I and Type II certifications serve different purposes, and understanding them helps you plan your compliance journey effectively.
-
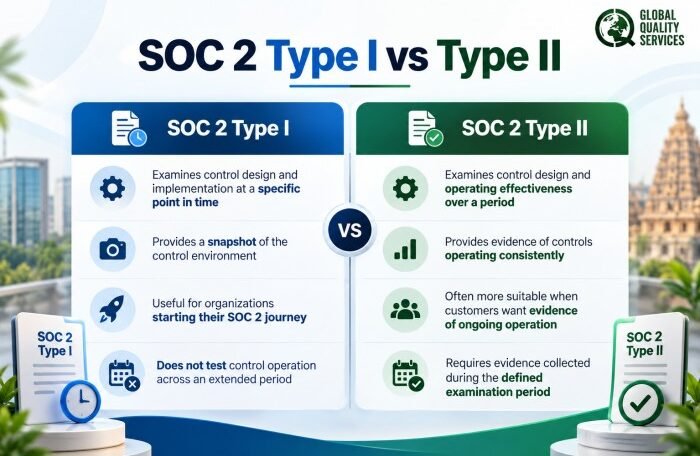
SOC 2 Type I Certification:
Focuses on your system’s design and documentation at a specific point in time. It verifies that proper controls exist to safeguard information.
Ideal for startups or companies beginning their compliance journey. -
SOC 2 Type II Certification:
Assesses how effectively those controls work over a defined period (usually 6–12 months). It provides deeper assurance that your organization consistently maintains compliance.
Best suited for established companies serving long-term enterprise clients.
Many Chennai organizations begin with Type I and progress to Type II as their operations scale and mature. GQS helps you plan this transition seamlessly.
SOC 2 Type I vs Type II
One of the first decisions a company needs to make is whether it should pursue a Type I or Type II report.
The SOC 2 Certification Process in Chennai
Getting SOC 2 certified sounds complicated, but GQS makes this process straightforward thanks to its systematic approach. It works as follows:
- Readiness Assessment & Gap Analysis: We first assess your systems’ status and determine any deficiencies compared to the SOC 2 criteria.
- Documentation & Control Development: Next, our consultants will develop strong cybersecurity policies, access management, and monitoring capabilities for you.
- Implementation Assistance: Then, we will help your employees implement appropriate controls across your organization.
- Internal Audit Simulation: This step involves conducting a simulated internal audit to make sure everything is prepared before the actual audit starts.
- External Audit Facilitation: Finally, we coordinate with reputable external auditors who confirm that your business meets the requirements and deserves either Type I or Type II SOC 2 certification.
- Continuous Improvement: Compliance is not a one-off task; therefore, we support you after obtaining SOC 2 certification.
This step-by-step approach ensures that SOC 2 Certification in Chennai is achieved efficiently without disrupting your daily operations.
Key Benefits of SOC 2 Certification in Chennai
There are a few important advantages associated with SOC 2 certification, which will benefit your business, clients, and reputation.
- Gains Client Trust: Shows that your IT infrastructure can manage data safely and responsibly.
- Lowers Risks: Helps avoid any accidental breaches or disruptions in operations.
- Improves Efficiency: Promotes consistency in record-keeping throughout your company.
- Increases Market Opportunities: Many international businesses operate exclusively with SOC 2-compliant service providers.
- Enhances Brand Reputation: Communicates your dedication to industry best practices and operational excellence.
- Future-Proofs Compliance: Helps align with future regulations like ISO 27001 and GDPR.
.Industries in Chennai That Benefit from SOC 2 Certification
Given Chennai’s thriving service economy, SOC 2 Certification is relevant across multiple sectors:
- Information Technology & Software Development
- Business Process Outsourcing (BPO) & Shared Services
- Cloud Service Providers and SaaS Platforms
- Fintech and Financial Institutions
- Healthcare Data Processing Firms
SOC 2 in Chennai: Key Business Areas
SOC 2 affects technology and business hubs throughout Chennai, including beyond any particular IT zone.
OMR and Sholinganallur
Technology companies, especially those operating in cloud computing, SaaS, software engineering, or BPOs, will likely face SOC 2 compliance demands coming from large enterprises as clients in these regions.
Taramani
The presence of numerous research-focused and technology companies in Taramani makes this region critical for firms handling digital assets and information-centric solutions.
Perungudi
Corporate campuses and technology parks in Perungudi host many kinds of technology and service firms whose operations hinge upon data security and customer relationships.
Guindy
Guindy contains technology companies, engineering firms, professional services, and corporate back-office operations. Enterprises targeting big businesses could find themselves having to meet rigorous vendor security standards.
Siruseri
SIPCOT IT Park specializes in large-scale technology operations and IT services. Any company operating within this region that targets international clients should strongly consider implementing security assurance measures.
Ambattur
Ambattur includes manufacturing facilities but also extends into technology and business service operations. Firms managing digital infrastructure and personal data should seriously consider establishing security controls.
Porur, Velachery, and Nungambakkam
These mature business districts also house tech companies, consulting firms, healthcare providers, and corporate offices that should showcase robust cybersecurity protocols to their clients.
Common SOC 2 Preparation Challenges for Chennai Companies
Organizations often already do all the right things when it comes to cybersecurity, but proving compliance becomes difficult because of internal inconsistencies. Typical issues that arise include:
- Policy Compliant But Execution Lagging: There is an access control policy, but user access reviews don’t always occur according to schedule.
- Dispersed Proof: Proof of security controls resides in multiple tools such as HR databases, helpdesk tickets, cloud environments, spreadsheets, email, etc.
- Insufficient User Access Reviews: Old or relocated employees retain unnecessary access.
- Vendor Reviews Fall Short: Third-party vendors might hold critical data without any form of formalized security assessment on file.
- Security Incident Handling Lacks Formal Process: Teams can address security threats efficiently while failing to document their responses properly.
Cost and Duration for SOC 2 Certification in Chennai
The cost and duration of SOC 2 Certification depend on factors such as organization size, scope of services, and audit readiness.
- Type I Certification: Typically takes 2–3 months to complete, with a focus on control design.
- Type II Certification: Requires 6–12 months, as it evaluates operational effectiveness over a period of time.
- Investment Factors: Costs depend on the complexity of the systems, the number of departments, and the depth of the audit.
At Global Quality Services, we offer transparent pricing and practical timelines, enabling you to achieve SOC 2 Certification in Chennai efficiently, without unnecessary delays.
How Global Quality Services Offers Support for SOC 2 Certification in Chennai
For over 26 years, Global Quality Services, a reputed consultant, has been a trusted name in certification consulting. Our team has helped hundreds of organizations across India achieve international compliance benchmarks like SOC 2, ISO 27001, and GDPR. Here is what sets us apart:
- Local Expertise with Global Perspective: Deep understanding of India’s IT and outsourcing industries combined with international compliance experience.
- Customized Approach: Each organization is unique, and our solutions are tailored to reflect that.
- Audit-Ready Documentation Support: We assist in preparing all necessary policies and reports to ensure a smooth audit process.
- Continuous Guidance: From initial readiness to post-certification compliance maintenance.
- Proven Success Stories: Trusted by leading IT, BPO, and fintech organizations across Chennai and beyond.
Get SOC 2-Ready with Global Quality Services in Chennai
Your customers do not simply want to hear that their information is protected. They want confidence that the right controls are in place and that your organization follows them consistently.
GQS helps Chennai-based businesses prepare for SOC 2 with practical support covering gap assessment, documentation, implementation, evidence preparation, and audit readiness.
Whether you operate a SaaS company in Sholinganallur, an IT services business in OMR, a technology operation in Taramani or Perungudi, or a growing service organization in Guindy, Siruseri or Ambattur, we can help you build a structured path toward SOC 2 readiness.
Start your SOC 2 preparation with us by contacting our team and building the security assurance your customers expect.
Frequently Asked Questions
1. What does SOC 2 Certification mean for my business?
SOC 2 Certification validates that your company has robust internal controls for data security, availability, and privacy, earning client trust and improving your overall compliance posture.
2. How is Type I different from Type II?
Type I assesses whether your controls are designed effectively at one point in time, while Type II evaluates their operational effectiveness over several months.
3. Does SOC 2 certification apply to startups?
Absolutely. Startups can become SOC 2 compliant ahead of time, especially if large enterprises demand proof of compliance prior to contracting. Early preparation will ensure good security practices are ingrained within the company culture.
4. Is GQS responsible for completing the SOC 2 audit?
GQS offers advisory services and readiness assistance. The actual SOC 2 examination process is conducted by the service auditor.
5. Is privacy addressed by SOC 2?
Yes, privacy is one of the five Trust Services Criteria. Whether or not privacy applies to a specific SOC 2 assessment, however, depends on both the organizational scope and which criteria were chosen for review.