Pune has evolved into one of the leading technology and business centers in India. Software firms, SaaS firms, fintechs, IT services firms, and global delivery centers operate out of Pune, catering to clients throughout India and abroad. The numbers speak volumes. According to figures made available through the Economic Survey of Maharashtra for FY 2025-26, Maharashtra exported software worth ₹1.74 lakh crore between March 2025 and January 2026. Pune accounted for most of these exports.
In such an ecosystem, it pays to be able to demonstrate the protection of your customer data, which impacts your enterprise sales, vendor assessments, and even long-term partnerships with clients. Enter SOC 2 Certification in Pune. Why should SOC 2 matter? SOC 2 assesses controls for security, availability, processing integrity, confidentiality, and privacy against the AICPA Trust Services Criteria.
Is your client requesting a SOC 2 report? Are your sales teams inundated with security questionnaires? Do you need to tap into bigger international markets? Getting prepared can streamline the entire process significantly. Go ahead and learn about SOC 2 reporting requirements, report types, the certification process, advantages, and how GQS can help navigate your SOC 2 certification process in Pune.
What is a SOC 2 Compliance Engagement
SOC 2 certification refers to a control framework created by the American Institute of CPAs (AICPA) to assess the controls put in place by organizations providing services regarding their information security and system operations. SOC 2 uses five Trust Services Criteria:
- Security
- Availability
- Processing Integrity
- Confidentiality
- Privacy
Security is one component of SOC 2 that cannot be avoided. Everything else will vary depending on the unique attributes of your business model, IT infrastructure, services provided, and customers’ requirements.
SOC 2 is not really a certification process such as ISO certification. It’s an attestation engagement in which your organization hires an independent CPA firm to assess its systems and produce a SOC 2 report. SOC 2 reports become associated with ‘certification’ because of the way Google ranks SOC 2 service providers.
Why SOC 2 Certification Matters for Pune-Based Companies
The technology ecosystem in Pune comprises SaaS vendors, IT services, engineering companies, fintech firms, cloud computing companies, startups, and companies dealing with international clients. In many cases, these organizations will collect data about their customers or run systems that their customers rely on. If you belong to one of these organizations, then SOC 2 should align well with your business objectives.
- Gain More Client Trust: The SOC 2 report provides your clients with an unbiased assessment of the security measures you have implemented to handle their data and run mission-critical services.
- Close Enterprise Deals: Big enterprises perform rigorous security assessments before engaging with vendors. An up-to-date SOC 2 report will cover several of the security-related questions that usually arise.
- Improve Your Security Posture: SOC 2 preparation will prompt you to assess your controls related to access management, threat detection, incident handling, change control, vendor management, staff behavior, and any other item within scope.
- Expand Globally: Organizations based in Pune who do business in foreign regions such as the United States or Europe will likely encounter SOC 2 mandates in their sales cycles.
- Bridge Compliance Gaps: An organized SOC 2 readiness assessment enables you to pinpoint gaps between your current controls, policies, documentation, and the requirements.
Who Needs SOC 2 Certification in Pune?
SOC 2 is particularly relevant to service organizations that store, process, transmit, or otherwise manage customer information through their systems. Businesses in Pune that may benefit include:
- SaaS Companies
- IT service providers
- Cloud service providers
- Fintech companies
- Data processing companies
- BPO and KPO companies
- Software product companies
- Managed service providers
Startups moving into enterprise sales - Global capability centre vendors
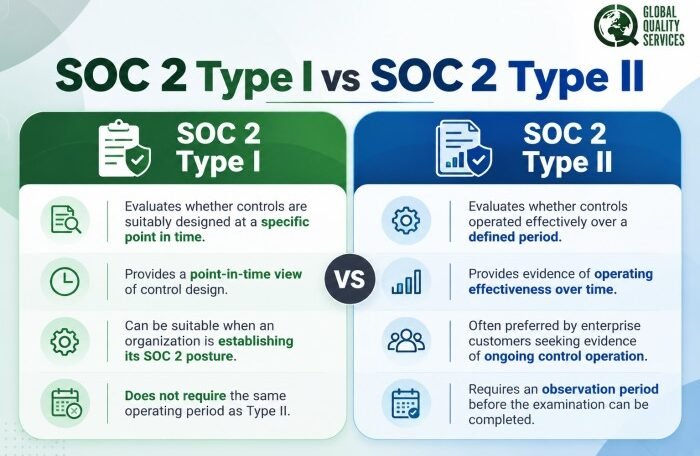
SOC 2 Type I vs SOC 2 Type II
Choosing the right report type is one of the first decisions an organization needs to make.
Process of Achieving SOC 2 Certification in Pune
The certification journey involves structured steps that ensure your company is fully prepared. Our team guides you through each stage of SOC 2 Certification in Pune:
Step 1: Set Your SOC 2 Scope
Determine which services, applications, systems, teams, facilities, and customer data will fall under your SOC 2 scope. Based on this assessment, determine which of the relevant Trust Services Criteria apply.
Step 2: Perform a SOC 2 Gap Assessment
Assess your current policies, control activities, processes, and documentation for any gaps against the appropriate SOC 2 requirements. You’ll get a complete list of items requiring attention prior to the independent examination process.
Step 3: Implement Controls and Gather Evidence
Close the gaps in your system, implementing controls related to topics such as access management, security monitoring, incident response procedures, risk management, vendor management, backup operations, and change management. Team members document these processes as proof of control implementation.
Step 4: Conduct Readiness Review and SOC 2 Examination
Perform a final readiness review to discover any outstanding concerns prior to starting the independent CPA examination. Control effectiveness needs to be demonstrated continuously during the entire examination period for a Type II audit. Meanwhile, a Type I audit will assess the design of your controls on one particular day.
Step 5: End With the SOC 2 Report
Once completed, the independent CPA firm delivers the relevant SOC 2 report. This document may now be distributed among your customers and partners as proof of controls.
How Long Does SOC 2 Certification Take in Pune?
There is no fixed timeline for every organization. The duration depends on factors such as:
- Type I or Type II report
- Scope of the examination
- Number of systems and applications
- Existing security controls
- Selected Trust Services Criteria
- Documentation readiness
- Evidence availability
- Number of business units involved
- Remediation requirements
- Type II observation period
What Documents and Evidence Are Needed for SOC 2?
The exact evidence requirements depend on the organization’s scope and selected criteria. Common evidence may include:
- Information security policies
- Risk assessment records
- User access reviews
- Employee onboarding and offboarding records
- Security awareness training records
- Password and MFA configurations
- Change management records
- Incident management records
- Vulnerability assessment reports
- Security monitoring records
- Backup records
- Disaster recovery test results
- Vendor assessment records
- Policy review records
- System and infrastructure information
Benefits of SOC 2 Certification for Pune Businesses
Preparing for SOC 2 certification can result in compliance and business benefits if done based on how your organization really works.
- Improved Customer Confidence: SOC 2 certification offers official proof of your controls that instills confidence in clients.
- Simplified Enterprise Procurement: A recent SOC 2 report provides easy answers to common security questions that come up in vendor evaluations.
- Improved Control Environment: The preparation phase may uncover vulnerabilities in access management, auditing, incident response, recordkeeping, etc.
- Enhanced Security Accountability: Roles and responsibilities ensure clear understanding of ownership when performing certain security functions.
- Benefits to International Businesses: Organizations dealing with international clients will find SOC 2 well-regarded among tech services providers.
- Minimized Risk of Unexpected Findings: Adequate preparation and documentation review can help prevent surprises during audits conducted independently.
Why Choose Global Quality Services for SOC 2 Certification in Pune
Global Quality Services (GQS) is one of India’s reputed consultants for compliance certifications. For organizations in Pune, our expertise in SOC 2 Certification in Pune offers unmatched advantages:
- Over 26 Years of Consulting Experience for Compliance: At GQS, we have accumulated over two decades of experience providing consulting services for management systems, information security, compliance, and certification.
- Business-Centric Consultation: Everything we do revolves around optimizing and improving upon the processes and systems that you already have in place. That means we’ll guide you on changes that need to happen without burdening you with superfluous documentation.
- Expertise with a Wide Range of Technology Firms: From IT and SaaS to cloud computing, fintech, BPOs, data processing, and other service industries, GQS works with businesses that value information security and customer assurance.
- Tailored SOC 2 Readiness Assistance: One-size-fits-all approaches don’t apply when preparing for SOC 2. Our team will determine how to tailor the process based on your services, systems, risks, and client needs.
- Full Cycle Assistance with the Process: Our experts will guide you through each stage of SOC 2 preparation, from assessing gaps and documenting, implementing controls, gathering evidence, readiness testing, and audit preparation.
- Deep Insight into Other Relevant Regulatory Requirements: We have experience working across various information security frameworks and compliance requirements. This gives us valuable insight when recommending ways to align SOC 2 controls with other relevant requirements.
- Pan-India Consulting Capability: GQS provides consulting support across major Indian business and technology centres, including Pune, Bengaluru, Mumbai, Delhi NCR, Hyderabad, Chennai, Ahmedabad, and other locations.
Get Expert SOC 2 Support in Pune and Move Your Enterprise Deals Forward
Prepare Your SOC 2 Readiness With GQS Before the Next Client Review. If a customer has asked for SOC 2, your sales team is facing security questionnaires, or you are preparing for enterprise and international contracts, connect with GQS for a tailored SOC 2 readiness discussion.
Call us or submit your enquiry today to discuss your SOC 2 scope, Type I or Type II requirements, readiness gaps, and audit preparation needs with an experienced compliance consultant.
Frequently Asked Questions
1. Is SOC 2 certification mandatory in Pune?
SOC 2 certification isn’t legally required for every company operating out of Pune. That said, some clients, enterprise customers, or business partners may ask for the SOC 2 compliance document during procurement.
2. Who Conducts the SOC 2 Audit for GQS Clients?
GQS doesn’t conduct any SOC 2 examinations internally or issue SOC 2 reports. Instead, we advise companies on SOC 2 readiness and prepare them for the exam with our consulting services.
3. What is the difference between SOC 2 Type I and Type II, and which is right for my Pune startup?
Your selection will depend on client needs, business priorities, the sophistication of your internal controls, and overall organizational readiness. If your customer demands SOC 2 Type II compliance, then you need to account for this during planning instead of settling for Type I.
4. How much does SOC 2 compliance cost in Pune?
SOC 2 compliance costs vary widely based on factors such as scope, systems, criteria, report options, existing controls, remediations needed, observation periods, and independent auditor fees. There is no fixed rate applicable across all organizations.
5. How does SOC 2 benefit enterprise clients?
A SOC 2 report gives third-party verification of control effectiveness within the scope of the examination. This makes it easy to comply with security audits requested by customers and vendors.