Organisations in Chennai handle large amounts of sensitive information every day. Hospitals manage patient records, healthcare technology companies process health data, laboratories store diagnostic information, and software providers support digital healthcare services. Protecting this information requires more than basic cybersecurity controls.
HITRUST CSF Certification in Chennai provides a structured way for organisations to assess their information security, privacy, risk management, and compliance controls against the requirements of the HITRUST framework.
Global Quality Services (GQS) supports organisations in Chennai with HITRUST CSF certification readiness, gap assessment, documentation support, risk assessment, control implementation guidance, internal assessment support, and preparation for the formal assessment.
The HITRUST CSF is a comprehensive cybersecurity and risk management framework that brings together requirements from multiple security and compliance frameworks. It supports risk-based assessments and can help organisations create a more consistent approach to protecting sensitive information.
What Is HITRUST CSF Certification?
HITRUST CSF Certification is an independent assurance process that evaluates whether an organisation has established and maintained the security controls required for its selected HITRUST assessment and certification scope.
The HITRUST CSF is designed to support organisations that need to manage cybersecurity, privacy, regulatory, and third-party risk through a structured control framework. It is particularly relevant to organisations that process sensitive information and need to demonstrate stronger security practices to customers, partners, regulators, or other stakeholders.
HITRUST currently provides different assurance options, including foundational i1, threat-adaptive r2, and other tailored assurance approaches. The appropriate option depends on the organisation’s risk profile, business requirements, systems, and stakeholder expectations.
What Does the HITRUST CSF Cover?
The HITRUST CSF brings together security and compliance requirements into a structured control environment. Depending on the assessment selected, organisations may need to address areas such as:
- Information security
- Access control
- Risk management
- Incident management
- Business continuity
- Data protection
- Privacy
- Third-party risk
- Vulnerability management
- Security awareness
- Policy and governance
- Technical and operational controls
The exact requirements depend on the selected HITRUST assessment, scope, and current HITRUST requirements.
Why Is HITRUST CSF Certification Important in Chennai?
HITRUST CSF Certification is important because Chennai has a large and growing ecosystem of hospitals, healthcare providers, medical technology companies, healthcare software businesses, research organisations, laboratories, and IT service providers.
The city’s technology and healthcare activity is spread across locations such as Guindy, Taramani, Tharamani, Perungudi, OMR, Sholinganallur, Ambattur, Nungambakkam, T Nagar, Velachery, Adyar, and the Chennai IT corridor. Organisations operating from these areas may exchange sensitive information across hospitals, cloud platforms, healthcare applications, laboratories, insurers, vendors, and other third parties.
Chennai’s healthcare technology ecosystem also includes organisations operating around IIT Madras Research Park and Taramani, while Perungudi and the OMR corridor have a strong concentration of technology and healthcare-related businesses.
For example, healthcare technology companies operate from areas such as Perungudi and Taramani, while major healthcare providers are located in central Chennai and other important healthcare clusters. This makes information security and third-party risk management important considerations for organisations working across Chennai’s healthcare ecosystem.
HITRUST provides a structured approach for demonstrating that security controls are being managed and assessed rather than relying only on informal security practices.
Benefits of HITRUST CSF Certification in Chennai
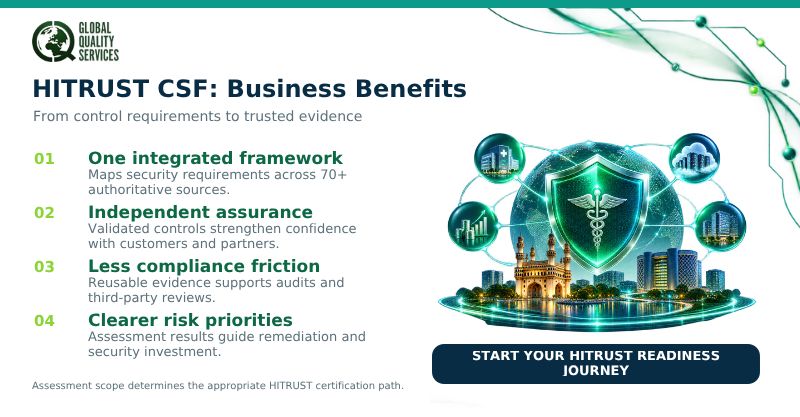
HITRUST CSF Certification can help Chennai organisations strengthen security controls, improve risk management, and demonstrate a structured approach to protecting sensitive information.
Stronger Information Security
A HITRUST-based assessment encourages organisations to evaluate security controls across different areas of their operations. This can help identify weaknesses that may otherwise remain unnoticed.
Better Protection of Sensitive Data
Healthcare organisations deal with highly sensitive patient and health information. A structured control framework can help organisations improve how this information is protected, accessed, stored, transmitted, and managed.
Improved Customer and Partner Confidence
Customers and business partners increasingly want evidence that suppliers and service providers have appropriate security controls. HITRUST assurance can provide additional evidence of an organisation’s approach to information security and risk management.
Better Risk Management
HITRUST uses a risk-based approach that helps organisations identify and address security risks based on their business environment and assessment requirements.
Support for Regulatory and Contractual Requirements
Organisations may face requirements from customers, regulators, contracts, and industry-specific obligations. HITRUST can provide a structured control framework that helps organisations organise and demonstrate their security practices.
Improved Audit Readiness
Preparing for a HITRUST assessment requires organisations to collect evidence, review controls, address gaps, and establish appropriate documentation. This can improve overall audit readiness.
Support for Global Business
Chennai-based technology and healthcare organisations working with international customers may need to demonstrate mature information security practices. HITRUST assurance can help support these business relationships where HITRUST is requested or recognised by the customer or stakeholder.
Who Should Consider HITRUST CSF Certification in Chennai?
HITRUST CSF Certification is particularly relevant to organisations that handle sensitive information or provide technology and services to organisations that have strict security requirements.
Hospitals and Healthcare Providers
Hospitals and healthcare networks can consider HITRUST when they manage electronic patient information, clinical systems, digital records, connected medical systems, or other sensitive healthcare data.
This may include hospitals and healthcare groups operating in areas such as Greams Road, Nungambakkam, Vadapalani, Adyar, Anna Nagar, T Nagar, OMR, Perungudi, and other healthcare centres across Chennai.
Healthcare Technology Companies
Healthcare software providers, health technology companies, medical software developers, and digital health platforms can use HITRUST to establish a structured security and risk management approach.
Chennai’s technology corridor, particularly areas such as Taramani, Perungudi, Thoraipakkam, Sholinganallur, and OMR, is home to many technology-focused organisations that may work with healthcare information and healthcare clients.
Diagnostic Laboratories
Diagnostic and pathology laboratories manage patient records, reports, test results, billing information, and other sensitive data. HITRUST can help such organisations establish a structured approach to information protection.
Medical Device and Healthcare Product Companies
Companies developing connected healthcare products, medical technologies, and digital health solutions may also consider HITRUST when their systems process or connect to sensitive information.
Healthcare SaaS Providers
SaaS companies supporting hospitals, clinics, laboratories, insurance companies, or other healthcare organisations may face customer security requirements that make HITRUST relevant.
Healthcare BPO and IT Service Providers
Organisations providing medical billing, claims processing, healthcare support, data processing, cloud services, or IT services to healthcare organisations may also benefit from a structured HITRUST assessment.
HITRUST CSF Certification Process in Chennai
The certification process begins with understanding the organisation’s business, systems, information flows, risks, and required assessment scope.
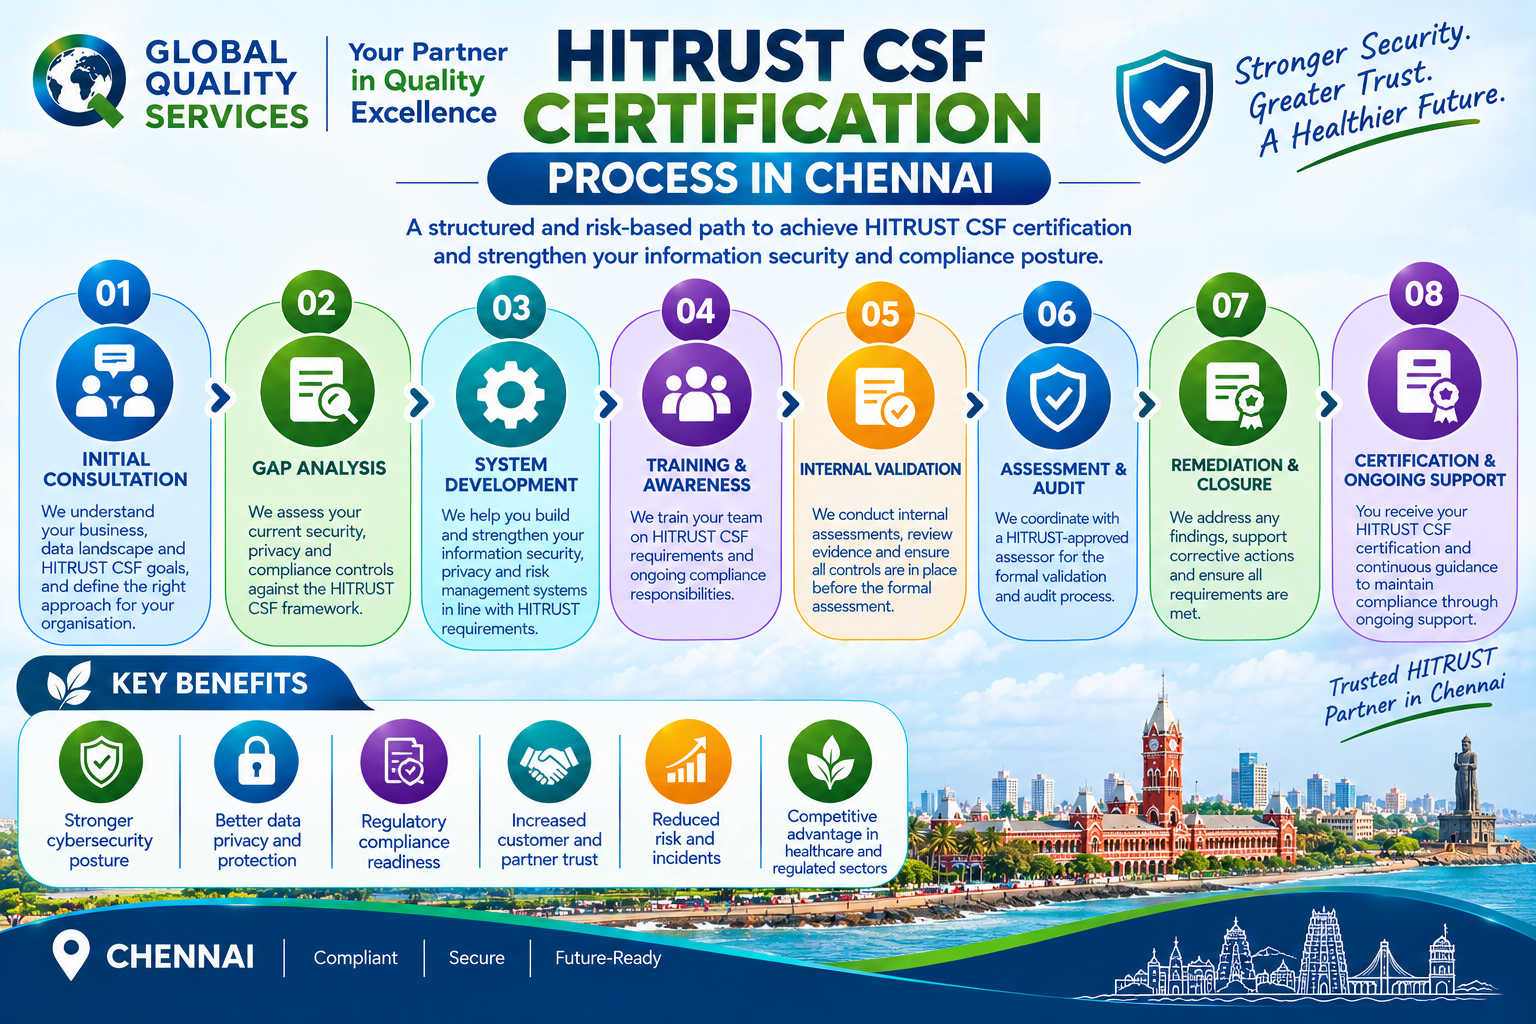
Step 1: Understand the Certification Requirement
The first step is to determine why the organisation needs HITRUST and what its customers, partners, contracts, or internal security objectives require.
GQS can help the organisation understand the certification pathway and identify the most suitable assessment approach.
Step 2: Define the Scope
The organisation needs to identify the business units, applications, systems, locations, processes, and information that will fall within the assessment scope.
A clearly defined scope helps prevent unnecessary assessment effort and ensures that the right controls are reviewed.
Step 3: Conduct a Gap Assessment
Existing policies, procedures, technical controls, records, and security practices are reviewed against the applicable HITRUST requirements.
The gap assessment helps identify what is already in place and what needs improvement.
Step 4: Develop or Improve Documentation
Organisations may need to establish or improve policies, procedures, risk records, access control documentation, incident response processes, business continuity documentation, vendor management records, security awareness records, and other evidence.
Step 5: Address Security Gaps
The identified gaps are prioritised according to risk and assessment requirements. Organisations then work on corrective actions and improvements before the formal assessment.
Step 6: Prepare Evidence
Evidence is an important part of the assessment. Organisations need to demonstrate that controls are not only documented but are operating as required.
GQS can help teams understand evidence expectations and prepare their documentation and records for assessment.
Step 7: Formal HITRUST Assessment
The organisation proceeds with the applicable HITRUST assessment through the appropriate assessment process.
HITRUST states that certification is based on the assessment results and that certification decisions are reviewed and approved by HITRUST.
Step 8: Maintain Certification
Certification is not the end of the security programme. Organisations need to continue monitoring controls, maintaining evidence, addressing risks, and meeting applicable ongoing requirements.
HITRUST’s current assurance portfolio includes assessment options with different validity periods, so organisations should plan ongoing maintenance according to the specific assurance product and current HITRUST requirements.
HITRUST CSF Certification Across Chennai
GQS can support organisations located across Chennai and its major commercial, technology, industrial, and healthcare areas.
HITRUST CSF Certification in OMR
Organisations operating along Old Mahabalipuram Road can benefit from structured information security and risk management practices, particularly where technology companies provide services to healthcare organisations or process sensitive data.
HITRUST CSF Certification in Perungudi
Perungudi is an important technology and business location in Chennai. Healthcare technology, software, IT services, and data-driven businesses in this area may consider HITRUST when working with customers that require strong cybersecurity assurance.
HITRUST CSF Certification in Taramani
Taramani has a strong technology, research, and healthcare innovation presence. Organisations working on healthcare technology, digital health, medical research, and software solutions can evaluate HITRUST as part of their security assurance strategy.
HITRUST CSF Certification in Thoraipakkam
Technology and service organisations in Thoraipakkam may need structured security controls when providing services to healthcare companies, hospitals, insurers, or global customers.
HITRUST CSF Certification in Guindy
Guindy is one of Chennai’s established business and industrial areas. Organisations handling sensitive business, employee, customer, or healthcare-related information can use a structured security framework to improve risk management.
HITRUST CSF Certification in Ambattur
Ambattur has a significant industrial and business presence. Organisations combining manufacturing, technology, healthcare products, or digital systems can assess whether HITRUST is relevant to their information security requirements.
HITRUST CSF Certification in Nungambakkam
Nungambakkam is an established healthcare and commercial area in Chennai. Hospitals, clinics, professional service providers, and technology-enabled businesses handling sensitive information can consider HITRUST where customer or contractual requirements call for it.
HITRUST CSF Certification in T Nagar
Businesses operating in T Nagar and surrounding commercial areas can seek HITRUST support when their systems or services involve sensitive customer, healthcare, payment, or business information.
How HITRUST Can Support Chennai’s Growing Healthcare Technology Ecosystem
Chennai is becoming increasingly connected through digital healthcare, cloud applications, electronic records, telemedicine, healthcare software, connected devices, and data-driven services.
This creates opportunities but also increases the need for stronger information security controls.
A HITRUST programme can help organisations move from isolated security activities to a more organised control structure. It can also help security teams establish evidence that controls are operating consistently.
For healthcare technology organisations working with international customers, HITRUST can also become an important part of their customer assurance strategy when it is specifically requested by the customer or business partner.
Future Benefits of HITRUST CSF Certification
HITRUST can provide long-term value when certification is treated as part of an organisation’s continuing security programme rather than as a one-time compliance exercise.
Stronger Cybersecurity Maturity
Regular review of security controls can help organisations identify weaknesses earlier and improve their overall cybersecurity maturity.
Easier Customer Security Reviews
Organisations may receive fewer repetitive questions from customers when they can provide recognised assurance and structured evidence for their security programme.
Better Third-Party Risk Management
Healthcare organisations depend on software vendors, cloud providers, IT service providers, laboratories, consultants, and other third parties. A structured framework can help improve vendor and third-party risk management.
Greater Business Readiness
As healthcare and technology businesses expand into new markets, they may encounter more demanding customer security requirements. A mature information security programme can make these requirements easier to manage.
Continuous Security Improvement
The value of HITRUST extends beyond certification. Organisations can use assessment findings to improve policies, controls, monitoring, risk management, and security governance over time.
Why Choose Global Quality Services for HITRUST CSF Certification in Chennai?
Global Quality Services provides structured certification consulting and compliance support to organisations preparing for information security and management system certifications.
For HITRUST CSF projects in Chennai, GQS can help organisations understand their requirements, identify gaps, organise documentation, review controls, prepare evidence, and improve assessment readiness.
If your organisation operates in Chennai and handles sensitive healthcare, customer, employee, financial, or business information, HITRUST CSF may provide a structured approach to strengthening information security and demonstrating assurance to customers and business partners.
Whether you operate from OMR, Perungudi, Taramani, Thoraipakkam, Guindy, Ambattur, Nungambakkam, T Nagar, Sholinganallur, Adyar, Velachery, or another part of Chennai, GQS can help you assess your current position and plan the next steps toward HITRUST CSF certification.
Contact Global Quality Services to discuss your HITRUST CSF requirements, assessment scope, current controls, and certification readiness.
Frequently Asked Questions About HITRUST CSF Certification in Chennai
1. What is HITRUST CSF Certification?
HITRUST CSF Certification is an assurance process used to assess an organisation’s security controls against applicable HITRUST requirements. It provides a structured way to demonstrate that an organisation has established and operates controls for managing information security and related risks.
2. Is HITRUST CSF only for hospitals in Chennai?
No. HITRUST can be relevant to hospitals, healthcare technology companies, laboratories, SaaS providers, IT service providers, medical technology companies, and other organisations that handle sensitive information. The framework is industry-agnostic, although it has strong relevance to healthcare and organisations dealing with sensitive data.
3. How long does HITRUST CSF Certification take in Chennai?
The timeline depends on the organisation’s scope, existing controls, documentation, technology environment, assessment type, and the number of gaps that need to be addressed. A gap assessment should be completed first so that the organisation can develop a more realistic certification plan.
4. Can a small healthcare technology company in Chennai pursue HITRUST?
Yes. The appropriate HITRUST assurance option depends on the organisation’s risk profile, business requirements, scope, and customer expectations. Smaller organisations should first determine what assurance their customers actually require before selecting an assessment pathway. HITRUST currently offers different assurance approaches, including i1 and r2.
5. Does GQS issue the HITRUST certificate?
HITRUST certification is granted through the HITRUST assurance process. GQS can support organisations with readiness, gap assessment, documentation, control review, evidence preparation, and assessment preparation. The final certification decision is made through the applicable HITRUST process.