Organisations in Noida are increasingly dependent on cloud platforms, software applications, healthcare technology, digital services, and connected business systems. As the amount of sensitive information handled by these organisations grows, strong information security and risk management become essential.
HITRUST CSF Certification in Noida provides a structured approach for evaluating and improving information security, privacy, risk management, and compliance controls.
Global Quality Services (GQS) supports organisations in Noida with HITRUST CSF certification readiness through gap assessment, documentation review, control assessment, risk management support, evidence preparation, and assessment readiness.
HITRUST describes the CSF as a comprehensive, threat-adaptive control library that harmonises more than 60 frameworks and standards. It supports tailored, risk-based assessments across different industries.
What Is HITRUST CSF Certification?
HITRUST CSF Certification is an assurance process that evaluates an organisation’s applicable security controls against the requirements of the HITRUST framework.
The HITRUST CSF brings together security and compliance requirements into a structured control framework. This helps organisations assess their current security practices, identify gaps, manage risks, and demonstrate that appropriate controls are in place.
HITRUST currently offers several assurance products. These include e1 for foundational cybersecurity assurance, i1 for threat-adaptive assurance, and r2 for more tailored and extensive assurance requirements. The right option depends on the organisation’s risk profile, business needs, systems, and customer requirements.
For a Noida-based organisation, the first step should therefore be understanding the business requirement and selecting an assessment pathway that matches the organisation’s actual needs.
Why Is HITRUST CSF Certification Important in Noida?
HITRUST CSF Certification is important in Noida because the city has a strong presence of IT companies, software businesses, healthcare service providers, technology-enabled businesses, and organisations serving international customers.
Noida is part of the wider National Capital Region and has developed into an important technology and business hub. Organisations operating here may process personal information, healthcare information, customer records, intellectual property, financial information, and other sensitive data.
Noida also has a growing healthcare technology ecosystem. Businesses involved in medical billing, healthcare software, pharmaceutical services, health technology, and data processing may need to demonstrate strong information security practices to customers and business partners.
Organisations may also need to consider Indian regulatory and industry requirements relevant to their operations. Depending on the business, useful government resources may include the Ministry of Electronics and Information Technology (MeitY), Central Drugs Standard Control Organisation (CDSCO), Department of Pharmaceuticals, and the Department of IT and Electronics, Government of Uttar Pradesh.
These resources can be useful when organisations are reviewing their broader information security, digital technology, healthcare, pharmaceutical, or regulatory responsibilities.
Benefits of HITRUST CSF Certification in Noida
HITRUST CSF Certification can help organisations strengthen security controls, improve risk management, and provide greater assurance to customers and business partners.
Stronger Information Security
HITRUST provides a structured way to review security controls across an organisation. This can help identify weaknesses and create a more consistent approach to information security.
Better Protection of Sensitive Data
Organisations in Noida may handle personal information, healthcare records, customer information, intellectual property, financial information, and other confidential data. A structured security framework can help improve how this information is protected.
Improved Customer Confidence
Customers increasingly want evidence that their service providers have appropriate security controls. HITRUST assurance can provide additional evidence of an organisation’s security and risk management practices when HITRUST is required or recognised by the customer.
Better Risk Management
HITRUST uses a risk-based approach that allows security requirements to be considered according to the organisation’s environment, systems, risks, and business needs.
Supports Multiple Security Requirements
Organisations often need to address several security and compliance requirements at the same time. The HITRUST CSF brings multiple authoritative sources into a common control framework, which can make security management more organised.
Improved Audit Readiness
The certification preparation process requires organisations to review controls, maintain records, collect evidence, and address identified gaps. This can improve overall audit readiness.
Supports International Business
Many Noida-based IT and technology companies serve customers outside India. A recognised security assurance framework can help organisations respond to customer security requirements and vendor assessments.
Who Should Consider HITRUST CSF Certification in Noida?
HITRUST CSF Certification can be relevant to organisations that handle sensitive information or provide technology and services to customers with strict security requirements.
Healthcare Organisations
Hospitals, healthcare providers, clinics, healthcare networks, and digital healthcare businesses can consider HITRUST when they manage sensitive patient or health information.
Healthcare Technology Companies
Health-tech companies, healthcare software providers, medical billing platforms, digital health applications, and healthcare SaaS businesses can use a structured security framework to improve their security posture.
IT and Software Companies
Noida has a large technology and software ecosystem. IT service providers, SaaS companies, cloud service providers, software developers, and managed service providers may consider HITRUST when their customers require stronger security assurance.
Pharmaceutical and Life Sciences Organisations
Companies involved in pharmaceutical services, research, healthcare products, clinical data, and life sciences may handle highly sensitive information. HITRUST can be considered where the organisation’s customers or stakeholders require this type of assurance.
Healthcare BPO and Data Processing Companies
Organisations providing medical billing, claims processing, healthcare administration, data processing, or other outsourced healthcare services may benefit from a structured security and risk management framework.
Organisations Serving International Customers
Businesses that work with overseas healthcare providers, technology companies, insurers, or other organisations may encounter HITRUST requirements during customer due diligence or vendor security assessments.
HITRUST CSF Certification Process in Noida
The HITRUST certification journey begins with understanding the organisation’s requirements and assessment scope. A structured preparation process can make the assessment easier to manage.
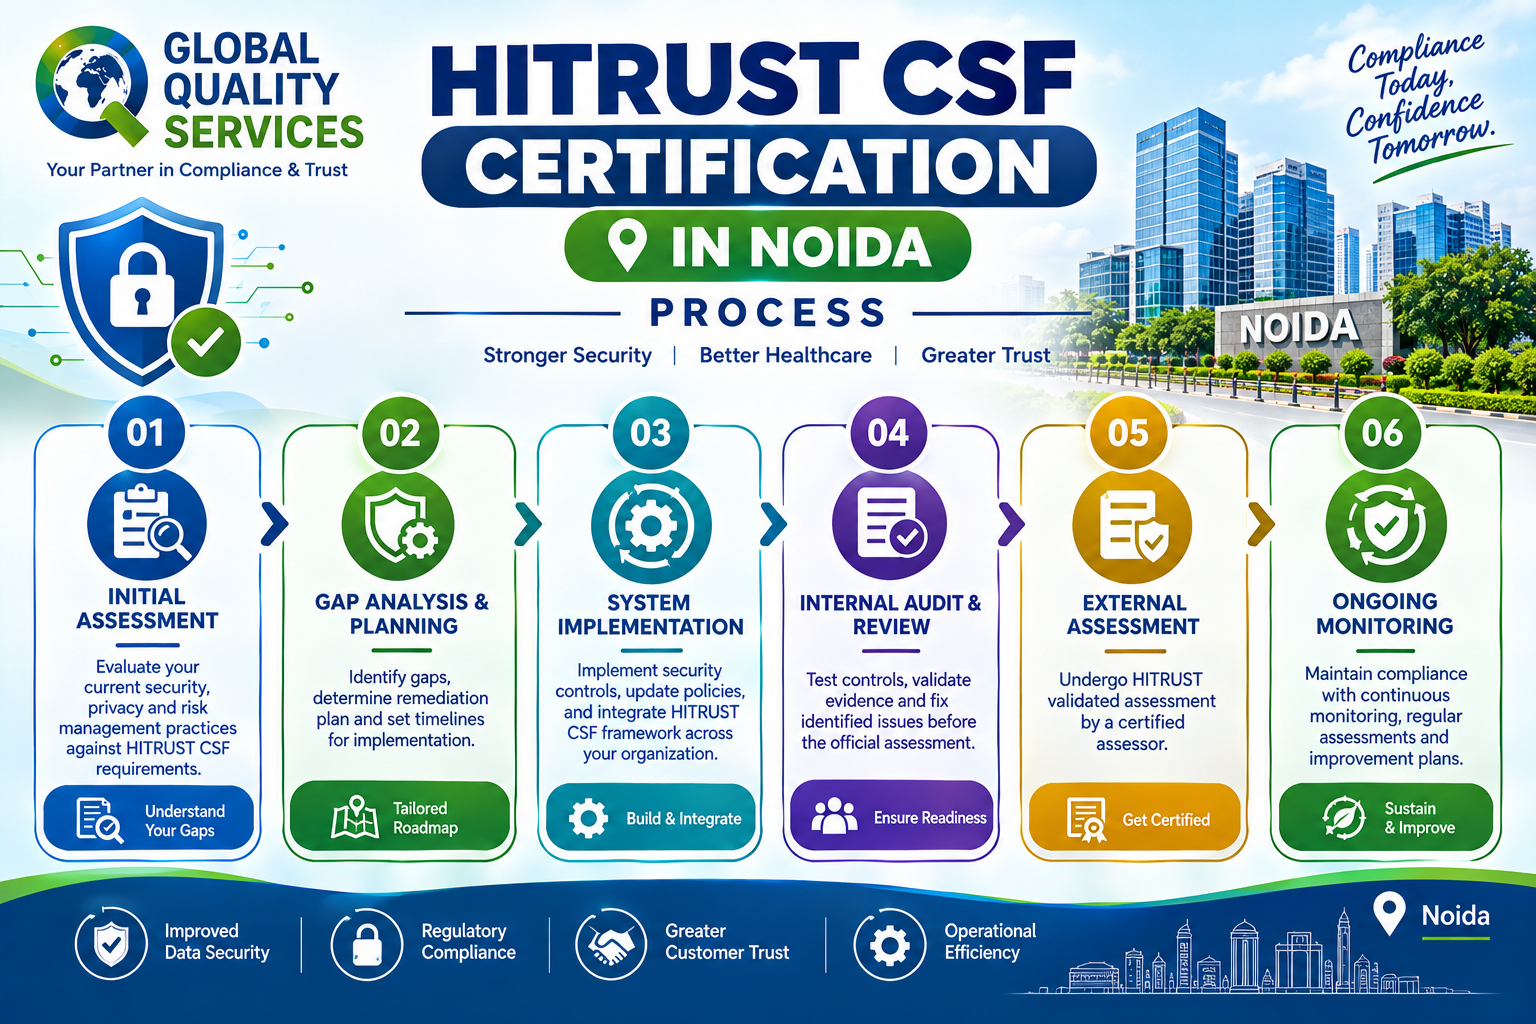
Step 1: Understand the Business Requirement
The first step is to identify why the organisation needs HITRUST.
The requirement may come from a customer, business partner, contractual obligation, internal security objective, or the need to strengthen the organisation’s overall security programme.
Step 2: Select the Appropriate Assessment Path
HITRUST offers different assurance products with different levels of requirements. The organisation should identify the assessment pathway that matches its business, risk profile, customer expectations, and scope.
The current HITRUST portfolio includes e1, i1, and r2 assurance options.
Step 3: Define the Scope
The organisation identifies the systems, applications, business units, processes, locations, and information that will be included.
Clear scope definition helps ensure that the assessment focuses on the systems and processes that actually need to be evaluated.
Step 4: Conduct a Gap Assessment
Existing policies, procedures, technical controls, operational processes, and records are reviewed against applicable HITRUST requirements.
The gap assessment identifies what is already in place and where improvements are needed.
Step 5: Improve Policies and Controls
Gaps identified during the assessment are addressed through appropriate corrective actions.
This may include improving access controls, risk management, incident response, vulnerability management, vendor management, business continuity, security awareness, and data protection practices.
Step 6: Prepare Documentation and Evidence
Organisations need to demonstrate that their controls are not only documented but are operating as required.
GQS can help teams understand applicable evidence requirements and organise documentation and records for assessment readiness.
Step 7: Complete the Formal Assessment
The organisation proceeds with the applicable HITRUST assessment through the appropriate assessment process.
HITRUST states that certification involves a validated assessment and that certification decisions are reviewed and approved by HITRUST.
Step 8: Maintain Security Controls
HITRUST certification should be supported by ongoing security management. Organisations need to continue monitoring controls, managing risks, maintaining evidence, and addressing changes to their systems and business environment.
HITRUST CSF Certification in Key Noida Areas
GQS can support organisations across Noida and nearby business and technology clusters.
Some important areas include:
- Sector 62: A major technology and IT business area with software, healthcare technology, and other technology-focused organisations.
- Sector 63: An established industrial and IT area with businesses involved in technology, services, manufacturing, and data-driven operations.
- Sector 16 and Sector 18: Important commercial areas with offices, service companies, and technology-enabled businesses.
- Sector 125, 126, 127 and 132: Growing corporate and technology locations along the Noida Expressway.
- Sector 135 and Sector 142: Major corporate and IT locations with businesses serving domestic and international customers.
- Noida Special Economic Zone: An important location for technology, export-oriented, and business service organisations.
- Greater Noida: Organisations operating in Greater Noida and nearby industrial and technology areas can also seek HITRUST CSF readiness support based on their business requirements.
HITRUST CSF and Noida’s Technology Ecosystem
Noida’s technology ecosystem includes software companies, IT service providers, healthcare technology businesses, business process service providers, and organisations serving customers across different countries.
These businesses often depend on cloud infrastructure, applications, APIs, databases, remote access, third-party platforms, and external service providers.
As a result, information security cannot be limited to one department. Security controls need to cover people, processes, technology, suppliers, and business operations.
HITRUST can provide a structured control framework for organisations that need to bring these different security requirements together.
The framework is also updated over time. HITRUST released CSF version 11.8.0 in May 2026, with changes including continued consolidation of requirement statements and new or refreshed authoritative source mappings.
HITRUST CSF for Healthcare and Life Sciences Organisations in Noida
Healthcare and life sciences organisations require particular attention to information security because their systems may contain sensitive patient, clinical, research, pharmaceutical, or business information.
A Noida organisation working in this sector may also interact with hospitals, laboratories, healthcare professionals, technology vendors, pharmaceutical companies, and international customers.
HITRUST can help create a structured approach to security controls across these relationships.
For organisations involved in pharmaceuticals and medical products, relevant Indian government bodies may include the Central Drugs Standard Control Organisation (CDSCO) and the Department of Pharmaceuticals, Ministry of Chemicals and Fertilizers. For organisations dealing with digital technology and information security, the Ministry of Electronics and Information Technology (MeitY) can also be a useful official reference.
These government resources should be considered alongside the organisation’s specific contractual, regulatory, and industry requirements.
Future Benefits of HITRUST CSF Certification
HITRUST can provide long-term value when certification is treated as part of an ongoing information security programme.
Improved Cybersecurity Maturity
Regular review of controls can help organisations identify weaknesses and improve their cybersecurity practices over time.
Easier Customer Security Reviews
Organisations with structured security controls and appropriate evidence may be better prepared to respond to customer questionnaires and security due diligence.
Better Third-Party Risk Management
Technology and healthcare organisations depend on vendors, cloud providers, software suppliers, consultants, and other third parties. A structured framework can help organisations improve their approach to third-party risk.
Stronger International Business Readiness
Noida-based businesses serving international customers may face increasingly detailed security requirements. A mature security programme can make these requirements easier to manage.
Continuous Improvement
The assessment process can help organisations establish a cycle of reviewing controls, identifying risks, implementing improvements, and maintaining evidence.
Why Choose Global Quality Services for HITRUST CSF Certification in Noida?
Global Quality Services supports organisations with certification consulting, compliance readiness, and management system improvement.
For HITRUST CSF projects in Noida, GQS focuses on helping organisations understand their requirements, identify gaps, improve applicable controls, prepare documentation, and become ready for the relevant assessment.
\
If your organisation operates in Noida and handles sensitive healthcare information, personal data, customer information, intellectual property, research data, or other confidential information, HITRUST CSF can provide a structured approach to improving information security and demonstrating assurance.
Whether you operate from Sector 62, Sector 63, Sector 16, Sector 18, Sector 125, Sector 126, Sector 127, Sector 132, Sector 135, Sector 142, Noida Special Economic Zone, or Greater Noida, GQS can help you understand your current security position and prepare for the applicable HITRUST assessment.
Contact Global Quality Services to discuss your HITRUST CSF requirements, assessment scope, existing controls, and certification readiness.
Frequently Asked Questions About HITRUST CSF Certification in Noida
1. What is HITRUST CSF Certification?
HITRUST CSF Certification is an assurance process that evaluates an organisation’s applicable security controls against HITRUST requirements. It provides a structured way to demonstrate that an organisation has established and maintains appropriate security and risk management controls.
2. Is HITRUST CSF Certification only for healthcare companies?
No. HITRUST can be relevant to healthcare organisations, IT companies, SaaS providers, pharmaceutical organisations, laboratories, BPOs, and other businesses that manage sensitive information or have customer requirements for recognised security assurance.
3. How long does HITRUST CSF Certification take in Noida?
The timeline depends on the assessment type, organisation size, scope, existing controls, technology environment, documentation, and number of gaps identified. A gap assessment can help establish a more realistic timeline.
4. Can a Noida-based SaaS company pursue HITRUST CSF Certification?
Yes. A SaaS company can consider HITRUST when it manages sensitive information or serves customers that require HITRUST assurance. The appropriate assessment should be selected based on the company’s business requirements, risk profile, scope, and customer expectations.
5. Does GQS issue the HITRUST CSF certificate?
HITRUST certification is granted through the applicable HITRUST assurance process. GQS can support organisations with readiness activities including gap assessment, documentation review, control preparation, evidence preparation, and assessment readiness. HITRUST states that certification decisions are reviewed and approved by HITRUST.