Organisations in Delhi handle large volumes of personal, healthcare, financial, customer, and business information every day. Hospitals, healthcare providers, IT companies, SaaS businesses, research organisations, and service providers need effective controls to protect this information from security threats and unauthorised access.
HITRUST CSF Certification in Delhi provides a structured approach to assessing information security, privacy, risk management, and compliance controls. It can help organisations identify gaps, strengthen security practices, improve risk management, and demonstrate their commitment to protecting sensitive information.
Global Quality Services (GQS) supports organisations in Delhi with HITRUST CSF certification readiness, including gap assessment, documentation review, control assessment, risk management support, evidence preparation, and assessment preparation.
HITRUST describes the CSF as a comprehensive control framework that supports risk-based security and compliance assessments. The framework brings together requirements from multiple authoritative sources and can be tailored to an organisation’s risk and business environment.
What Is HITRUST CSF Certification?
HITRUST CSF Certification is an assurance process that evaluates an organisation’s applicable security controls against the requirements of the HITRUST framework.
The HITRUST CSF brings different security, privacy, and compliance requirements into a structured control framework. This allows organisations to assess their current controls, identify weaknesses, manage risks, and prepare evidence for an independent assessment.
The appropriate HITRUST assessment depends on the organisation’s business needs, risk profile, systems, scope, and customer requirements. Organisations should first understand what type of HITRUST assurance their customers or stakeholders require before selecting an assessment pathway.
HITRUST also maintains a list of authorised external assessors and readiness licensees. Organisations seeking formal readiness or validated assessment services should verify the provider’s status through HITRUST.
Why Is HITRUST CSF Certification Important in Delhi?
HITRUST CSF Certification is important in Delhi because the city has a large healthcare, technology, government, financial, professional services, and business ecosystem.
Organisations across Delhi may manage sensitive information through cloud applications, healthcare systems, databases, software platforms, digital services, employee systems, and third-party applications.
Delhi also has a significant healthcare infrastructure. The Department of Health and Family Welfare, Government of NCT of Delhi oversees healthcare responsibilities across the capital, while the Directorate General of Health Services (DGHS) is a major agency involved in healthcare delivery.
For technology and digital businesses, the Information Technology Department, Government of NCT of Delhi is another useful official reference. The department works on technology-related matters and IT initiatives across Delhi Government departments and autonomous bodies.
These government resources can be useful when organisations are reviewing their wider technology, healthcare, data protection, and regulatory responsibilities alongside their HITRUST requirements.
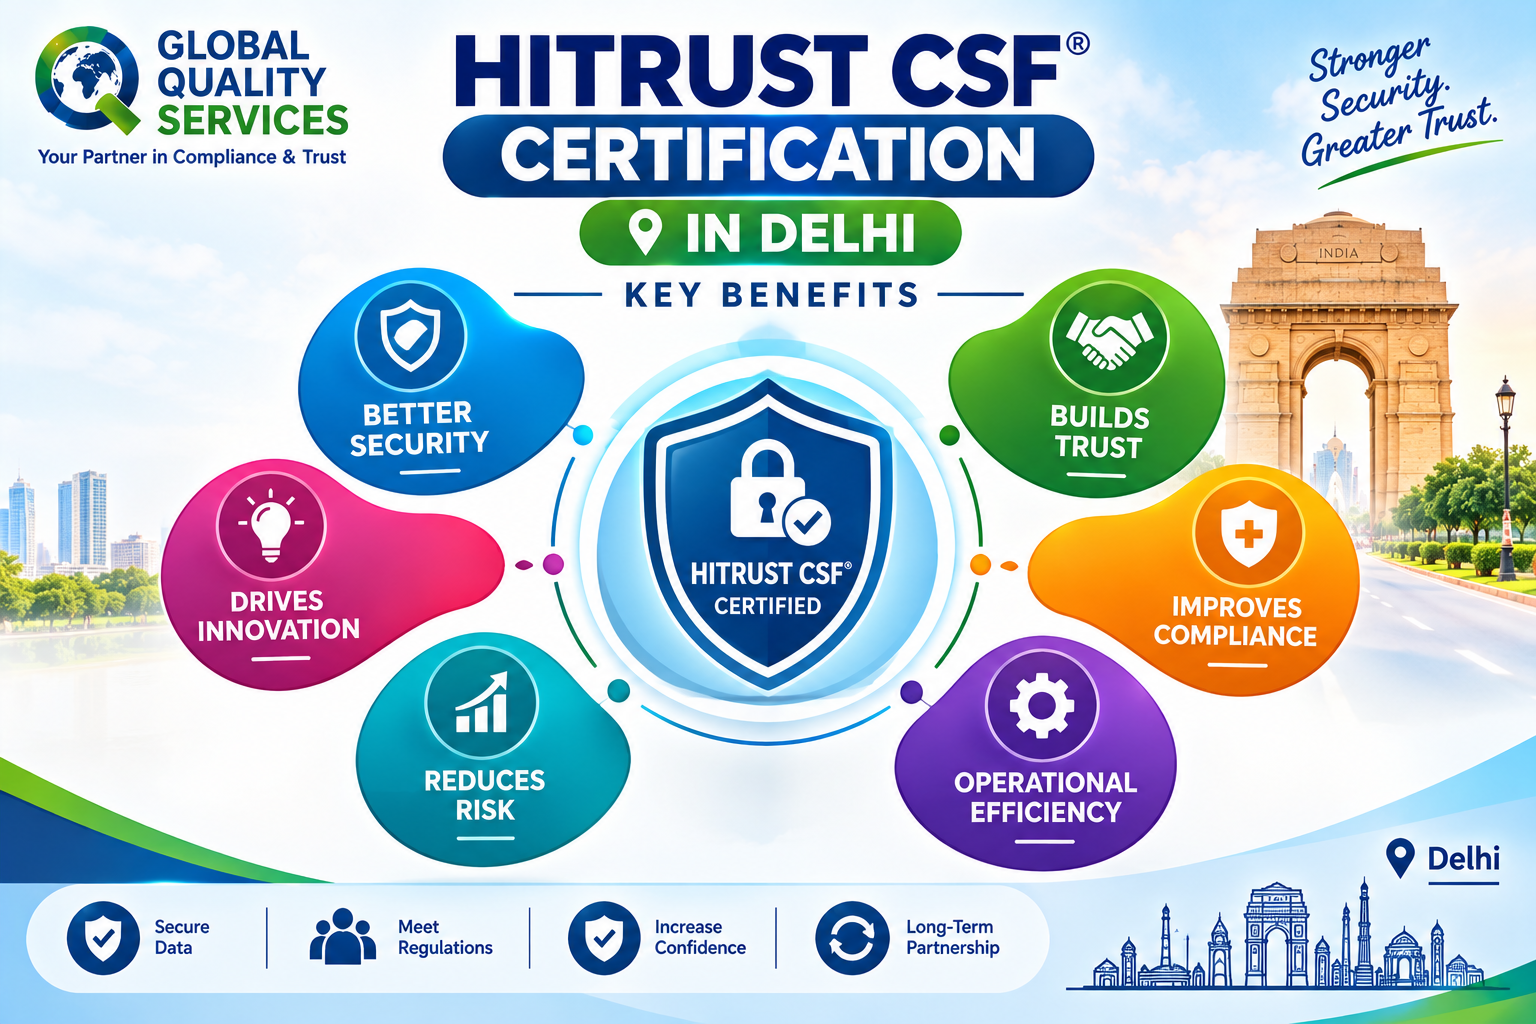
Benefits of HITRUST CSF Certification in Delhi
HITRUST CSF Certification can help Delhi-based organisations improve their security controls and provide stronger assurance to customers, partners, and other stakeholders.
Stronger Information Security
HITRUST provides a structured way to review security controls across different parts of an organisation. This can help identify weaknesses and create a more consistent security programme.
Better Protection of Sensitive Information
Healthcare providers, technology companies, financial service providers, and other organisations may handle personal and confidential information. A structured security framework can help improve how this information is protected.
Greater Customer Confidence
Customers and business partners may ask service providers to demonstrate their cybersecurity practices. HITRUST assurance can support these requirements when HITRUST is requested or recognised by the customer.
Improved Risk Management
HITRUST follows a risk-based approach. This allows organisations to consider their specific systems, processes, risks, and business environment when managing security controls.
Better Audit Preparation
Preparing for HITRUST requires organisations to review their controls, maintain documentation, collect evidence, and address identified gaps. This can improve overall audit readiness.
Support for Multiple Compliance Requirements
Organisations may have to address several security, privacy, contractual, and industry requirements. A structured framework can help bring these requirements into a more manageable control environment.
Support for International Business
Delhi-based IT, healthcare, SaaS, and professional service organisations may work with customers outside India. Strong information security assurance can help when international customers conduct security due diligence or require specific certifications.
Who Should Consider HITRUST CSF Certification in Delhi?
HITRUST CSF Certification can be relevant to organisations that manage sensitive information or provide services to customers with demanding security requirements.
Healthcare Organisations
Hospitals, clinics, healthcare networks, diagnostic centres, medical service providers, and digital healthcare companies can consider HITRUST when they manage patient or health information.
Healthcare Technology Companies
Health-tech companies, healthcare software providers, digital health platforms, medical billing systems, and healthcare SaaS providers may need to demonstrate strong information security controls to their customers.
IT and Software Companies
Delhi has a large technology and software ecosystem. IT service providers, SaaS companies, cloud service providers, software developers, and managed service providers can consider HITRUST when their customers require recognised security assurance.
Pharmaceutical and Life Sciences Organisations
Organisations involved in pharmaceutical services, medical products, research, clinical data, and life sciences may handle sensitive information and intellectual property. HITRUST can be considered when it aligns with their customer or business requirements.
BPO and Data Processing Organisations
Companies involved in healthcare BPO, claims processing, medical billing, data processing, customer support, and outsourced business services may benefit from a structured security and risk management framework.
Organisations Serving International Customers
Businesses serving international healthcare providers, technology companies, insurers, and other regulated organisations may encounter HITRUST requirements during vendor assessments and customer due diligence.
HITRUST CSF Certification Process in Delhi
The HITRUST certification journey begins by understanding the organisation’s business requirements, systems, risks, and assessment scope.
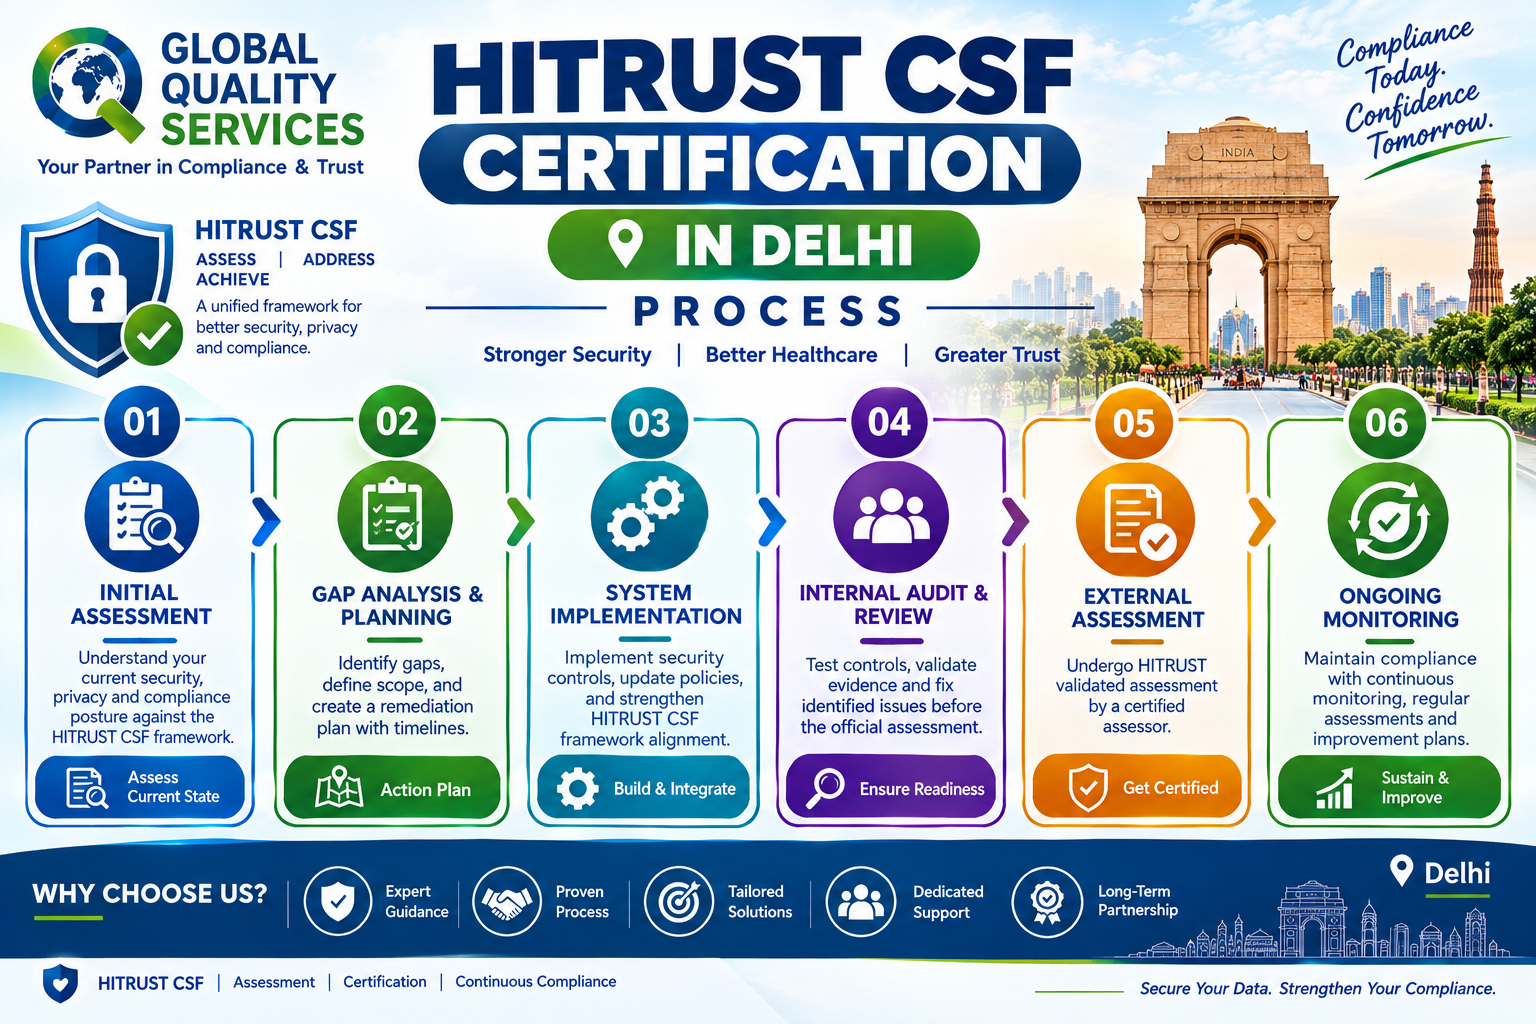
Step 1: Understand the Requirement
The organisation first identifies why HITRUST is required.
The requirement may come from a customer, contract, business partner, internal security objective, or the organisation’s need to strengthen its security programme.
Step 2: Determine the Assessment Scope
The organisation identifies the systems, applications, processes, business units, locations, and information that need to be included in the assessment.
A clear scope helps ensure that the assessment focuses on the environment that actually needs to be evaluated.
Step 3: Conduct a Gap Assessment
Existing policies, procedures, technical controls, operational practices, and security records are reviewed against the applicable HITRUST requirements.
The gap assessment identifies which controls are already established and where improvements are required.
Step 4: Improve Policies and Procedures
The organisation addresses documentation gaps and improves applicable policies and procedures.
These may include information security, access control, incident response, risk management, business continuity, vendor management, vulnerability management, security awareness, and data protection processes.
Step 5: Strengthen Security Controls
Identified gaps are addressed through appropriate corrective actions.
The improvements may involve technology, processes, people, monitoring, risk management, or documentation depending on the organisation’s assessment findings.
Step 6: Prepare Evidence
Organisations need to demonstrate that applicable controls are operating as required.
GQS can help teams understand evidence expectations and organise the relevant records before the formal assessment.
Step 7: Complete the Formal Assessment
The organisation proceeds through the applicable HITRUST assessment process with the appropriate authorised assessment organisation.
HITRUST states that certification decisions are reviewed and approved by HITRUST following the applicable assessment process.
Step 8: Maintain the Controls
HITRUST certification requires continued attention to security controls. Organisations should continue monitoring risks, maintaining evidence, reviewing controls, and addressing changes to systems and business processes.
HITRUST CSF Certification in Key Delhi Areas
GQS can support organisations across Delhi and nearby business and technology centres.
Some relevant areas include:
- Connaught Place: A major commercial centre with professional services, technology-enabled businesses, and corporate offices.
- Nehru Place: A well-known technology and electronics business hub with IT and software-related organisations.
- Okhla: An important business and industrial area with technology, healthcare, manufacturing, and service organisations.
- Saket: A major commercial and corporate area with healthcare, retail, professional services, and technology-enabled businesses.
- Dwarka: A growing commercial and institutional area with businesses and service organisations.
- Rohini: A major residential and commercial area with healthcare providers, professional services, and businesses.
- Patparganj: An established industrial and business area with manufacturing and service organisations.
- Mayur Vihar: A mixed commercial and residential area with healthcare, technology, and service businesses.
- Karol Bagh: A long-established commercial area with a wide range of businesses and professional services.
- Vasant Kunj: A corporate and commercial area with technology, healthcare, retail, and professional service organisations.
Organisations in these areas can evaluate HITRUST based on their information security requirements, industry, customer expectations, and assessment scope.
HITRUST CSF and Delhi’s Healthcare and Technology Ecosystem
Delhi’s healthcare and technology sectors rely heavily on digital systems and information exchange.
Hospitals and healthcare providers use electronic records, diagnostic systems, digital platforms, laboratory applications, billing systems, and connected technologies. Technology companies provide cloud services, software platforms, data processing, cybersecurity services, and other digital solutions.
This interconnected environment creates a need for clear controls around access, data protection, risk management, incident response, third-party relationships, and business continuity.
HITRUST can help organisations bring these areas into a structured control framework.
For organisations working with government healthcare systems or digital technology projects, official resources from the Department of Health and Family Welfare, Government of NCT of Delhi, the Directorate General of Health Services, and the Information Technology Department, Government of NCT of Delhi can also be useful when reviewing the wider operating and regulatory environment.
Future Benefits of HITRUST CSF Certification
HITRUST can provide long-term value when certification is treated as part of an ongoing security programme rather than as a one-time compliance activity.
Improved Cybersecurity Maturity
Regular control reviews can help organisations identify weaknesses and improve their security practices over time.
Easier Customer Security Reviews
Organisations with structured controls and appropriate evidence can be better prepared when customers conduct security questionnaires or vendor assessments.
Better Third-Party Risk Management
Businesses often depend on cloud providers, software suppliers, consultants, IT vendors, and other third parties. A structured control framework can help improve the way these risks are identified and managed.
Stronger International Business Readiness
Delhi-based organisations working with international customers may face increasingly detailed security requirements. A mature security programme can make these requirements easier to manage.
Continuous Security Improvement
HITRUST preparation can establish a process of reviewing controls, identifying risks, implementing corrective actions, and maintaining evidence.
Why Choose Global Quality Services for HITRUST CSF Certification in Delhi?
Global Quality Services supports organisations with certification consulting, compliance readiness, and management system improvement.
For HITRUST CSF projects in Delhi, GQS focuses on helping organisations understand their requirements, identify gaps, improve applicable controls, prepare documentation, and become ready for the relevant assessment.
GQS helps organisations understand the documentation and evidence required for assessment readiness and organise their records accordingly.
If your organisation operates in Delhi and manages healthcare information, personal data, customer information, intellectual property, research information, or other sensitive data, HITRUST CSF can provide a structured approach to strengthening information security.
Whether you operate from Nehru Place, Okhla, Connaught Place, Saket, Dwarka, Rohini, Patparganj, Mayur Vihar, Karol Bagh, Vasant Kunj, or another part of Delhi, GQS can help you understand your current security position and prepare for the applicable HITRUST assessment.
Contact Global Quality Services to discuss your HITRUST CSF requirements, assessment scope, existing controls, and certification readiness.
Frequently Asked Questions About HITRUST CSF Certification in Delhi
1. What is HITRUST CSF Certification?
HITRUST CSF Certification is an assurance process that evaluates an organisation’s applicable security controls against HITRUST requirements. It provides a structured way to demonstrate that appropriate information security and risk management controls have been established and are operating as required.
2. Is HITRUST CSF Certification only for healthcare organisations in Delhi?
No. HITRUST can be relevant to healthcare organisations, IT companies, SaaS providers, pharmaceutical businesses, laboratories, BPOs, data processing companies, and other organisations that manage sensitive information or have customer requirements for security assurance.
3. How long does HITRUST CSF Certification take in Delhi?
The timeline depends on the organisation’s size, assessment scope, existing controls, technology environment, documentation, and selected assessment pathway. A gap assessment can help determine the work required and provide a more realistic certification plan.
4. Can a Delhi-based IT or SaaS company pursue HITRUST CSF Certification?
Yes. IT and SaaS companies can consider HITRUST when they manage sensitive information or provide services to customers that require HITRUST assurance. The appropriate assessment should be selected based on the company’s scope, risk profile, business requirements, and customer expectations.
5. Does GQS issue the HITRUST CSF certificate?
HITRUST certification is granted through the applicable HITRUST assurance process. GQS can support organisations with readiness activities such as gap assessment, documentation review, control preparation, evidence preparation, and assessment readiness. HITRUST states that organisations seeking official readiness or validated assessment services should work with entities listed through its authorised assessor and readiness licensee programme.