s your organisation in Pune handling sensitive healthcare information, personal data, financial information, or business-critical systems? As organisations increasingly depend on cloud platforms, connected applications, and third-party service providers, demonstrating that security controls are properly designed and maintained has become increasingly important.
HITRUST CSF Certification in Pune provides organisations with a structured way to assess their cybersecurity controls, identify gaps, strengthen information security practices, and demonstrate a recognised level of assurance to customers and business partners.
Global Quality Services helps organisations in Pune prepare for HITRUST CSF assessments through structured gap assessment, documentation support, control readiness, remediation guidance, and assessment preparation.
What Is HITRUST CSF Certification?
HITRUST CSF is a comprehensive, threat-adaptive control framework that brings together requirements from more than 60 frameworks and standards. It is designed to help organisations assess cybersecurity and compliance controls according to their business risks and security needs.
- HITRUST offers different assurance options depending on the organisation’s risk profile and security maturity.
- HITRUST e1 provides foundational cybersecurity assurance and is based on 43 core controls. It can be suitable for organisations looking for a defined starting point for cybersecurity assurance.
- HITRUST i1 provides threat-adaptive assurance based on 182 control requirements and is intended for organisations with more established information security practices.
- HITRUST r2 provides a tailored, risk-based assessment for organisations with more complex environments and higher assurance requirements.
The appropriate assessment depends on factors such as organisational risk, regulatory expectations, information systems, customer requirements, and the complexity of the environment.
Why Is HITRUST CSF Certification Important for Pune Organisations?
Pune has a large concentration of technology, healthcare, pharmaceutical, engineering, manufacturing, and professional services organisations. Businesses operating in these sectors may process significant volumes of sensitive information across internal systems, cloud environments, applications, and third-party platforms.
HITRUST CSF can help organisations create a structured approach to security controls instead of managing cybersecurity requirements as disconnected activities.
For organisations working with healthcare providers, technology companies, enterprise customers, or international clients, a recognised security assurance framework can also make it easier to demonstrate that information security risks are being actively managed.
The framework can be particularly relevant where organisations need to address requirements related to access control, risk management, data protection, incident response, vulnerability management, business continuity, supplier relationships, and information security governance.
What Are the Benefits of HITRUST CSF Certification in Pune?
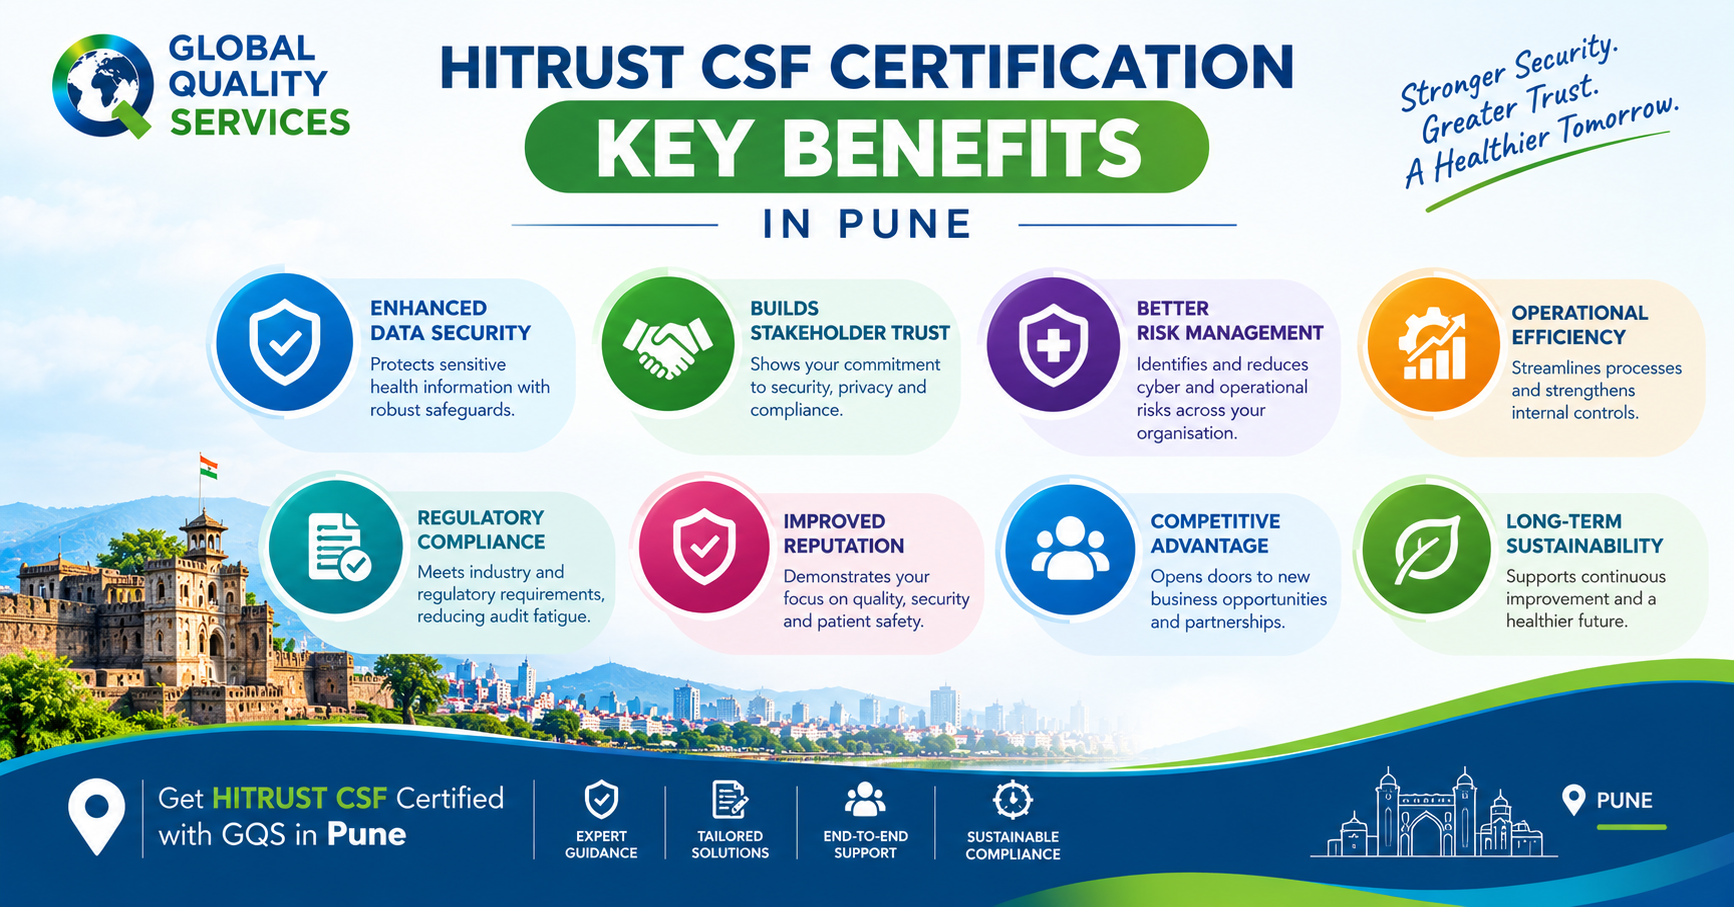
HITRUST CSF certification can provide several practical benefits for organisations operating in Pune.
Stronger Information Security Controls
The assessment process helps organisations examine their existing security controls and identify areas requiring improvement.
This can include access management, endpoint protection, network security, vulnerability management, incident response, data protection, security policies, and business continuity.
Better Customer and Partner Confidence
Customers increasingly want evidence that their service providers can protect sensitive information.
A HITRUST validated assessment and certification can provide structured assurance that an organisation’s security controls have undergone an established assessment process.
Improved Risk Management
HITRUST CSF follows a risk-based approach, helping organisations focus their security efforts on the risks and requirements that are relevant to their environment.
This can be particularly useful for organisations operating across multiple applications, locations, cloud platforms, and third-party services.
Support for Healthcare and Health-Tech Organisations
Healthcare organisations and health technology companies often deal with highly sensitive information. HITRUST can provide a structured framework for evaluating controls surrounding the protection of such information.
Pune’s healthcare technology and pharmaceutical ecosystem can therefore benefit from a security framework that brings multiple control requirements into a structured assessment model.
Better Preparation for Enterprise Contracts
Large customers may require suppliers and technology partners to demonstrate cybersecurity assurance before entering into or renewing contracts.
HITRUST certification can help organisations prepare evidence of their security practices for such customer and third-party requirements.
Who Should Consider HITRUST CSF Certification in Pune?
HITRUST CSF can be considered by organisations that manage sensitive information or operate environments where strong cybersecurity assurance is important.
This may include:
- Healthcare organisations and healthcare technology companies
- Pharmaceutical and life sciences organisations
- Software and SaaS companies
- IT and IT-enabled service providers
- Cloud service and technology providers
- Organisations handling personal or sensitive customer information
- Financial and professional service organisations
- Organisations supplying services to large enterprises
- Businesses working with international customers
- Organisations seeking a structured cybersecurity assurance programme
The right HITRUST assessment depends on the organisation’s environment, risk profile, existing controls, and assurance objectives.
What Is the HITRUST CSF Certification Process in Pune?
A structured preparation process helps an organisation understand its current security position before proceeding to the formal assessment.
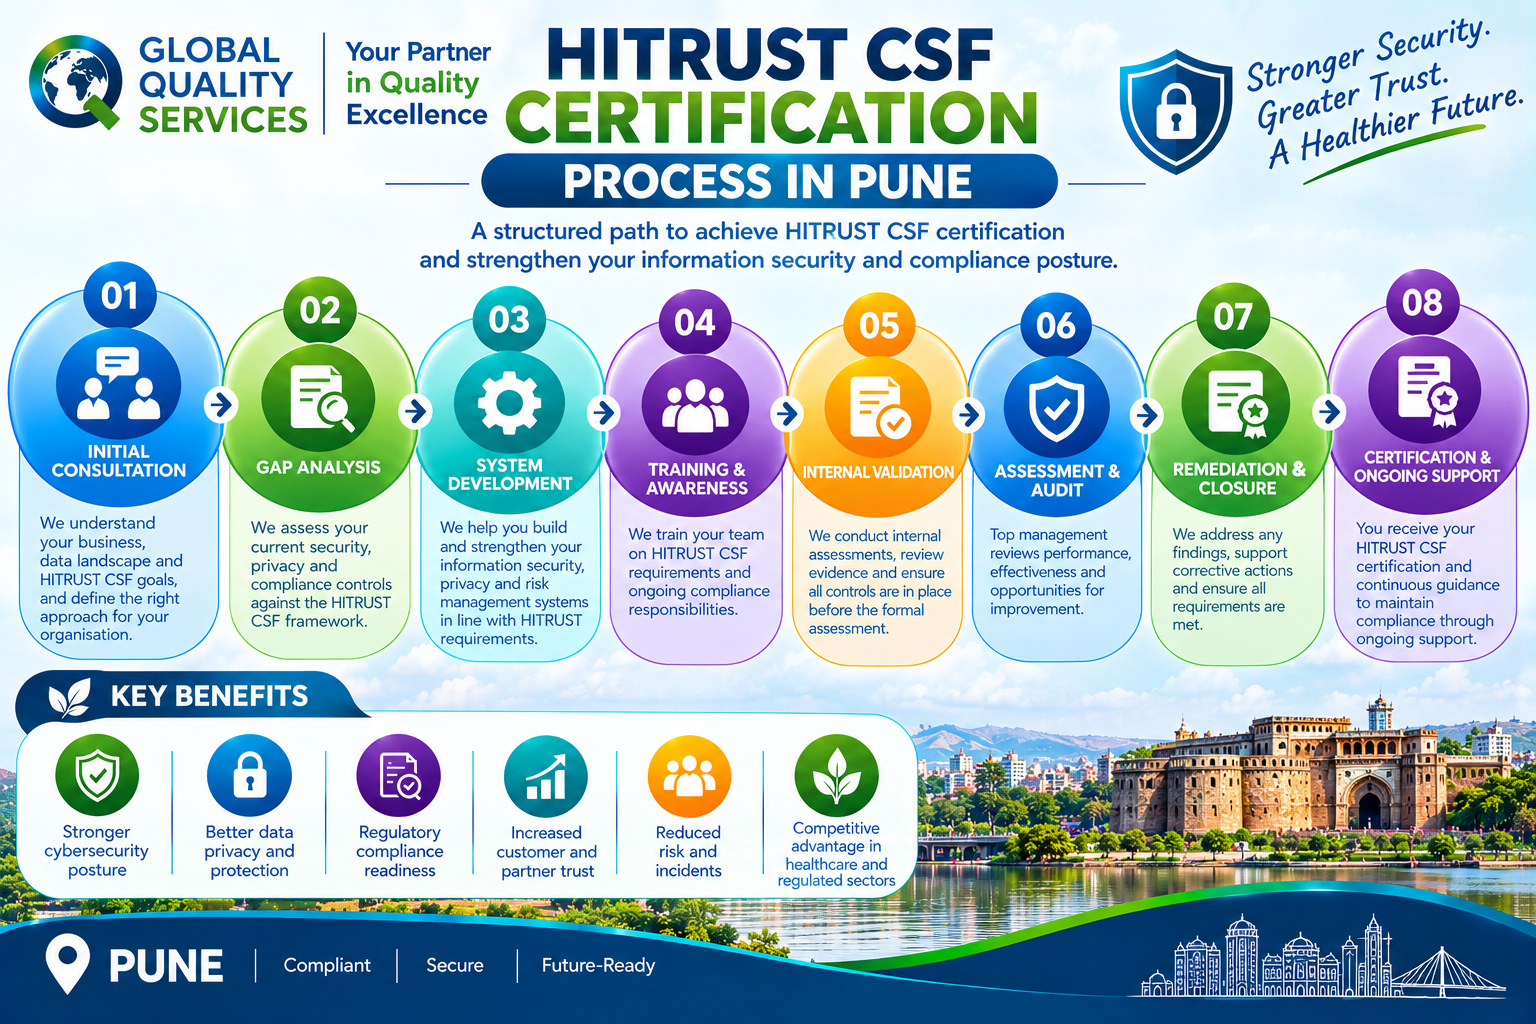
Step 1: Understand the Organisation’s Requirements
The first stage is to understand the organisation’s business activities, information systems, data types, locations, applications, cloud services, third parties, and customer requirements.
This helps determine which HITRUST assurance approach is appropriate.
Step 2: Define the Scope
The scope identifies the systems, applications, processes, locations, and business functions that will be included in the assessment.
Clearly defining scope is important because it determines which controls need to be evaluated.
Step 3: Conduct a Gap Assessment
Existing policies, procedures, technical controls, records, and evidence are reviewed against applicable HITRUST requirements.
Gaps are documented so that the organisation knows what needs to be addressed before the formal assessment.
Step 4: Strengthen Controls and Documentation
The organisation addresses identified gaps and improves its policies, procedures, technical safeguards, monitoring practices, and evidence.
Depending on the findings, this may involve improving access management, incident response, vulnerability management, risk assessment, supplier controls, business continuity, or security awareness processes.
Step 5: Prepare Assessment Evidence
Evidence must demonstrate how controls are designed, implemented, and maintained.
Examples can include policies, procedures, system configurations, audit records, risk assessments, access reviews, vulnerability reports, incident records, training records, and monitoring evidence.
Step 6: Complete the Validated Assessment
HITRUST validated assessments include testing performed by an authorised HITRUST External Assessor. The assessment process is used to evaluate the organisation’s controls against the applicable HITRUST requirements.
Step 7: Address Findings and Maintain Readiness
After the assessment, organisations should continue monitoring their controls and maintaining the required evidence.
Cybersecurity is an ongoing process, so maintaining readiness is important for future assessments, customer reviews, surveillance activities, and changing security requirements.
Which Areas of Pune Can Benefit from HITRUST CSF Certification?
HITRUST CSF support can be relevant to organisations across Pune’s major commercial and technology areas.
- Hinjawadi: A major technology and software hub with organisations operating IT, SaaS, healthcare technology, and enterprise technology environments.
- Kharadi: A prominent business and technology area with IT, software, pharmaceutical, and professional service organisations.
- Magarpatta and Hadapsar: Important business locations with technology, service, and enterprise operations.
- Viman Nagar: A commercial and technology-focused area with businesses handling digital systems and customer information.
- Baner and Balewadi: Growing business and technology locations with startups, technology companies, and professional services.
- Pimpri-Chinchwad: An important industrial and business region with manufacturing, engineering, healthcare, and technology organisations.
- Shivajinagar: A central commercial area supporting technology, professional services, education, and other business activities.
- Yerawada: A well-established business and technology location with organisations operating across different service sectors.
Healthcare and pharmaceutical organisations face particular challenges because their environments can involve sensitive patient information, research data, intellectual property, employee information, and regulated processes.
A HITRUST CSF programme can help organisations establish a structured security control environment covering areas such as access management, information protection, risk management, incident response, system security, and business continuity.
For healthcare technology providers and organisations supporting healthcare customers, a recognised cybersecurity assurance framework can also help demonstrate security practices during customer due diligence.
Pune’s pharmaceutical and healthcare technology ecosystem makes cybersecurity assurance relevant for organisations that exchange sensitive information with hospitals, healthcare providers, research organisations, customers, and technology partners.
HITRUST CSF for Pune’s IT and Technology Companies
Technology companies frequently manage cloud infrastructure, applications, databases, APIs, customer portals, remote access systems, and third-party integrations.
These environments can create complex security requirements because information may move between internal systems, cloud platforms, customers, suppliers, and external service providers.
HITRUST CSF can help technology organisations organise these security requirements into a structured control framework and establish evidence that controls are operating as intended.
This can be useful for SaaS companies, software developers, managed service providers, health-tech companies, cloud-based businesses, and organisations providing technology services to enterprise customers.
How Can HITRUST CSF Support Pune Organisations in the Future?
Cybersecurity requirements continue to change as organisations adopt cloud computing, artificial intelligence, remote work, connected systems, and increasingly complex third-party environments.
HITRUST has also continued updating its CSF and assurance programmes. For example, HITRUST CSF version 11.8.0 was released in 2026, with updated requirements for newer assessments.
Organisations that build a mature security control environment can therefore be better positioned to respond to changing customer expectations and cybersecurity requirements.
HITRUST assessments are also designed to be traversable, allowing work completed for certain assessments to support progression toward more comprehensive assurance levels.
Why Choose Global Quality Services for HITRUST CSF Certification Support in Pune?
Global Quality Services provides structured support to organisations preparing for HITRUST CSF assessment and certification.
Our approach focuses on understanding your organisation’s environment first, rather than applying a generic checklist.
We can support organisations with:
- HITRUST CSF gap assessment
- Scope and readiness support
- Security documentation review
- Control implementation guidance
- Evidence preparation
- Risk and compliance documentation
- Internal readiness assessment
- Remediation guidance
- Assessment preparation
- Support during the certification readiness journey
The objective is to help your organisation understand what is required, identify gaps early, strengthen its controls, and approach the formal assessment with better preparation.
If your organisation operates from Hinjawadi, Kharadi, Magarpatta, Hadapsar, Baner, Balewadi, Pimpri-Chinchwad, Viman Nagar, Shivajinagar, or another part of Pune, HITRUST CSF can provide a structured approach to cybersecurity assurance.
Frequently Asked Questions About HITRUST CSF Certification in Pune
1. What is HITRUST CSF Certification?
HITRUST CSF certification is a validated cybersecurity assurance process based on the HITRUST CSF framework. HITRUST currently offers e1, i1, and r2 assurance options with different levels of control requirements.
2. Is HITRUST CSF Certification suitable for IT companies in Pune?
Yes. IT, SaaS, cloud, software, and technology service companies can consider HITRUST where they need to demonstrate structured cybersecurity controls to customers, partners, or other stakeholders.
3. Is HITRUST useful for healthcare organisations in Pune?
Yes. Healthcare and healthcare technology organisations dealing with sensitive information may find HITRUST relevant because it provides a structured approach to evaluating information security controls.
4. How long is HITRUST certification valid?
The validity depends on the assurance programme. HITRUST currently lists e1 and i1 as one-year assurance options, while r2 is a two-year assurance option.
5. Can GQS issue the HITRUST certificate?
The formal HITRUST validated assessment involves an authorised HITRUST External Assessor and the HITRUST certification process. GQS can support your organisation with readiness, gap assessment, documentation, control preparation, and assessment preparation rather than representing itself as the body that issues the HITRUST certification.