Mumbai is home to banks, financial institutions, fintech companies, healthcare organizations, pharmaceutical businesses, technology companies, and large corporate groups that routinely handle sensitive information. For these organizations, cybersecurity is not limited to protecting internal systems. It also affects customer trust, vendor relationships, contractual requirements, and the ability to work with larger enterprises.
HITRUST CSF Certification in Mumbai gives organizations a structured way to evaluate their security controls, identify weaknesses, improve their information security practices, and demonstrate that their cybersecurity environment has been independently assessed against the applicable HITRUST requirements.
Global Quality Services helps Mumbai-based organizations prepare for HITRUST CSF assessments through gap assessment, control review, documentation support, remediation guidance, and certification readiness.
What Does HITRUST CSF Certification Mean?
HITRUST CSF is a cybersecurity and assurance framework that brings together requirements from numerous authoritative sources, standards, regulations, and best practices. HITRUST’s 2026 Trust Report states that CSF v11.7 included 72 authoritative sources.
Rather than asking an organization to manage every security requirement separately, HITRUST provides a structured control environment that can be assessed according to the organization’s risk profile and assurance needs.
HITRUST currently provides different assurance pathways, including:
- e1, which provides foundational cybersecurity assurance.
- i1, which provides a higher level of threat-adaptive cybersecurity assurance.
- r2, which provides a more comprehensive and tailored risk-based assessment.
The appropriate option depends on the organization’s systems, information, risks, customer expectations, and business requirements.
Why Are Mumbai Businesses Looking at HITRUST CSF?
Mumbai organizations often operate in environments where information moves between customers, employees, cloud platforms, vendors, applications, and external service providers.
This is particularly relevant for financial services and fintech organizations, where customer and transaction information must be protected across highly connected environments. It also matters to healthcare and pharmaceutical companies that manage patient information, research data, intellectual property, and other sensitive records.
For technology companies, the challenge may be different. A SaaS provider or software company may need to demonstrate that its own platform and supporting infrastructure can protect customer information.
HITRUST CSF gives these organizations a common framework for examining how security controls are designed, implemented, monitored, and maintained.
What Can HITRUST CSF Help a Mumbai Organization Improve?
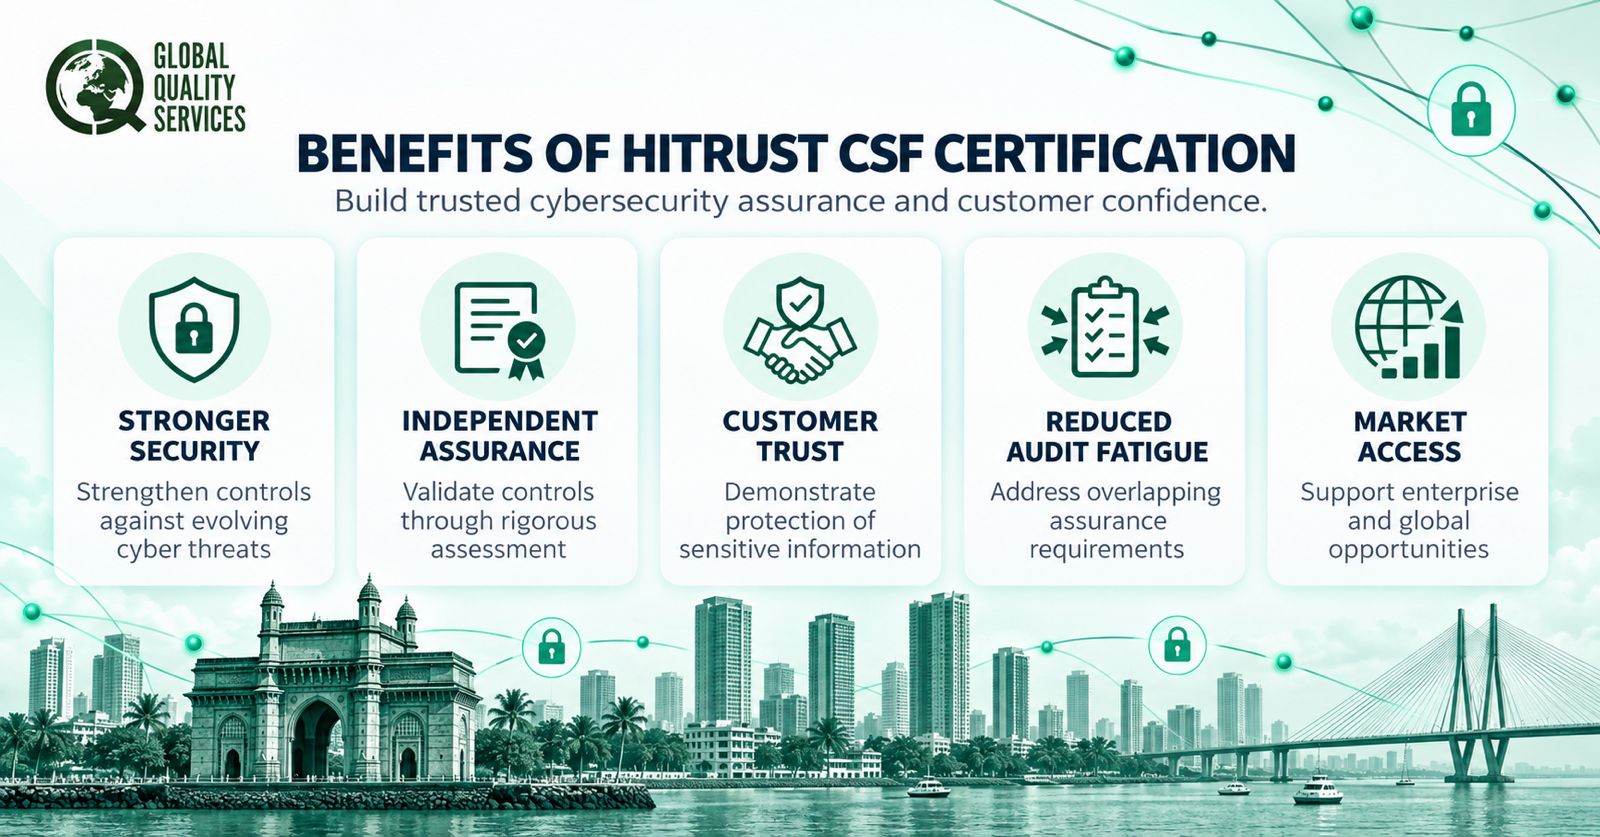
The value of HITRUST is not simply having another certificate on a company profile. The assessment process can expose weaknesses that may otherwise remain hidden between different departments and technology systems.
Clearer Security Ownership
Security controls often involve several teams. IT may manage infrastructure, HR may manage employee access processes, procurement may manage suppliers, and business teams may own applications or data.
A structured assessment helps establish who is responsible for applicable controls and what evidence needs to be maintained.
Better Evidence Management
Organizations may have good security practices but struggle to demonstrate them consistently.
HITRUST preparation brings attention to the evidence needed to show that controls are actually operating. This can include access reviews, vulnerability management records, risk assessments, policies, incident records, security awareness records, and monitoring information.
Stronger Third-Party Risk Management
Mumbai’s large enterprise ecosystem means many organizations depend on vendors, technology providers, cloud services, and outsourced operations.
A mature security program should therefore consider not only internal controls but also the risks created by external parties.
HITRUST can help organizations establish a more structured approach to these requirements.
Greater Readiness for Customer Security Reviews
Large customers may conduct detailed security assessments before onboarding a supplier.
Organizations with a documented and independently assessed control environment may be better prepared to respond to these reviews because their security practices and supporting evidence are already organized.
Which Mumbai Industries Can Benefit From HITRUST CSF?
HITRUST is not restricted to one type of organization. Its relevance depends more on the sensitivity of information, security risks, customer requirements, and the assurance an organization needs.
Banking, Financial Services and Fintech
Mumbai’s financial ecosystem creates a strong need for disciplined information security.
Banks, fintech companies, payment technology providers, financial software companies, insurance technology businesses, and other service providers may manage financial information, identity information, transaction data, and customer records.
For these organizations, HITRUST can form part of a broader security assurance program alongside applicable financial-sector requirements.
Healthcare and Health Technology
Healthcare organizations and health-tech companies may process patient information through clinical systems, applications, portals, cloud environments, and connected services.
HITRUST can help organizations examine controls around access, data protection, security monitoring, incident response, risk management, and continuity.
Pharmaceutical and Life Sciences
Pharmaceutical organizations may need to protect much more than employee and customer information.
Research data, intellectual property, clinical information, manufacturing systems, supplier information, and corporate systems can all require protection.
A structured cybersecurity framework can help bring these different security considerations into a more consistent control environment.
Technology and SaaS
Mumbai has a large technology and enterprise services ecosystem. Software companies may provide applications and platforms that store or process customer information on behalf of other organizations.
For these businesses, cybersecurity assurance can become an important part of enterprise sales and vendor due diligence.
How Does HITRUST CSF Certification Preparation Work in Mumbai?
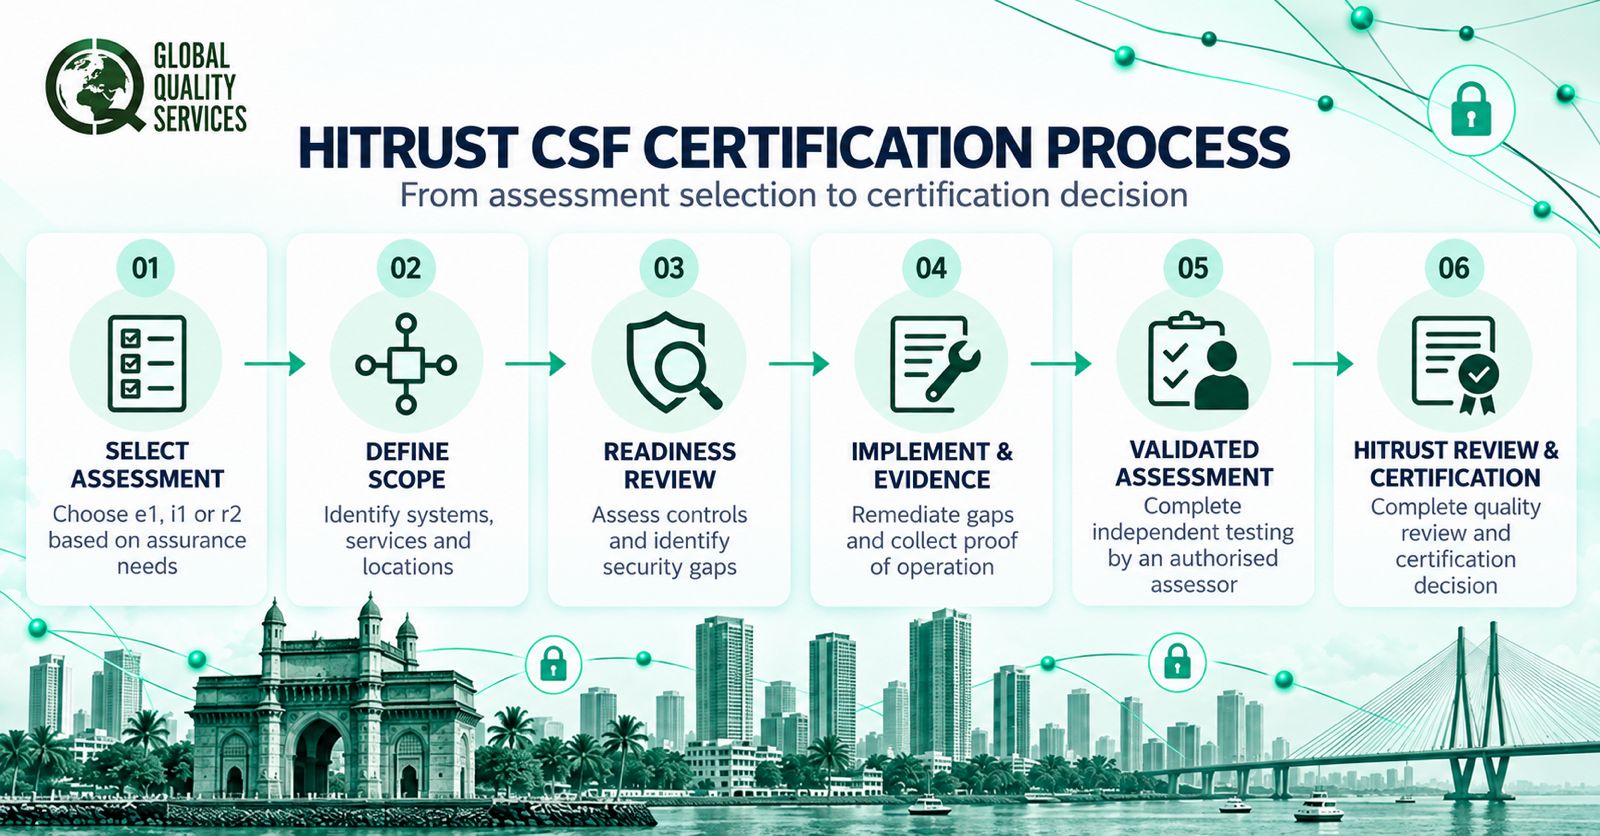
Preparation should begin with the organization’s actual environment rather than with a generic checklist.
1. Understand the Business and Technology Environment
The first stage is to understand what the organization does, what information it handles, where that information resides, and which systems are involved.
This may include cloud platforms, business applications, databases, endpoints, networks, remote access systems, third-party services, and customer-facing applications.
2. Establish the Assessment Boundary
The organization then determines which systems, processes, business units, locations, and information assets are included in the assessment.
This is especially important for large Mumbai organizations operating across multiple offices, business divisions, or technology environments.
3. Map Existing Controls
Existing policies, procedures, technologies, and operational practices are compared with the applicable HITRUST requirements.
This identifies what the organization already does well and where additional work may be necessary.
4. Identify and Prioritize Gaps
Not every gap has the same business impact.
Organizations should understand which weaknesses affect critical systems, sensitive information, regulatory obligations, customer commitments, or important business processes.
The findings can then be prioritized for remediation.
5. Strengthen Controls
Depending on the findings, improvements may involve identity management, access reviews, vulnerability management, incident response, security awareness, encryption, logging, risk management, supplier controls, business continuity, or other applicable areas.
6. Build an Evidence Trail
The organization needs more than written policies. It should be able to demonstrate that applicable controls are actually operating.
Evidence is therefore collected and organized before the formal assessment.
7. Prepare for the Validated Assessment
The formal HITRUST validated assessment involves an authorized HITRUST External Assessor. HITRUST maintains a directory of External Assessors that are approved to perform validated assessments.
GQS can support the organization before this stage by helping identify gaps, organize documentation, prepare evidence, and improve readiness.
8. Maintain the Control Environment
Certification should not be treated as the end of the security program.
Organizations need to continue monitoring controls, managing risks, maintaining evidence, addressing vulnerabilities, and preparing for future assessment requirements.
Where in Mumbai Can Organizations Seek HITRUST CSF Support?
HITRUST requirements can apply across Mumbai’s business ecosystem rather than being limited to one commercial district.
- Bandra-Kurla Complex: A major corporate and financial district where organizations across financial services, consulting, technology, and enterprise services operate.
- Andheri East: A significant business and technology corridor with IT, pharmaceutical, professional service, and other corporate organizations.
- Powai: Known for its technology and corporate ecosystem, making it relevant for software, SaaS, digital services, and enterprise technology organizations.
- Lower Parel: A major corporate and commercial district with financial, professional, media, and technology businesses.
- Goregaon: A growing business area with organizations across technology, financial services, healthcare, and professional services.
- Malad: A significant commercial location with technology, service, and healthcare-related businesses.
- Navi Mumbai: An important part of the wider Mumbai business region, with technology, pharmaceutical, logistics, financial, and industrial organizations.
- Thane: A major commercial and technology location within the Mumbai metropolitan region, with a growing base of corporate and service organizations.
What Government and Regulatory Requirements Should Mumbai Organizations Consider?
HITRUST certification does not replace Indian legal, regulatory, or contractual requirements.
An organization preparing for HITRUST should also identify the requirements that apply to its particular industry and information environment.
For cybersecurity-related requirements, organizations can review official guidance and directions from the Ministry of Electronics and Information Technology (MeitY) and CERT-In.
Organizations operating in regulated financial services should also consider applicable requirements issued by the Reserve Bank of India (RBI), Securities and Exchange Board of India (SEBI), and other relevant authorities, depending on their business activities.
Healthcare organizations should review applicable requirements and guidance from the Ministry of Health and Family Welfare and other relevant health authorities.
These bodies do not administer HITRUST certification. Their requirements are separate and may need to be addressed alongside the organization’s HITRUST program.
What Should a Mumbai Organization Have Before Starting HITRUST Preparation?
Organizations often benefit from having several basic elements in place before beginning a formal HITRUST assessment.
These can include:
- Defined information security responsibilities
- Documented security policies and procedures
- Risk assessment processes
- Access management controls
- Vulnerability management
- Incident response procedures
- Business continuity arrangements
- Employee security awareness
- Vendor and third-party risk management
- Security monitoring and evidence collection
The exact requirements will depend on the applicable HITRUST assessment and the organization’s environment.
How Can HITRUST CSF Support Long-Term Cybersecurity Maturity?
Cybersecurity requirements continue to change as organizations adopt cloud services, artificial intelligence, remote access, connected technologies, and increasingly complex vendor ecosystems.
HITRUST also continues to evolve its CSF and assurance programs. Its 2026 Trust Report notes the expansion of authoritative sources within the framework, reflecting the broader range of security standards and requirements organizations need to consider.
For a Mumbai organization, this makes continuous security management more useful than treating certification as a one-time compliance project.
A well-maintained control environment can help the organization respond to customer questionnaires, security reviews, new technology risks, internal audits, and future assurance requirements.
Why Choose Global Quality Services for HITRUST CSF Support in Mumbai?
Global Quality Services helps organizations prepare for HITRUST CSF assessments through a practical, organization-specific approach.
Instead of starting with documentation alone, the process considers the organization’s business model, technology environment, information assets, existing controls, and assessment objectives.
Whether your organization operates in BKC, Andheri, Powai, Lower Parel, Goregaon, Malad, Thane, Navi Mumbai, or another part of the Mumbai metropolitan region, HITRUST CSF can provide a structured approach to cybersecurity assurance.
If your customers are asking for stronger security assurance, your organization is entering regulated or enterprise markets, or you simply want a more structured approach to information security, HITRUST preparation can help you understand where your controls stand today.
Contact Global Quality Services to discuss your HITRUST CSF Certification requirements in Mumbai.
Frequently Asked Questions About HITRUST CSF Certification in Mumbai
1. What is HITRUST CSF Certification?
HITRUST CSF certification is a validated cybersecurity assurance process based on the HITRUST CSF. The framework brings together requirements from multiple authoritative sources and provides different assurance options based on organizational needs.
2. Is HITRUST CSF useful for Mumbai fintech and financial technology companies?
It can be. Fintech companies and technology providers that handle sensitive financial or customer information may use HITRUST as part of their broader cybersecurity assurance strategy, subject to their specific customer and regulatory requirements.
3. Can a healthcare technology company in Mumbai pursue HITRUST?
Yes. Healthcare technology organizations can consider HITRUST when they need a structured way to assess controls protecting sensitive information and demonstrate security assurance to customers and business partners.
4. Does HITRUST replace ISO 27001 or other security standards?
No. HITRUST is a separate assurance framework. It incorporates requirements and concepts from multiple authoritative sources, but organizations should determine which standards, regulations, and contractual requirements apply to their own environment.
5. Does GQS issue the HITRUST certification?
GQS provides preparation and readiness support. The formal validated assessment is performed through the HITRUST assessment process involving an authorized HITRUST External Assessor. GQS should therefore not be described as the independent issuer of a HITRUST certificate.