Healthcare in India has evolved to embrace digital health records, hospital connectivity, telehealth services, and health tech platforms. The need for robust data security measures has never been greater as a result. By July 20, 2026, 94.87 crore ABHA IDs were generated under the Ayushman Bharat Digital Mission, and 5.36 lakh health facilities were enrolled in the Health Facility Registry.
The increasing reliance on this ecosystem places hospitals, labs, insurance firms, health tech firms, and other healthcare stakeholders in the position of needing to adopt systematic controls over the protection of sensitive data assets. This is where HITRUST CSF Certification comes into play.
HITRUST CSF offers an established methodology for managing information security, privacy, risk, and compliance via a controlled environment. HITRUST CSF Certification could benefit many healthcare entities dealing with patient records, insurance claims, clinical data, or health applications in India.
What is HITRUST CSF Certification
HITRUST CSF unifies global security standards into one auditable framework, simplifying compliance while improving enterprise-wide information risk management maturity.
HITRUST CSF is a comprehensive, certifiable framework developed by HITRUST Alliance. It integrates requirements from ISO 27001, NIST, HIPAA, PCI DSS, GDPR, and other regulations into a single, scalable framework.
For Indian organizations, this means reduced audit fatigue, consistent security controls, and a structured approach to managing sensitive data, including personal health information (PHI) and personally identifiable information (PII).
Why HITRUST CSF Certification is Important for Indian Businesses
Indian organizations face rising regulatory pressure, making HITRUST essential for managing compliance, data protection, and third-party risk effectively.
Regulatory Alignment in India
HITRUST CSF aligns well with Indian regulatory expectations, including data protection, IT governance, and sector-specific compliance needs. It supports organizations preparing for evolving privacy and cybersecurity regulations while maintaining global readiness.
Enhanced Trust and Market Credibility
Certification signals a high level of security maturity. It reassures clients, investors, and international partners that your organization follows globally recognized best practices.
Reduced Compliance Complexity
Instead of managing multiple frameworks separately, HITRUST allows Indian businesses to adopt one unified control structure, saving time, cost, and operational effort. Another option that organizations could pursue to enhance information security management alongside their HITRUST CSF program would be the ISO/IEC 27001 Certification.
Who Needs HITRUST CSF Certification in India?
HITRUST CSF Certification is most relevant for organizations that handle sensitive data, provide technology services, or work with highly regulated sectors:
- Healthcare and Hospitals
- HealthTech and Digital Health
- Pharmaceutical and Life Sciences
- Health Insurance
- Banking and Financial Services
- FinTech
- IT and ITES
- SaaS and Cloud Service Providers
- BPO and KPO
- Medical Device Companies
- Government and Public Sector
- E-commerce and Retail
Types of HITRUST CSF Assessments
HITRUST offers multiple assessment levels, allowing organizations to choose certification based on risk exposure, regulatory needs, and business goals.
Phase 1 – E1 Assessment
The E1 assessment suits low-risk organizations seeking foundational cybersecurity assurance. It validates essential security controls, establishes baseline hygiene, and helps organizations demonstrate basic compliance readiness without complex or resource-intensive assessment requirements.
Phase 2 – I1 Assessment
The I1 assessment supports moderate-risk organizations that require stronger assurance. It uses standardized controls to evaluate security maturity, reduces assessment complexity, and enables faster certification while meeting common regulatory and client security expectations.
Phase 3 – R2 Assessment
The R2 assessment is ideal for high-risk organizations handling sensitive or regulated data. It delivers the highest level of assurance through comprehensive control evaluation, detailed testing, and rigorous validation aligned with complex compliance demands.
HITRUST CSF Certification Process in India
A structured certification process ensures consistent control implementation, accurate risk evaluation, and successful validation by authorized HITRUST assessors. Here is a clear process:
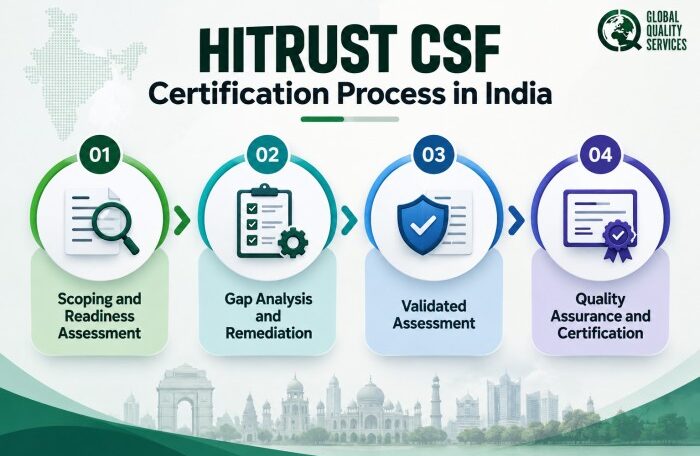
Step 1: Scoping and Readiness Assessment
We define the assessment scope by analyzing your organization’s size, industry, data types, and regulatory exposure, ensuring the right HITRUST controls apply accurately from the beginning.
Step 2: Gap Analysis and Remediation
Our experts evaluate your current security controls, identify compliance gaps, and provide clear, practical remediation guidance aligned with HITRUST CSF requirements and operational realities.
Step 3: Validated Assessment
An authorized HITRUST assessor conducts a thorough assessment, validating control design and testing operational effectiveness to confirm your organization meets certification requirements.
Step 4: Quality Assurance and Certification
HITRUST reviews the assessment through strict quality assurance checks and, once approved, issues the official certification confirming your compliance and security maturity.
Industries That Benefit from HITRUST CSF Certification in India
HITRUST CSF supports industries managing sensitive data, complex regulations, and high third-party security expectations across global markets.
Healthcare and Life Sciences
Hospitals, diagnostic centers, and digital health platforms use HITRUST CSF to protect sensitive patient data, strengthen privacy controls, and align with global healthcare regulations, including international data protection and information security expectations.
IT, SaaS, and Cloud Service Providers
IT companies, SaaS providers, and cloud service organizations implement HITRUST CSF to demonstrate strong security governance, manage third-party risks, and meet enterprise and global client compliance requirements with confidence.
BFSI and FinTech
Banks, NBFCs, and FinTech companies adopt HITRUST CSF to enhance risk management, safeguard financial and personal data, and meet stringent regulatory, cybersecurity, and customer trust requirements.
Outsourcing and BPO Organizations
BPOs and outsourcing firms handling international client data rely on HITRUST CSF to strengthen information security, ensure cross-border compliance, and build long-term trust with global clients and partners.
Benefits of HITRUST CSF Certification for Your Organization
HITRUST CSF delivers measurable security improvements, stronger governance, and competitive differentiation in regulated and international markets.
Key Advantages
- Strengthened information security posture
- Improved regulatory and contractual compliance
- Increased customer and stakeholder trust
- Reduced audit duplication and long-term compliance costs
- Better third-party risk management
HITRUST Certification Cost in India
HITRUST Certification costs vary widely across Indian firms. There is no flat rate because the fees depend on several factors, including the size of the company, the number of systems and datasets involved, and the extent of the audit itself. Additional costs can include any gap assessments, documentation preparation, employee training, or implementation assistance prior to the audit.
Smaller organizations may pay less compared to bigger firms that operate from multiple sites and handle vast amounts of data. Defining the certification scope and requirements accurately will give you the most accurate quote.
Why Choose Global Quality Services for HITRUST CSF Certification in India
Global Quality Services has emerged as a respected consultant for HITRUST CSF Certification within India. It assists companies in comprehending the certification requirements, documenting themselves accordingly, correcting any areas of non-compliance, and preparing for the audit process without disrupting business-as-usual operations. Here are key reasons why choose us:
Our Expertise
We bring together deep technical knowledge, strong regulatory insight, and practical implementation experience. Our team actively works with Indian organizations to design, implement, and strengthen HITRUST-aligned controls that fit real business operations, not just documentation requirements.
End-to-End Support
We manage your entire HITRUST CSF certification journey, from initial readiness and gap analysis to remediation, validated assessment, and final certification. Our structured approach reduces internal effort, avoids delays, and ensures complete transparency at every stage.
Local and Global Perspective
We understand Indian compliance challenges, data protection expectations, and industry practices. At the same time, we align your security framework with global standards, enabling you to meet international client, partner, and regulatory expectations with confidence.
Partner with Global Quality Services for HITRUST CSF Certification in India
Partner with Global Quality Services for HITRUST CSF Certification in India and achieve compliance with confidence. Our experts deliver structured guidance, practical implementation support, and faster certification with minimal operational disruption. With over 26 years of experience, we help you meet global security expectations while addressing Indian regulatory requirements effectively. Contact us to make your certification journey smooth and reliable.