Mumbai businesses increasingly handle sensitive customer, financial, and operational data, making cybersecurity a growing business priority. In 2026, the average cost of a data breach in India reached ₹25.5 crore, according to an IBM report covered by The Economic Times.
A CyberVadis Cybersecurity Assessment in Mumbai helps organisations evaluate their security practices, identify gaps, and demonstrate cybersecurity maturity. With experienced consultants, businesses can prepare evidence, address weaknesses, and navigate the assessment more effectively.
What is a CyberVadis Cybersecurity Assessment
CyberVadis is a cybersecurity assessment that evaluates an organisation’s information security practices and overall cybersecurity maturity. It uses a structured questionnaire and supporting evidence to assess how effectively a company manages security risks.
The assessment covers four major areas:
- Identify: Asset management, risk assessment, data classification, and security governance.
- Protect: Access control, encryption, network security, endpoint protection, and security awareness.
- Detect: Security monitoring, logging, anomaly detection, and vulnerability management.
- React: Incident response, business continuity, recovery, and communication procedures.
CyberVadis maps its methodology to recognised approaches such as ISO 27001, NIST Cybersecurity Framework, GDPR, NIS2, and DORA. CyberVadis Help Center
Why CyberVadis Assessment Matters for Mumbai Businesses
Mumbai has a diverse business ecosystem that includes financial services, IT companies, startups, manufacturing businesses, logistics providers, healthcare organisations, and professional services firms. Many of these businesses exchange sensitive information with customers, suppliers, and international partners.
A cybersecurity assessment can help organisations:
- Understand their current cybersecurity maturity.
- Identify weaknesses across security controls.
- Organise cybersecurity documentation and evidence.
- Demonstrate security practices to customers and business partners.
- Prioritise areas that need improvement.
- Strengthen internal information security processes.
- Prepare for customer or supplier security assessments.
For companies in Bandra Kurla Complex, Andheri, Powai, Lower Parel, Navi Mumbai, and other commercial areas, a structured cybersecurity assessment can support stronger security governance as the organisation grows.
What Does CyberVadis Assess
CyberVadis does more than check whether your company has cybersecurity policies. It looks at how those practices operate in real business situations.
The assessment considers three evidence levels:
1. Definition
Your organisation should have clearly defined security policies, procedures, or processes covering applicable controls.
2. Implementation
You need to demonstrate that your organisation actually follows those security practices rather than simply maintaining documents.
3. Monitoring
Your evidence should show that the organisation reviews, monitors, and maintains its security controls over time.
This approach makes the CyberVadis assessment in Mumbai useful for companies that want a clearer picture of how their cybersecurity practices work in day-to-day operations.
CyberVadis Cybersecurity Assessment Process in Mumbai
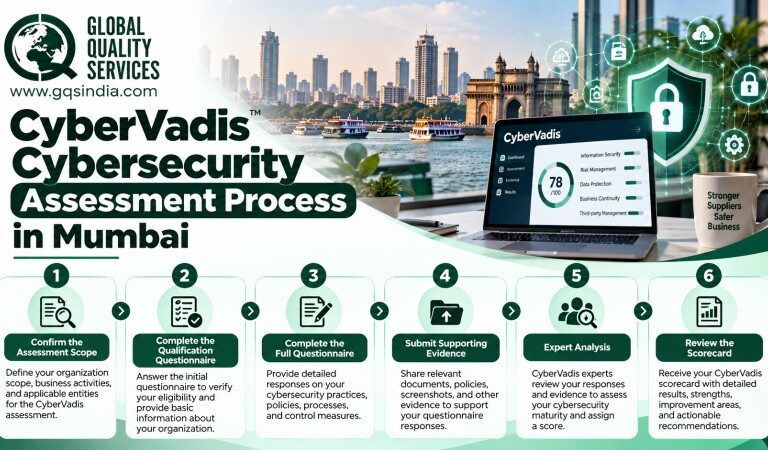
Understanding the process beforehand can help Mumbai businesses prepare their teams and documentation.
Step 1: Confirm the Assessment Scope
First, confirm which legal entity falls within the assessment scope. CyberVadis evaluates the defined legal entity rather than automatically assessing only the systems connected to a particular customer relationship.
Step 2: Complete the Qualification Questionnaire
The organisation provides initial information about its business and cybersecurity practices. CyberVadis uses this information to determine the relevant assessment questions.
Step 3: Complete the Full Questionnaire
The company answers detailed cybersecurity questions and attaches supporting evidence to the relevant controls. CyberVadis states that a typical full questionnaire can take around two to three days when documentation is ready.
Step 4: Submit Supporting Evidence
Evidence plays a central role in the CyberVadis assessment. Organisations should connect each document to the relevant answer because an uploaded document that is not attached to a question may not receive credit.
Step 5: Expert Analysis
CyberVadis analysts review the questionnaire and evidence before preparing the assessment results. The published process indicates that expert analysis typically takes around four to six weeks.
Step 6: Review the Scorecard
The final scorecard shows the organisation’s overall cybersecurity score, individual function scores, strengths, and areas requiring attention. CyberVadis calculates the overall score using a weighted model rather than a simple average.
Documents Required for CyberVadis Assessment
Mumbai businesses should organise relevant cybersecurity evidence before beginning the questionnaire. Depending on the organisation, this may include:
- Information security policies
- Risk assessment records
- Asset inventories
- Access control procedures
- User access reviews
- Incident response procedures
- Business continuity plans
- Vulnerability assessment reports
- Security awareness records
- Encryption procedures
- Backup records
- Network security documentation
- Endpoint security records
- Supplier security assessments
- Data protection procedures
- Monitoring and review records
The exact evidence depends on the applicable controls and the organisation’s assessment scope. CyberVadis can also accept alternative evidence where formal policies do not yet exist, provided the evidence demonstrates relevant cybersecurity practices.
Common CyberVadis Assessment Challenges in Mumbai
Many businesses understand cybersecurity but struggle to present their practices clearly during an assessment. Common challenges include:
- Incomplete documentation: Teams may have effective security practices but lack formal records to demonstrate them.
- Poor evidence mapping: Companies may upload documents without linking them to the specific questionnaire controls.
- Inconsistent implementation: A policy may exist, but employees may not consistently follow it.
- Limited monitoring records: Organisations may implement controls but lack evidence showing regular reviews.
- Unclear assessment scope: An incorrect legal-entity scope can lead to irrelevant questions and an inaccurate representation of the company’s security posture.
How a CyberVadis Consultant Can Help in Mumbai
A CyberVadis consultant can support your team before and during the assessment. The consultant can review existing cybersecurity practices, identify documentation gaps, map evidence to relevant controls, and help teams understand assessment questions.
For Mumbai organisations working with overseas customers or enterprise supply chains, this preparation can also make customer security reviews easier to manage.
A consultant can help with:
- CyberVadis readiness assessment
- Gap identification
- Evidence preparation
- Policy and procedure review
- Control mapping
- Questionnaire support
- Cybersecurity documentation
- Corrective action planning
- Scorecard improvement planning
The goal should not be to create documents only for the assessment. Your organisation should build security practices that employees can actually follow and maintain.
CyberVadis Assessment vs ISO 27001
CyberVadis and ISO 27001 address information security from different perspectives. CyberVadis assesses cybersecurity maturity through its questionnaire, evidence review, and scoring methodology. ISO 27001 focuses on establishing and maintaining an Information Security Management System that meets the standard’s requirements.
CyberVadis itself maps its methodology to ISO 27001, among other recognised frameworks and regulations.
A company can therefore use its existing ISO 27001 practices and documentation as useful supporting material, where applicable, while still responding specifically to the CyberVadis questionnaire.
Why Choose Global Quality Services for CyberVadis Assessment in Mumbai?
Global Quality Services can help Mumbai businesses prepare for CyberVadis with practical, structured support. We can review your cybersecurity practices, identify documentation gaps, organise supporting evidence, and guide your team through the assessment requirements.
Whether you operate from BKC, Andheri, Powai, Navi Mumbai, Thane, or another Mumbai business hub, we can help you prepare better and document more clearly. Contact Global Quality Services for smooth, reliable service.
Frequently Asked Questions
1. What is a CyberVadis cybersecurity assessment in Mumbai?
A CyberVadis cybersecurity assessment evaluates a Mumbai company’s security maturity across Identify, Protect, Detect, and React using questionnaires, evidence, and expert analysis.
2. How long does a CyberVadis assessment take?
The full questionnaire typically takes two to three days when documentation is ready, while CyberVadis expert analysis generally takes four to six weeks.
3. What evidence is required for CyberVadis?
CyberVadis requires evidence supporting questionnaire answers. Organisations can submit policies, procedures, records, reports, and other documentation that demonstrates implemented and monitored cybersecurity practices.
4. Can an ISO 27001-certified company complete CyberVadis?
Yes. CyberVadis maps its methodology to ISO 27001, so relevant ISO 27001 policies, records, and controls may support the assessment where they address applicable requirements.
5. Why hire a CyberVadis consultant in Mumbai?
A consultant can help review cybersecurity gaps, organise evidence, map documents to controls, clarify questionnaire requirements, and prepare your team for the assessment process.