Ahmedabad’s growing digital economy has made cybersecurity a key business priority. The Times of India reported that the city recorded ₹134.45 crore in cyber fraud losses between February 2024 and January 2026. This growing risk makes it important for businesses to demonstrate strong cybersecurity practices to customers and partners.
A CyberVadis cybersecurity assessment in Ahmedabad helps organisations evaluate their security maturity and identify gaps. However, preparing evidence and answering assessment questions correctly can be challenging. Hiring an experienced CyberVadis consultant helps businesses prepare accurately, address gaps, and approach the assessment with confidence.
What is a CyberVadis Cybersecurity Assessment
CyberVadis is a cybersecurity assessment designed to evaluate an organisation’s cyber risk management and security maturity. The assessment uses a tailored questionnaire based on factors such as the organisation’s size, sector, and cybersecurity practices.
Unlike a simple compliance checklist, CyberVadis evaluates whether security practices exist, operate in practice, and remain actively monitored. Its methodology maps to recognised references and requirements, including ISO 27001, NIST Cybersecurity Framework, GDPR, NIS2, and DORA.
The assessment produces a scorecard that shows your organisation’s overall cybersecurity performance, along with separate results across the four assessment functions.
Why CyberVadis Assessment Matters for Ahmedabad Businesses
Businesses in Ahmedabad increasingly work with customers, suppliers, manufacturers, technology providers, and international organisations. These relationships often involve sharing sensitive information or granting access to business systems.
A customer may therefore ask questions such as:
- How do you protect customer information?
- Do you control employee access to systems?
- How do you detect cybersecurity incidents?
- Do you regularly assess vulnerabilities?
- Can you respond effectively to a security incident?
- Do you maintain business continuity procedures?
- Can you demonstrate your security controls with evidence?
A CyberVadis assessment gives organisations a structured way to demonstrate how they manage these areas.
It can be particularly relevant for IT companies, SaaS providers, manufacturers, BPOs, financial service providers, healthcare organisations, logistics companies, exporters, and businesses handling customer or supplier data.
What Does CyberVadis Assess?
CyberVadis organises its assessment around four core cybersecurity functions.
1. Identify
The Identify function examines whether your organisation understands its assets, risks, data, and security responsibilities.
This area can include:
- Asset management
- Risk assessment
- Data classification
- Security governance
- Security roles and responsibilities
- Cybersecurity policies
- Risk registers
A business needs to know what it owns and what it needs to protect before it can manage cybersecurity effectively.
2. Protect
The Protect function focuses on the controls your organisation uses to prevent or reduce cybersecurity risks.
Typical areas include:
- Access management
- Authentication
- Encryption
- Network security
- Endpoint protection
- Security awareness
- Data protection
- Security policies and procedures
For example, having a password policy alone may not demonstrate that your organisation actively enforces password security.
3. Detect
The Detect function examines how your organisation identifies suspicious activity, vulnerabilities, and potential security incidents.
This can involve:
- Security monitoring
- Logging
- Vulnerability management
- Incident detection
- Anomaly detection
- Security testing
- Monitoring procedures
Regular monitoring helps organisations identify problems before they develop into larger security incidents.
4. React
The React function focuses on your organisation’s ability to respond when a cybersecurity incident occurs.
This area may cover:
- Incident response plans
- Business continuity
- Disaster recovery
- Incident communication
- Response responsibilities
- Post-incident reviews
- Recovery procedures
A documented incident response plan becomes much more useful when employees understand their responsibilities and the organisation regularly reviews the process.
How Does the CyberVadis Assessment Process Work?
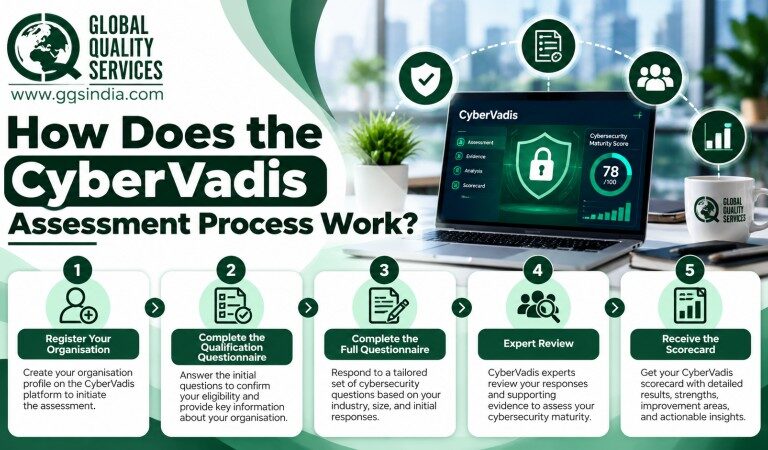
The CyberVadis assessment follows a structured process from registration through final results. The current process includes registration, qualification, the full questionnaire, expert analysis, and results.
Step 1: Register Your Organisation
The process begins with company registration on the CyberVadis platform. Registration typically takes around five minutes and requires basic company information and contact details.
Step 2: Complete the Qualification Questionnaire
The qualification questionnaire asks initial questions about your organisation and its cybersecurity practices.
Your answers determine which questions appear in the full assessment. This means businesses should answer this stage carefully rather than treating it as a basic formality.
Step 3: Complete the Full Questionnaire
After qualification, your organisation receives a questionnaire tailored to its specific context.
You need to select applicable controls, answer the questions, and attach supporting evidence. CyberVadis states that the full questionnaire can typically take around two to three days when the required documentation is already prepared.
Step 4: Expert Review
After submission, CyberVadis analysts review the questionnaire and supporting evidence.
The review checks whether your declared controls are credible and supported by documentation. The analysis generally takes several weeks, with CyberVadis currently stating approximately 3–6 weeks for the expert analysis process.
Step 5: Receive the Scorecard
Once the assessment is complete, your organisation receives a scorecard showing its cybersecurity performance.
The results include an overall score, function-level scores, topic-level strengths and risk areas, and an improvement plan.
What Evidence Do You Need for CyberVadis?
Evidence plays a major role in the CyberVadis assessment. Simply claiming that a security control exists does not demonstrate that your organisation actually operates it.
CyberVadis evaluates evidence across three levels:
Definition: Documentation showing that a security practice formally exists.
Implementation: Evidence demonstrating that employees and systems actually follow the practice.
Monitoring: Records showing that the organisation regularly reviews and maintains the control.
For example, if your organisation claims to have strong access controls, you could need a relevant access control policy, system configuration evidence, and records showing periodic access reviews.
Common evidence can include:
- Information security policies
- Risk assessments
- Risk treatment plans
- Access control records
- Vulnerability assessment reports
- Security awareness training records
- Incident response procedures
- Business continuity plans
- Disaster recovery documentation
- Audit reports
- ISO 27001 certificates
- SOC 2 reports
- Technical configuration screenshots
CyberVadis also notes that evidence should be attached to the relevant question. Uploading a document without linking it to the applicable response may not allow analysts to credit that evidence.
Common Challenges Businesses Face During CyberVadis Assessment
Many organisations have cybersecurity controls in place but struggle to demonstrate them properly during an assessment.
Scattered Documentation
Security evidence may sit across IT, HR, compliance, legal, and management teams. Finding the right document for each question can take significant time.
Outdated Policies
A company may have a security policy, but the document may not reflect its current systems, responsibilities, or processes.
Weak Implementation Evidence
A written policy does not always demonstrate that employees follow the required procedure.
Missing Monitoring Records
Organisations sometimes document a control but lack evidence showing that they review or monitor it regularly.
Incorrect Control Selection
Selecting an applicable control without providing relevant evidence can affect the assessment outcome. CyberVadis recommends addressing every control that genuinely applies to the organisation.
How to Prepare for CyberVadis Assessment in Ahmedabad
Preparation can make the assessment considerably easier. Before beginning the questionnaire, Ahmedabad businesses should:
- Define the assessment scope
Identify the legal entity and business operations covered by the assessment. - Create an evidence inventory
List existing policies, procedures, reports, records, certificates, and technical evidence. - Review cybersecurity policies
Check whether your policies reflect your current systems and business processes. - Map controls to evidence
Connect each security practice with documents that demonstrate its definition, implementation, and monitoring. - Involve relevant teams
Bring together IT, information security, data protection, compliance, and other relevant personnel. - Identify documentation gaps
Find missing or outdated evidence before submitting the questionnaire. - Review every response
Check that answers accurately represent your current cybersecurity practices.
CyberVadis itself recommends involving relevant IT, information security, data protection, legal, and compliance personnel because the assessment covers security practices across the organisation.
Benefits of CyberVadis Cybersecurity Assessment in Ahmedabad
A CyberVadis assessment gives Ahmedabad businesses insights into cybersecurity maturity, helping them identify gaps, strengthen controls, and improve stakeholder confidence.
- Demonstrate Cybersecurity Maturity: A CyberVadis scorecard gives customers and business partners a structured view of your cybersecurity performance.
- Identify Security Gaps: The assessment can highlight areas where your organisation needs stronger controls, better documentation, or more consistent monitoring.
- Support Customer Requirements: Some customers may request cybersecurity assessments before starting or expanding a business relationship. A CyberVadis assessment can help organisations respond to these requirements.
- Improve Internal Security Practices: Preparing for the assessment can encourage teams to formalise policies, strengthen controls, and maintain better security records.
- Support Continuous Improvement: The assessment does not end with the scorecard. CyberVadis provides an improvement plan that organisations can use to prioritise security enhancements.
Why Hire a CyberVadis Consultant in Ahmedabad?
Preparing for a CyberVadis assessment can involve several departments and a large amount of documentation. A consultant can act as a central point of coordination and help your organisation prepare systematically.
A CyberVadis consultant can help with:
- Understanding assessment requirements
- Reviewing existing cybersecurity controls
- Identifying documentation gaps
- Preparing an evidence checklist
- Mapping evidence to controls
- Reviewing questionnaire responses
- Identifying weak or incomplete responses
- Coordinating with IT and compliance teams
- Supporting remediation activities
- Conducting a readiness review before submission
The consultant does not replace your internal cybersecurity team. Instead, they can help your team interpret requirements and present existing practices more clearly and accurately.
Why Choose Global Quality Services for CyberVadis Assessment in Ahmedabad?
Global Quality Services helps businesses prepare for cybersecurity assessments by combining compliance knowledge with practical documentation support. Its consultants can review your existing security practices, identify gaps, organise supporting evidence, and guide your team through the assessment requirements.
For Ahmedabad businesses preparing for a customer-driven CyberVadis assessment, professional guidance can reduce confusion and help teams approach the questionnaire with greater clarity. The focus should remain on accurately representing your actual cybersecurity practices rather than simply trying to complete the questionnaire.
Frequently Asked Questions
1. What is a CyberVadis cybersecurity assessment?
CyberVadis is an evidence-based cybersecurity assessment that evaluates an organisation across Identify, Protect, Detect, and React functions and produces a cybersecurity scorecard.
2. Is CyberVadis the same as ISO 27001 certification?
No. ISO 27001 is a management-system standard that organisations can certify against, while CyberVadis assesses cybersecurity maturity using a tailored questionnaire and supporting evidence.
3. How long does a CyberVadis assessment take?
The full timeline varies by organisation. CyberVadis states that the questionnaire can take around two to three days when documentation is ready, while expert analysis generally takes several weeks.
4. What evidence does CyberVadis require?
Evidence can include policies, procedures, risk assessments, access records, technical screenshots, audit reports, training records, incident response documents, and other records supporting declared controls.
5. Can an Ahmedabad consultant help with CyberVadis preparation?
Yes. A consultant can help review controls, organise evidence, identify documentation gaps, prepare responses, and coordinate the assessment preparation process with relevant internal teams.