Software security has become a critical business requirement for companies developing applications that handle payment-related data or support payment environments. For software companies in Chennai, demonstrating that secure development practices are built into the software lifecycle can strengthen customer confidence and help address security requirements.
PCI Software Security Framework (PCI SSF) Certification in Chennai helps software vendors and developers assess their software development practices against the security expectations established by the Payment Card Industry Security Standards Council (PCI SSC). Global Quality Services supports organizations with assessment preparation, documentation, implementation guidance, and readiness activities required for the applicable PCI SSF program.
What Is PCI Software Security Framework Certification?
The PCI Software Security Framework is a collection of security standards developed by the PCI Security Standards Council for software vendors and developers. It focuses on integrating security into the software development lifecycle and addressing vulnerabilities that could affect payment account data.
PCI SSF includes frameworks designed for different software environments and development models. Organizations need to determine the applicable program and assessment requirements based on the nature of their software, development processes, and payment-related functions.
A PCI SSF assessment can examine areas such as:
- Secure software development practices
- Software design and architecture
- Identification and management of security vulnerabilities
- Secure coding practices
- Authentication and access controls
- Software testing and security verification
- Change and release management
- Vulnerability remediation
- Security documentation and evidence
- Protection of sensitive payment-related information
Importance of PCI Software Security Framework Certification in Chennai
Chennai has a large technology and IT services ecosystem, with companies involved in software development, SaaS platforms, fintech, digital commerce, payment technology, and enterprise applications.
For organizations operating in these sectors, security requirements may become an important part of customer contracts, vendor assessments, payment ecosystem relationships, and regulatory or contractual obligations.
PCI SSF can help organizations establish a structured approach to software security and demonstrate that security controls are incorporated throughout the software development lifecycle.
Benefits of PCI Software Security Framework Certification
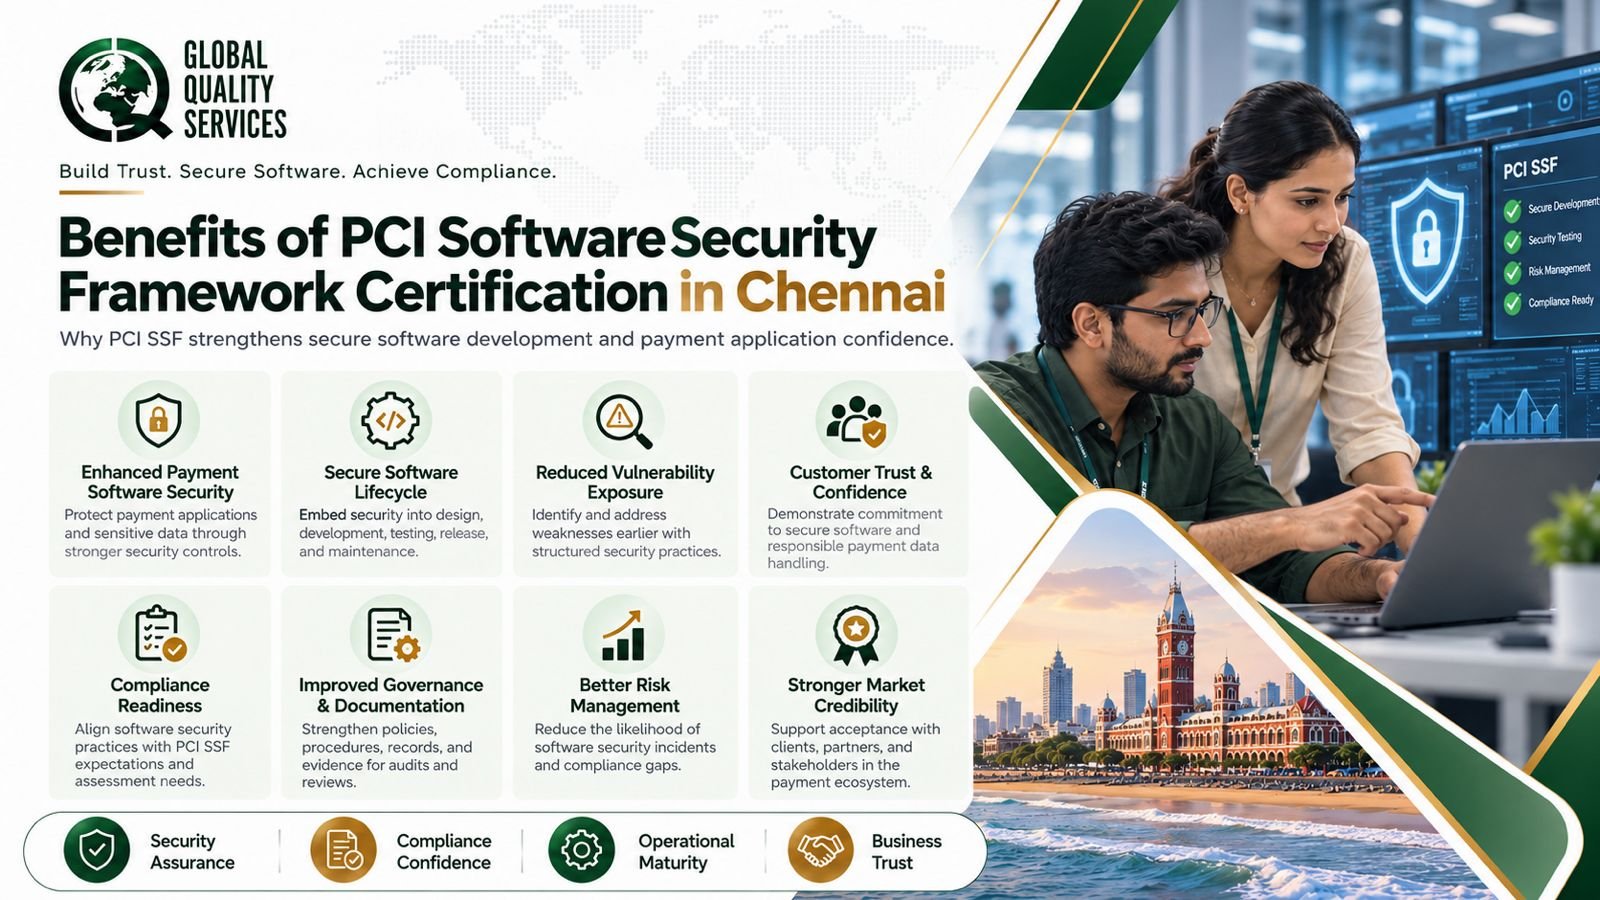
Working toward PCI SSF compliance can provide several business and security benefits:
- Establishes a structured software security approach
- Helps identify weaknesses in software development processes
- Strengthens secure coding and testing practices
- Improves vulnerability management
- Supports customer and partner security requirements
- Builds greater confidence in software security
- Provides documented evidence of security practices
- Supports organizations operating in payment-related technology environments
- Encourages security throughout the software development lifecycle
Which Organization Must Apply for PCI Software Security Framework Certification in Chennai
The following industries in Chennai may need to consider PCI SSF based on the nature and function of their software:
Fintech Companies
Fintech companies develop applications and platforms for digital payments, financial transactions, banking services, lending, wallets, and other financial activities. Since their software may process, facilitate, or support payment transactions, secure software development and vulnerability management are important considerations. PCI SSF can provide a structured framework for addressing security throughout the software lifecycle.
Payment Application Developers
Companies developing payment applications need to pay particular attention to software security because their products may directly support payment transactions. PCI SSF helps address security requirements related to software design, development, testing, vulnerability management, and protection of payment-related functions.
SaaS Providers
SaaS companies providing platforms that support payment processing, billing, subscriptions, merchant operations, or other payment-related activities may need to evaluate PCI SSF applicability. Demonstrating structured software security practices can also help SaaS providers address security expectations from enterprise customers and business partners.
E-Commerce Technology Providers
E-commerce software often connects customers, merchants, payment gateways, shopping platforms, and transaction systems. Companies developing checkout software, payment integrations, shopping platforms, or related applications should evaluate PCI SSF requirements where their software is involved in payment environments.
Digital Payment Solution Providers
Organizations developing mobile wallets, digital payment platforms, transaction applications, payment gateways, or supporting technologies need strong software security controls. PCI SSF can help establish security practices across development, testing, release, and ongoing maintenance of payment-related software.
Mobile Application Developers
Mobile applications increasingly support purchases, subscriptions, digital wallets, and other payment functions. Developers creating applications that facilitate payment-related activities should evaluate whether their software falls within an applicable PCI SSF program and ensure security is considered throughout the development lifecycle.
Software Product Companies
Software product companies developing applications for financial, retail, hospitality, healthcare, or other sectors may encounter PCI SSF requirements when their products support payment-related processes. A structured software security framework can help address vulnerabilities and demonstrate appropriate development practices to customers.
Banking and Financial Services Technology Providers
Technology companies developing software for banks, financial institutions, payment service providers, and other financial organizations may face specific security expectations from their customers. PCI SSF can be relevant where the software supports payment-related functions and falls within the scope of an applicable PCI SSC program.
IT and Technology Service Providers
IT companies that develop, customize, maintain, or manage payment-related software for clients should assess whether PCI SSF requirements apply to the software they provide. Secure development practices, vulnerability management, access controls, and software testing can become important parts of customer security requirements.
Payment Gateway and Integration Providers
Payment gateway and payment integration software connects merchants or applications with payment processing environments. Because these systems can be closely associated with payment transactions, organizations developing such software should evaluate the applicable PCI SSF requirements and maintain appropriate software security practices.
Retail Technology Companies
Retail technology providers developing point-of-sale applications, payment integrations, billing platforms, customer transaction systems, or merchant software may need to consider PCI SSF where their software supports payment-related activities. Secure development can help reduce vulnerabilities within applications used by merchants and retailers.
Hospitality and Travel Technology Providers
Hotels, travel platforms, booking systems, and hospitality technology providers often use software that supports reservations, online payments, billing, and customer transactions. Companies developing these payment-enabled platforms should evaluate whether PCI SSF applies to their software and establish appropriate security practices.
Companies Supplying Software to Payment-Related Businesses
Software vendors supplying applications to banks, fintech companies, payment service providers, merchants, or other payment-related organizations may encounter PCI SSF requirements as part of customer or contractual security expectations. Evaluating PCI SSF applicability early can help vendors understand the security controls and evidence expected for their software.
Chennai Locations Covered for PCI SSF Support
Organizations operating from Taramani, OMR, Guindy, Ambattur, Perungudi, Sholinganallur, Adyar, Velachery, and other Chennai technology and industrial locations can seek support for PCI SSF applicability review, gap assessment, documentation, and assessment preparation.
What Does a PCI SSF Assessment Cover?
A PCI SSF assessment looks beyond the final software product. It can involve an examination of the processes used to design, develop, test, release, and maintain the software.
Secure Software Development
The organization should have defined processes for incorporating security throughout software development. This includes security considerations during requirements, design, coding, testing, and release.
Vulnerability Management
Organizations need processes for identifying, evaluating, tracking, and addressing vulnerabilities affecting their software and development environment.
Security Testing
Security testing should be incorporated into appropriate stages of the software development lifecycle. Evidence from testing and remediation activities may form an important part of an assessment.
Access and Change Controls
Development environments, source code, build systems, and production releases should be protected through appropriate access and change-management controls.
Documentation and Evidence
Policies, procedures, records, test results, vulnerability reports, development evidence, and other documentation may be reviewed to demonstrate that required security practices are operating consistently.
How Can Global Quality Services Help with PCI SSF Certification in Chennai?
Global Quality Services provides consulting and certification support to organizations preparing for PCI Software Security Framework assessments.
Our support can include understanding applicable PCI SSF requirements, conducting a gap assessment, reviewing existing security processes, identifying documentation requirements, supporting remediation activities, and preparing the organization for the assessment.
For Chennai-based software companies, the approach can be aligned with the organization’s software development model, technology environment, existing security controls, and customer requirements.
Why Choose Global Quality Services?
Organizations preparing for PCI SSF can benefit from a structured approach rather than treating assessment preparation as a last-minute documentation exercise.
Get Support for PCI Software Security Framework Certification in Chennai
If your software organization in Chennai needs to understand PCI SSF requirements or prepare for an assessment, Global Quality Services can help you identify applicable requirements, evaluate existing practices, address gaps, and organize the required assessment evidence.
Contact Global Quality Services to discuss your software environment and PCI Software Security Framework certification requirements.
Frequently Asked Questions
1. What is PCI Software Security Framework Certification?
PCI Software Security Framework Certification refers to demonstrating that applicable software development and security practices meet the requirements of the relevant PCI SSC software security framework and assessment program.
2. Is PCI SSF applicable to all software companies in Chennai?
No. Applicability depends on the type of software, how it is developed and deployed, its relationship with payment environments, and the organization’s specific business and customer requirements.
3. How long does PCI SSF certification take?
The timeline varies according to the organization’s size, software environment, existing security controls, documentation, and gaps identified during preparation. A gap assessment can provide a more realistic estimate.
4. Can a software company prepare for PCI SSF without changing its entire development process?
PCI SSF preparation does not necessarily mean replacing an organization’s entire development methodology. The focus is on meeting applicable security requirements and integrating appropriate security practices into the existing software development lifecycle.
5. Does PCI SSF certification need to be maintained?
PCI SSF requirements involve ongoing security practices and assessment activities. Organizations should continue maintaining applicable controls, monitoring vulnerabilities, addressing changes, and meeting the requirements of their specific PCI SSF program.