Noida has become a major technology and business hub in the Delhi NCR region, with a strong presence of IT and ITES companies, software developers, fintech businesses, electronics companies, GCCs, e-commerce businesses, and digital service providers. Its growing technology ecosystem makes software security an important consideration for organizations developing applications used in payment-related environments.
PCI Software Security Framework Certification in Noida helps eligible software organizations establish and demonstrate structured security practices across software development, testing, deployment, and maintenance.
What Is PCI Software Security Framework Certification?
The PCI Software Security Framework (PCI SSF) is a collection of software security standards and validation programs developed by the Payment Card Industry Security Standards Council (PCI SSC). The framework includes the PCI Secure Software Standard and the PCI Secure Software Lifecycle (Secure SLC) Standard. Applicable requirements depend on the software’s nature, its payment-related functions, and the organization’s business model. PCI SSF can cover secure software development, vulnerability management, security testing, access controls, software changes, and security documentation.
Organizations preparing for PCI SSF can benefit from a structured approach to software security.
- Strengthens secure software development practices
- Helps identify software security weaknesses
- Supports vulnerability management
- Improves security testing processes
- Encourages security throughout the software lifecycle
- Helps address customer and contractual security requirements
- Provides structured evidence of software security practices
- Supports organizations operating in payment-related technology environments
Which Sectors in Noida Should Consider PCI SSF?
Noida’s technology ecosystem includes several sectors where software security can be an important business requirement.
Fintech and Payment Technology
Fintech companies developing payment platforms, transaction applications, digital payment solutions, and related technologies may need to evaluate applicable PCI SSF requirements.
SaaS and Software Product Companies
SaaS providers and software product companies developing applications for payment-related customers or environments can consider PCI SSF as part of their software security and customer assurance requirements.
E-Commerce and Digital Commerce
Companies developing e-commerce platforms, checkout systems, payment integrations, merchant applications, and other digital commerce technologies may need to determine whether their software falls within an applicable PCI SSF program.
IT and ITES Companies
Noida’s large IT and ITES sector includes organizations providing software development and technology services to businesses across industries. Companies developing payment-related software should evaluate the applicable PCI SSF requirements.
Electronics and Technology Companies
Organizations involved in electronics, embedded software, connected technologies, and payment-related technology solutions may also need to assess their software security requirements.
Mobile and Web Application Developers
Companies developing applications that facilitate or support payment-related activities can review their software development, testing, vulnerability management, and security controls against applicable PCI SSF requirements.
Areas We Cover in Noida
PCI Software Security Framework certification support is available across Noida’s major IT, technology, commercial, and business hubs. We work with eligible software and technology organizations across the city and nearby business districts.
- Sector 62
- Sector 63
- Sector 125
- Sector 126
- Sector 127
- Sector 135
- Noida Expressway
- Sector 142
- Sector 144
- Greater Noida
Other business and technology locations across Noida and Delhi NCR
What Does PCI SSF Assessment Cover?
PCI SSF assessment preparation can involve reviewing the organization’s software development lifecycle and security practices.
Secure Software Development
Security considerations should be incorporated into relevant stages of software development, including requirements, architecture, design, coding, testing, deployment, and maintenance.
Vulnerability Management
Organizations need appropriate processes to identify, evaluate, track, and address vulnerabilities affecting their software.
Security Testing
Security testing and verification activities should be performed at appropriate stages of the software development lifecycle, with suitable evidence maintained.
Access and Change Management
Controls relating to source code, development environments, user access, software releases, and changes may form part of the assessment.
Documentation and Evidence
Organizations need appropriate policies, procedures, records, testing results, vulnerability information, and other evidence to demonstrate that applicable security practices are implemented.
PCI Software Security Framework Certification Process in Noida
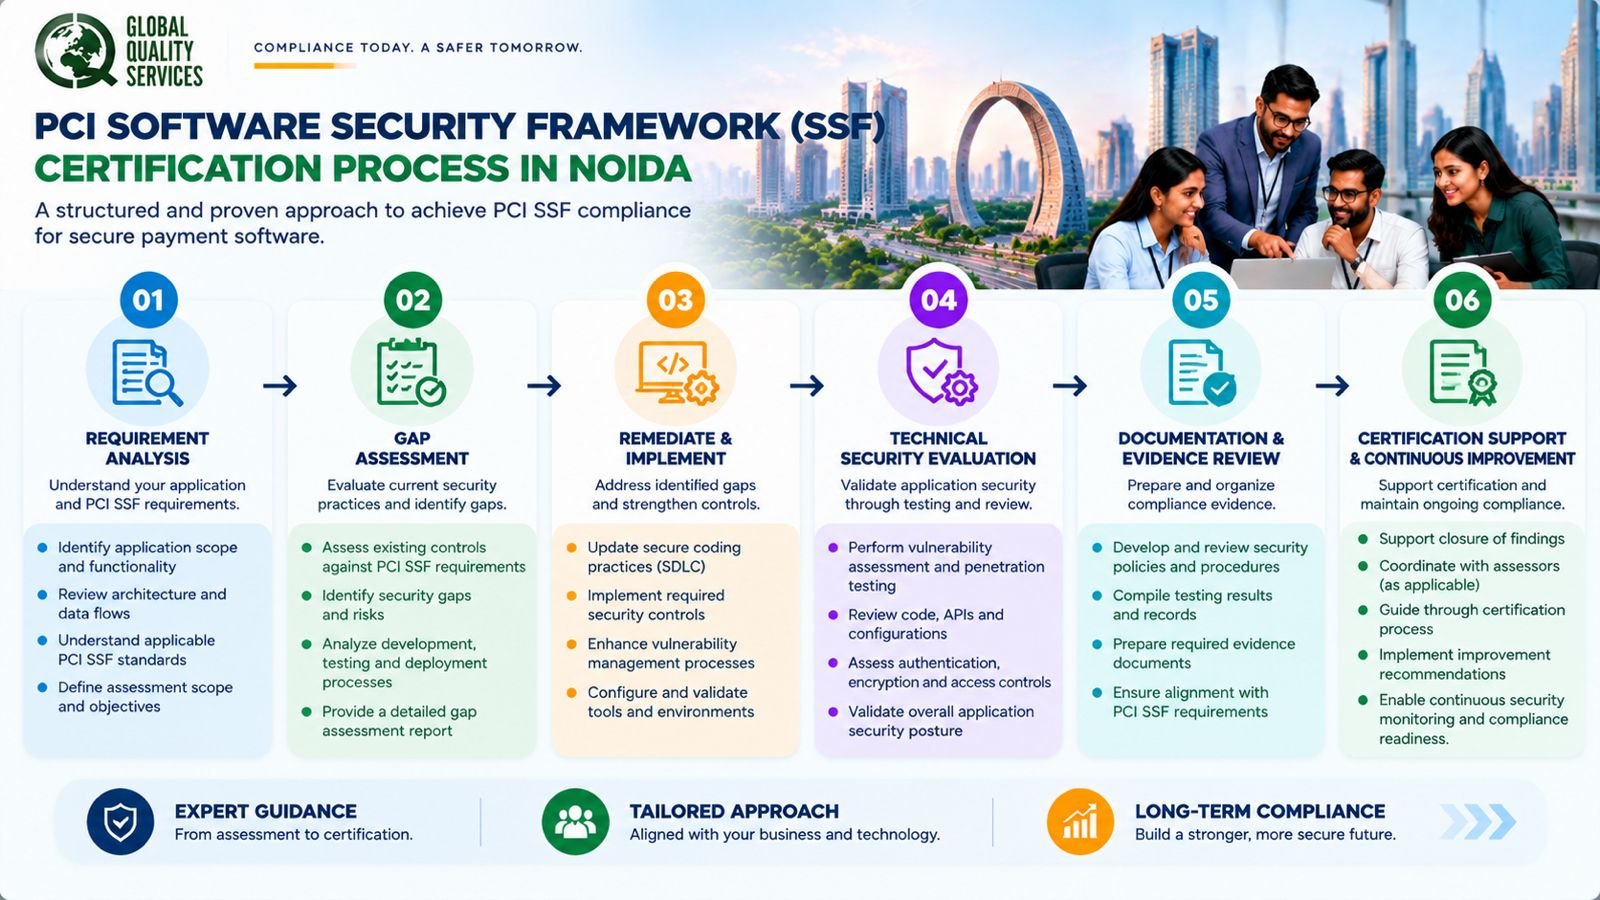
1. Determine PCI SSF Applicability
The first step is to understand the organization’s software, payment-related functions, business model, and the PCI SSF requirements that may apply.
2. Conduct a Gap Assessment
Review existing software development and security practices against applicable requirements. This helps identify missing controls, process gaps, and documentation requirements.
3. Implement Required Improvements
The organization addresses identified gaps by strengthening relevant software development, security testing, vulnerability management, access control, change management, and documentation practices.
4. Prepare Documentation and Evidence
Policies, procedures, technical records, testing results, vulnerability management records, and other required evidence are organized for assessment.
5. Complete the Applicable Assessment
The organization undergoes the applicable assessment with the appropriate PCI SSF assessor or assessment organization.
6. Maintain Security Practices
After the assessment, organizations should continue to maintain and update applicable security practices as software, technology environments, vulnerabilities, and business requirements change.
How Can Global Quality Services Help with PCI SSF Certification in Noida?
Global Quality Services helps organizations in Noida prepare for applicable PCI Software Security Framework requirements by reviewing their existing software security practices, identifying gaps, supporting documentation development, assisting with remediation planning, and preparing relevant evidence for the assessment.
Our approach aligns with the organization’s software architecture, development methodology, security controls, technology environment, and customer requirements, whether the organization operates from Sector 62, Sector 63, the Noida Expressway, Greater Noida, or another technology and business location in the region.
PCI SSF preparation needs to reflect the organization’s actual software development and security processes rather than becoming a documentation-only exercise.
Global Quality Services can help organizations establish a structured preparation approach and understand the requirements applicable to their software and business environment.
Frequently Asked Questions
1. Who needs PCI Software Security Framework Certification in Noida?
Software vendors developing payment software or software used in payment-related environments should evaluate the applicable PCI SSF requirements. Fintech, SaaS, e-commerce, IT, payment technology, and digital application companies may therefore need to consider PCI SSF based on their software and business model.
2. Is PCI SSF the same as PCI DSS?
No. PCI DSS focuses on payment account data security requirements for entities in the payment card ecosystem, while PCI SSF focuses on software security and secure software development for applicable payment-related software.
3. Which PCI SSF standard applies to my software?
The applicable standard depends on the nature and function of the software and the organization’s circumstances. The PCI SSF includes the PCI Secure Software Standard and PCI Secure Software Lifecycle Standard.
4. Can SaaS companies in Noida consider PCI SSF?
Yes, SaaS organizations can evaluate PCI SSF applicability when their software is developed for or used in payment-related environments. The applicable PCI SSC requirements should be reviewed based on the software and business model.
5. How long does PCI SSF certification take?
The timeline varies according to the software environment, existing security controls, documentation, scope, and gaps identified during preparation. A preliminary gap assessment can help establish a more realistic timeline.
Get Started with PCI Software Security Framework Certification in Noida
If your organization develops payment software or software used in payment-related environments, understanding the applicable PCI SSF requirements can help you establish a structured approach to software security.
Contact Global Quality Services for PCI Software Security Framework Certification support in Noida and discuss your software security and assessment preparation requirements.