Hyderabad has emerged as a leading center for IT services, SaaS providers, startups, and Global Capability Centers, and thus, data protection and consumer confidence are vital concerns for organizations processing sensitive information. Indeed, India’s IT & ITeS sector accounted for revenues of $283 billion in FY2025 alone, and there were over 2,100 GCCs operating throughout the nation. However, there were 29,44,248 cybersecurity attacks registered in India in 2025 by CERT-In, indicating an increased requirement for robust security protocols.
SOC 2 Type I and Type II certifications help Hyderabad-based organizations serving international clientele provide evidence of effective security controls and their management practices. However, what should you know about each option? Which one is best suited to your organization, and how does the certification process work? Find out everything you need to know about SOC 2 Certification Hyderabad.
What is SOC 2 Type I vs Type II Certification
There are two report formats within the SOC 2 framework: Type I and Type II. Both report formats assess how well your company’s control processes align with the SOC 2 Trust Services Criteria, but each evaluates something different about them.
- SOC 2 Type I Report: This report verifies that your security controls and other relevant controls are effectively designed and in operation as of the assessment date. Essentially, this means the necessary controls exist within your system at the exact time the assessor reviewed it.
- SOC 2 Type II Report: This type takes things a bit further by verifying that these same controls not only exist within your system, but are consistently operational throughout a set timeframe.
Why SOC 2 Matters for Service Organizations
Service organizations in Hyderabad handle sensitive information on a daily basis, whether in IT, cloud hosting, or financial services. Without strict controls, the risk of breaches or misuse rises sharply. SOC 2 Certification provides independent assurance that your company follows global best practices for data protection.
- Protects Customer Data: Safeguards customer, financial, business, and personal information using formal security controls.
- Increases Client Confidence: Assures your customers that you have effective measures in place to protect their data.
- Aids in Securing International Deals: Facilitates meeting the security needs of your international and enterprise customers.
- Mitigates Information Security Threats: Assists in detecting and addressing vulnerabilities related to access controls, information security, monitoring, and security incident management.
- Boosts Market Credibility: Improves security credibility for Hyderabad-based IT, SaaS, cloud computing, and outsourcing firms.
- Enhances Internal Security Controls: Establishes formal procedures for managing users’ access rights, systems, data, risk management, and security incidents.
- Fuels Organizational Expansion: Offers a structure for controlling your growing customer base, offerings, infrastructure, and operations.
- Offers Third-Party Validation: Offers your clients formal documentation confirming that the applicable controls were properly designed and implemented. For Type II reports, this includes demonstrating effectiveness during operation over time.
What Are the SOC 2 Trust Services Criteria
SOC 2 Trust Services Criteria outline criteria that the controls of an organization can be evaluated against when going through a SOC 2 audit. They assess whether an organization has implemented sufficient controls for the handling and safeguarding of information. The five Trust Services Criteria include:
- Security involves safeguarding against any threat to systems and information.
- Availability means maintaining the availability of services and systems.
- Processing integrity ensures proper functioning of processes to ensure accuracy and completeness.
- Confidentiality refers to the safeguarding of information classified as confidential.
- Privacy covers the collection, use, retention, disclosure, and proper disposal of personally identifiable information.
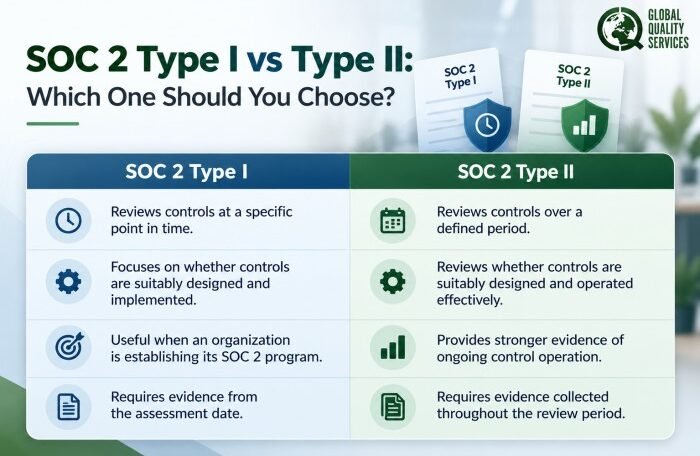
SOC 2 Type I vs Type II: Which One Should You Choose
The right SOC 2 report depends on your business needs, customer expectations, and how mature your controls are:
The SOC 2 Certification Process in Hyderabad
The journey to SOC 2 Certification in Hyderabad involves several stages. Each step ensures your organization is ready for a successful audit and compliance:
Step 1: Gap Analysis
Evaluate your current set of security controls and practices compared to the SOC 2 Trust Services Criteria requirements.
Step 2: Control Implementation
Build out policies and procedures, access controls, monitoring capabilities, risk assessment and mitigation procedures, and any additional necessary controls to meet the criteria.
Step 3: Control Testing
Test these controls to ensure they function as expected. This step uncovers and resolves any gaps prior to the official audit.
Step 4: Independent SOC 2 Audit
Here’s where an independent CPA firm comes in to test the effectiveness of your controls. In the case of a Type I assessment, only the controls at a certain point in time get assessed. But for Type II, the auditor must examine evidence of control operation effectiveness throughout the review period as well.
Step 5: SOC 2 Report and Ongoing Compliance
Following this audit process, the report will be issued according to your assessment findings. It’s important to keep testing those controls moving forward.
Benefits of SOC 2 Certification for Businesses
SOC 2 Certification helps businesses strengthen their security practices while making it easier to build trust with customers, partners, and international clients:
- Security Controls and Access Management: It protects sensitive information using predetermined controls and limitations around who accesses what and when.
- Customer Trust and Peace of Mind: You give your customers peace of mind in the knowledge that their data is being securely stored using proven practices.
- International Clients: It meets security requirements necessary to attract global clients and large enterprises.
- Finding Weaknesses in Your Operations: By regularly auditing your security controls, you identify gaps that need to be closed.
- Process Improvement: A SOC 2 engagement leads to a process that governs how you handle access, monitoring, incidents, and handling data.
- Professionalism and Accountability: It proves your commitment to proper data management.
- Growing Your Business: A SOC 2 report will improve your standing as you expand into new markets or pursue bigger contracts.
- Ongoing Proof of Effectiveness: Unlike SOC 2 Type I reports, SOC 2 Type II shows that the relevant controls worked consistently during a period of time.
SOC 2 certification is especially important for businesses that operate in key tech and commercial hubs within Hyderabad such as HITEC City, Madhapur, Gachibowli, Kondapur, Nanakramguda, Financial District, Raidurg, Begumpet, Banjara Hills, Jubilee Hills, Secunderabad, Uppal, and Manikonda. Organizations based in these regions include IT firms, SaaS vendors, fintech organizations, GCCs, cloud computing services, and many more.
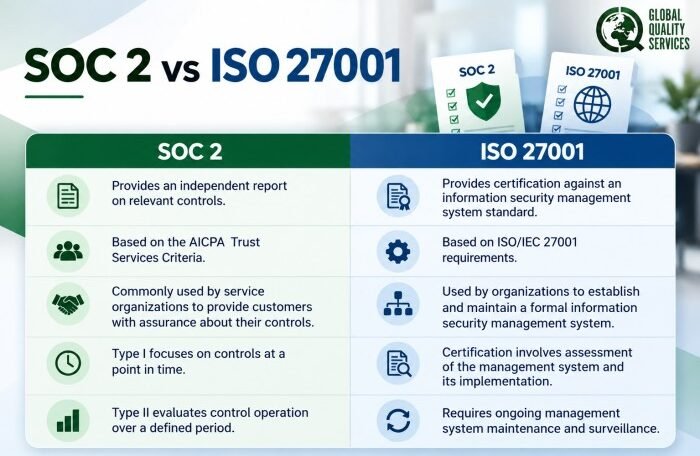
SOC 2 vs ISO 27001 Certification
SOC 2 and ISO 27001 both address information security, but they serve different purposes:
Industries in Hyderabad That Require SOC 2 Certification
Several industries increasingly rely on SOC 2 Certification in Hyderabad to assure clients of data protection. Here are the list of industries that require SOC 2 certification:
- SaaS and Technology
- IT and ITES
- FinTech and BFSI
- Healthcare and HealthTech
- Cloud Computing and Data Services
- E-commerce and Retail
- EdTech
- Business Process Outsourcing (BPO)
- Insurance and InsurTech
- AI, ML and Data Companies
- Global Capability Centres (GCCs)
- Telecommunications
- Professional Service
Documents and Evidence Required for SOC 2
Organizations must demonstrate how their controls are adequately executed and, if it’s SOC 2 Type II, working effectively throughout the review period. Here is the list of documents:
- Information security policies and procedures
- User access records and access reviews
- Employee security training records
- Risk assessment and risk treatment records
- Incident response records
- Vendor and third-party assessments
- System change management records
- Backup and recovery records
- Security monitoring and testing evidence
- Asset inventories
- Password and authentication controls
- Business continuity and disaster recovery records
Cost and Timeline for SOC 2 Certification
SOC 2 certification fees in Hyderabad depend on several things, including your organization’s size, audit scope, number of systems, existing controls, and whether you choose a Type I or Type II SOC 2 report. Type II reports will likely cost more since they look at how controls function over an extended period.
This process takes different amounts of time depending on your preparedness. Organizations that have already developed policies and implemented security controls should expect the process to move quickly, whereas those just getting started may need extra time for planning and documentation. To get started, a SOC 2 gap assessment can tell you where you stand and help you prepare for the external audit.
Common SOC 2 Compliance Challenges
Preparing for SOC 2 can be difficult when security processes are informal, or evidence is not consistently maintained:
- Incomplete Documentation: The company might have policies but lacks clear documentation of how controls should be executed.
- Lack of Access Review: Users’ access isn’t always reviewed and revoked upon changes to their duties.
- Insufficient Audit Trail: Teams conduct necessary processes but fall short on maintaining proper evidence of them.
- Consistent Security Monitoring Failure: Security incidents and system activity aren’t monitored or logged as needed.
- Insufficient Vendor Management: There’s no systematic approach to assessing third-party threats to information security.
- Undefined Roles: Staff aren’t provided with clear responsibilities regarding implementation and evaluation of controls.
- Insufficient Pretesting of Controls: No pre-testing happens at a business level prior to the SOC 2 review.
Who Issues the SOC 2 Report
SOC 2 reports come from examinations carried out by third-party licensed CPA firms. In this case, the service auditor evaluates the controls within the organization according to the relevant Trust Services Criteria and then produces the SOC 2 report.
A SOC 2 consultant does not produce the actual SOC 2 report at the end of the day. However, consultants may play a role in getting your organization ready through processes such as gap assessments, control improvement, documentation support, evidence preparation, and readiness reviews.
Summary Points
- SOC 2 helps organisations prove they protect customer data with strong security and privacy controls.
- It evaluates how well your systems manage data security, availability, confidentiality, and processing integrity.
- The certification builds client trust by showing your controls work consistently, not just on paper.
- It strengthens internal processes and improves accountability across people, systems, and operations.
- SOC 2 reduces data breach risks and supports compliance with global client expectations.
- For Hyderabad-based businesses, it enhances credibility and opens doors to international contracts and partnerships.
Why Partner with GQS for SOC 2 Certification in Hyderabad?
Global Quality Services has extensive experience guiding organizations through SOC 2 Certification, offering tailored solutions that meet global expectations.
- 26 Years of Consultancy Expertise: Leverage experience in delivering management systems consultancy services, compliance consultancy, and certification consultancy for companies operating in different sectors.
- Respected SOC 2 Consultant: Work with a respected consultant who aims to make SOC 2 simpler for organizations through practical advice.
- Full-Fledged Services: Enjoy services ranging from gap analysis and controls implementation to documentation assistance and readiness assessment. Industry
- Specific Solutions: Obtain customized SOC 2 solutions suitable for IT firms, SaaS vendors, BPO providers, fintech organizations, healthcare businesses, and similar service organizations.
- Compliance Across Borders: Implement security controls that comply with SOC 2 guidelines as well as international client demands.
By partnering with Global Quality Services, Hyderabad companies achieve SOC 2 compliance faster, with greater efficiency, and stronger business outcomes.
Get SOC 2 Certification in Hyderabad with Global Quality Services
Build stronger trust with clients and demonstrate your commitment to data security with SOC 2 Certification in Hyderabad. We provide practical, end-to-end support from gap assessment and control implementation to documentation and audit readiness, helping your business move through the process with greater clarity and confidence.
- Strengthen data security and internal controls
- Build credibility with global clients
- Support enterprise contract opportunities
- Prepare efficiently for the SOC 2 audit
Take the next step toward stronger security and global business opportunities with us. Talk to our team today to start your journey.
Frequently Asked Questions
1. Who provides SOC 2 Certification in Hyderabad?
SOC 2 Certification in Hyderabad is granted after an independent audit by licensed CPA firms. While GQS prepares businesses with assessments, implementation, and readiness, only accredited auditors issue the report. This ensures companies achieve compliance while also receiving expert support throughout the certification journey.
2. Does GQS perform the actual audit for SOC 2 Certification?
GQS does not conduct the final audit. Instead, we support businesses in Hyderabad by preparing them for SOC 2 certification through readiness checks, gap closure, and documentation. The final audit is carried out by certified CPA firms, ensuring transparency and independence in the certification process.
3. Is SOC 2 Certification mandatory for IT and service companies?
SOC 2 Certification in Hyderabad is not legally mandatory, but it has become a business necessity. Global clients, especially in the U.S. and Europe, require SOC 2 compliance before outsourcing projects. For IT, BPO, and fintech companies in Hyderabad, certification enhances credibility and opens up new international business opportunities.
4. Can startups also benefit from SOC 2 Certification?
Yes, startups benefit significantly from SOC 2 Certification in Hyderabad. Early compliance demonstrates strong security practices to investors and clients, giving startups a competitive edge. For young companies in Hyderabad’s IT and fintech ecosystem, SOC 2 compliance builds trust quickly and accelerates business partnerships at a global scale.
5. How often should SOC 2 Certification be renewed?
SOC 2 Certification in Hyderabad is renewed annually. Type II reports cover continuous monitoring over a period of 6–12 months, requiring yearly updates to stay valid. With GQS, businesses establish long-term compliance systems, making renewals more straightforward and ensuring they remain trusted partners for global clients.