India’s capital of finance and fintech, Mumbai, creates high demand for securing payment cards. According to the Government of Maharashtra’s Mumbai Fintech Hub, there are currently 500+ fintech companies collaborating within its ecosystem.
Payment Card Industry Data Security Standard (PCI DSS) offers a methodology for organisations that store, process, or transmit sensitive payment card data. It’s a well-known security framework in the industry today. PCI DSS v4.0.1 is the latest version of the PCI DSS requirements, and an appropriate self-assessment questionnaire (SAQ), attestation of compliance (AOC), or compliance report (ROC) will depend on the scope and validation requirements for each organisation.
GQS offers PCI DSS consulting and assessment solutions for Mumbai-based enterprises. By doing so, we will be able to assist our clients in evaluating their PCI DSS environment, assessing potential gaps in controls, preparing the necessary evidence, and preparing themselves for validation. This is applicable to fintech companies, ecommerce organisations, payment services, banks, software-as-a-service providers, or any other type of business dealing with card payments. Find out how PCI DSS compliance can be achieved for your organisation based in Mumbai below.
What is PCI DSS Certification
PCI DSS Certification refers to the Payment Card Industry Data Security Standard, an international framework designed to safeguard cardholder data during storage, processing, and transmission. Key objectives of PCI DSS Certification in Mumbai include:
- Building a secure network and system infrastructure.
- Protecting stored cardholder data through encryption and restricted access.
- Monitoring and testing systems regularly to prevent breaches.
- Maintaining a robust security policy for all employees.
By obtaining PCI DSS Certification in Mumbai, your business assures clients and partners that it prioritizes security and compliance at every level.
Why PCI DSS Certification in Mumbai Matters
Financial services organizations, fintech startups, tech firms, retail brands, and e-commerce operations congregate in Mumbai. The fintech startup scene in Mumbai receives significant support from the Government of Maharashtra via its Mumbai Fintech Hub program.
Payment security is not solely a matter of IT infrastructure for these businesses. It impacts consumer trust, banking partnerships, supplier evaluations, and collaborations with payment processors. Reasons why your business should get PCI DSS Certification in Mumbai:
- Protect cardholder and payment account data
- Identify weaknesses in payment-related systems
- Improve access control and authentication practices
- Strengthen vulnerability management
- Establish better security monitoring
- Demonstrate compliance to relevant business partners
- Prepare required compliance documentation
- Reduce avoidable security and compliance gaps
- Build stronger payment security practices
Although PCI DSS is intended to be used for securing payment card data, many companies adopt the practice of enhancing their data management framework by obtaining an ISO 27001 Certification.
Which Mumbai Businesses Need PCI DSS Compliance
Here is a list of businesses that need PCI DSS compliance:
- Banking and Financial Services
- Fintech Companies
- Payment Gateways and Payment Service Providers
- E-commerce and Online Marketplaces
- SaaS and IT Service Providers
- Retail and Hospitality
PCI DSS v4.0.1: What Mumbai Businesses Should KnowPCI DSS v4.0.1
PCI DSS v4.0.1 is the current active version of PCI DSS. This is essentially a minor update of v4.0 published by PCI SSC in order to fix any problems or misunderstandings with the standards document while leaving the core requirements unchanged. Some key aspects highlighted in the newer framework include:
- Understanding and confirming PCI DSS scope
- Targeted risk analysis
- Defined security responsibilities
- Stronger authentication controls
- Vulnerability management
- Payment page security
- Ongoing monitoring
- Third-party service provider management
- Documented security practices
- Evidence that controls are operating effectively
This means businesses should not treat PCI DSS as a documentation exercise. The actual security environment, supporting technology, people, processes and evidence all need to align with the applicable requirements.
Understanding PCI DSS Scope Before You Start
One of the most critical elements involved in PCI DSS compliance is figuring out what is in scope. Initially, a company might think that PCI DSS applies only to the application or the payment page where card data is entered.
In fact, scope can go beyond that and cover all systems and networks, administrative access, cloud environments, security systems, remote access technology, and third parties who have any bearing on the security of the cardholder data environment. Global Quality Services assists companies in analyzing the payment environment before the compliance process gets too far. This includes checking up on:
- Cardholder data flows
- Applications
- Databases
- Networks
- Cloud infrastructure
- Payment systems
- Workstations
- Administrative systems
- Security technologies
- Remote access
- Third-party providers
- Supporting systems
- 2Access privileges
PCI DSS Certification Process in Mumbai
At Global Quality Services, we simplify the certification process for organizations of all sizes:
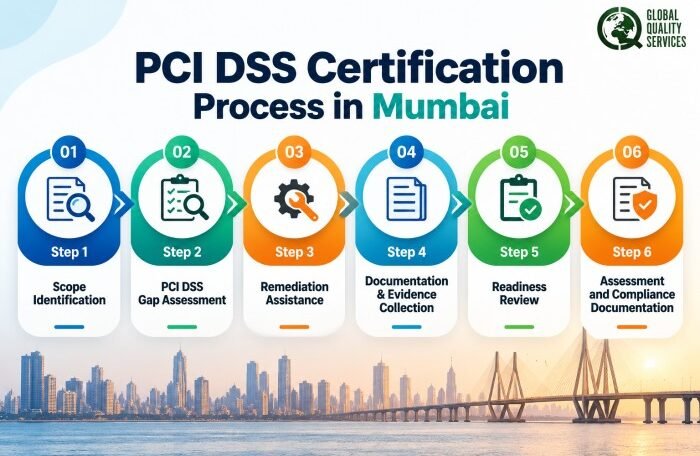
Step 1: Scope Identification
This step involves identifying how the payment data flows in your organization and identifying systems, individuals, technology and third parties involved in the cardholder data environment.
Step 2: PCI DSS Gap Assessment
Global Quality Services assesses your existing controls with regard to applicable PCI DSS controls and determines areas requiring attention.
Step 3: Remediation Assistance
The gaps are then prioritized in accordance with applicability to your environment. Our consultants will assist your organization in making the necessary adjustments.
Step 4: Documentation & Evidence Collection
The documents and evidence are collected in line with the applicable PCI DSS controls.
Step 5: Readiness Review
Prior to the validation process, GQS examines the existing evidence and controls that have been put into practice for unresolved concerns.
Step 6: Assessment and Compliance Documentation
Your organization’s needs dictate which validation process you would undertake. It could be the SAQ, AOC, ROC, and more documentation as required.
Common PCI DSS Gaps We Find in Businesses
Many businesses believe that having a firewall, antivirus software, and encryption automatically means their payment environment is compliant.
PCI DSS is broader than that. Common areas requiring attention can include:
- Unclear PCI DSS scope
- Incomplete asset inventories
- Poorly documented cardholder data flows
- Excessive user access
- Weak authentication controls
- Missing access reviews
- Incomplete logging
- Weak log monitoring
- Delayed vulnerability remediation
- Incomplete security testing
- Poor change management
- Inadequate incident response documentation
- Unsupported software
- Weak application security
- Incomplete third-party documentation
Key Benefits of PCI DSS Certification in Mumbai
PCI DSS Certification in Mumbai offers both compliance and competitive advantage:
- Enhances brand credibility and consumer confidence.
- Protects against cyberattacks and data breaches.
- Enables partnerships with major payment brands.
- Minimizes financial losses due to fraud.
- Ensures continuous monitoring and security improvement
PCI DSS Compliance Support Across Mumbai’s Business Areas
Global Quality Services can support organisations across Mumbai and its major commercial and technology zones, including:
- Andheri
- Andheri East
- Powai
- Bandra
- Bandra Kurla Complex
- Lower Parel
- Goregaon
- Malad
- Vile Parle
- Worli
- Fort
- Nariman Point
- Colaba
- Navi Mumbai
- Thane and the wider Mumbai Metropolitan Region
PCI DSS and Other Information Security Standards
While the PCI DSS deals strictly with payment account data security, there are other organisations that may need further information security measures due to customer demands, contractual agreements, and organisational security policies.
Organisations seeking to have a strong information security management system in addition to PCI DSS may want to look at getting ISO 27001 Certification in Mumbai. It is important to remember that PCI DSS and ISO 27001 are not mutually exclusive standards; rather, the former takes care of payment security and the latter offers a broader approach to information security management.
PCI DSS Certification Cost in Mumbai
There is no single PCI DSS cost applicable to every Mumbai business. The overall cost depends on the organisation’s:
- Size and complexity
- Number of systems in scope
- Cardholder data environment
- Payment channels
- Number of locations
- Third-party dependencies
- Existing security controls
- Required testing
- Required documentation
- Validation method
- Acquirer or payment brand requirements
How Long Does PCI DSS Compliance Take in Mumbai
The timeline will depend on the size and nature of the organization, as well as the quality of the existing security controls. An easy environment will need less time to get things done than a larger company with multiple applications, locations, cloud, third parties and payment mechanisms. The timeline will be influenced by:
- Scope complexity
- Existing security maturity
- Number of gaps identified
- Remediation requirements
- Availability of evidence
- Testing requirements
- Third-party dependencies
- Assessment requirements
Why Start PCI DSS Compliance With a Consultant
PCI DSS requirements can appear straightforward when viewed individually. The difficulty often comes from understanding how those requirements apply to an organisation’s actual environment. A consultant can help your team:
- Define the correct scope
- Understand applicable requirements
- Identify security gaps
- Prioritise remediation
- Prepare required documentation
- Organise evidence
- Coordinate with relevant stakeholders
- Prepare for assessment
- Avoid common compliance mistakes
Why Choose Global Quality Services
Global Quality Services brings more than 26 years of global consulting expertise in quality, information security, and compliance management systems. Here are reasons why leading companies trust us for PCI DSS Certification in Mumbai:
- Experienced Compliance Consultants: The experienced compliance consultants at GQS have over 26 years of experience in quality, information security, and compliance consultation. GQS Bangalore
- Mumbai-Based Assistance: We assist organizations that operate within the Mumbai corporate and technology ecosystem, such as those in
- financial services, fintech, IT, e-commerce, and any other industry that requires payment security.
- Business-Led Assistance: Rather than simply supplying you with a list of items, we help your organization identify the changes that need to be made and why.
- Assistance From Gap Analysis To Assessment Preparation: The consultants at GQS can help at all stages of the compliance process, from the gap analysis stage to preparing your organization for an assessment.
- Experience Through Multiple Security Frameworks: GQS operates through multiple information security and compliance frameworks. The benefit of such experience may come in handy for companies trying to handle PCI DSS in conjunction with other customer, contractual, or information security policies.
- Documentation Support: Well-designed security controls always require the right amount of evidence. GQS assists organizations in structuring their policies and documentation in order to comply with compliance policies.
- Consultation Driven by the Client: Every company has its own payment landscape. That is why our consultation is tailored towards each individual organization and not driven by checklists only.
Get Expert PCI DSS Consulting in Mumbai
Move From PCI DSS Gaps to Assessment-Ready Controls. Protect payment data with a structured PCI DSS compliance approach built around your actual systems, scope, and business requirements. Contact GQS today for a PCI DSS consultation in Mumbai, share your payment environment and compliance requirements, and our team will guide you on the appropriate next steps and commercial engagement.
Frequently Asked Questions
1. What is the purpose of PCI DSS Certification in Mumbai?
It helps organizations secure payment data, ensuring protection from theft and fraud while complying with global data protection requirements.
2. Is PCI DSS v4.0.1 currently applicable?
Yes. PCI DSS v4.0.1 is the current active version of PCI DSS. PCI DSS v4.0 was retired at the end of 2024.
3. What is the difference between PCI DSS compliance and certification?
PCI DSS compliance means meeting the applicable requirements. The term ‘certification’ is commonly used in the market, but PCI SSC does not issue a generic PCI DSS certificate. Official compliance documentation includes forms such as the ROC, AOC, and SAQ.
4. Can a SaaS company in Mumbai need PCI DSS compliance?
Yes. A SaaS provider can have PCI DSS responsibilities if its services store, process or transmit cardholder data or can affect the security of a customer’s cardholder data environment.
5. Does PCI DSS cover cloud environments?
Cloud infrastructure can be relevant to PCI DSS when it forms part of or can affect the security of the cardholder data environment. The exact scope depends on the organisation’s architecture and payment data flows.